Technical Tip: FortiSASE support in steering bypass destination in SSL VPN mode
| Description | This article describes FortiSASE support in steering bypass destination in SSL VPN mode. |
| Scope | FortiSASE. |
| Solution | As per Steering bypass destinations in the FortiSASE admin guide:
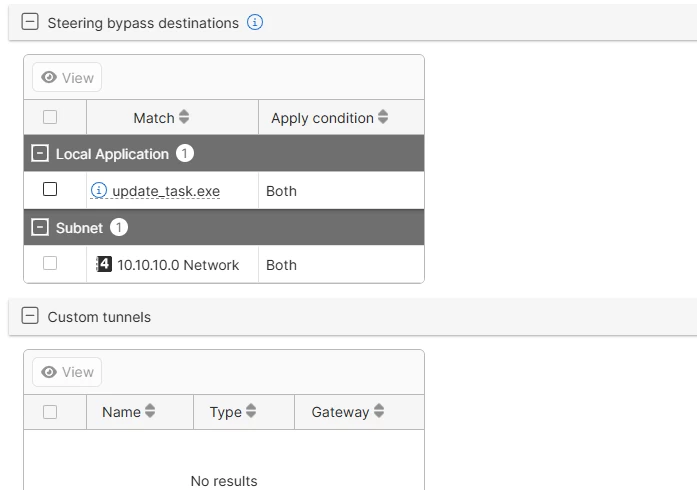
For subnet-based destinations, the Apply condition option is only available on FortiSASE instances with IPsec VPN remote user connectivity.
However, this feature is available for SSL VPN users only under Endpoint Management -> Endpoint Profiles -> Default Profile.
Refer to the following screenshot:
This is applicable for both the feature and mature versions of FortiSASE. |