

Saundraraju
Staff
Staff
August 12, 2026

Technical Tip: Deny traffic for policy name 'Block-Internal-Subnets' in Internet access traffics logs

  • August 12, 2026
  • 0 replies
  • 53 views

Description

The article describes the Block-Internal-Subnet Internet traffic logs in FortiSASE, and limitations regarding them.

Scope

FortiSASE v26.1.1.

Solution

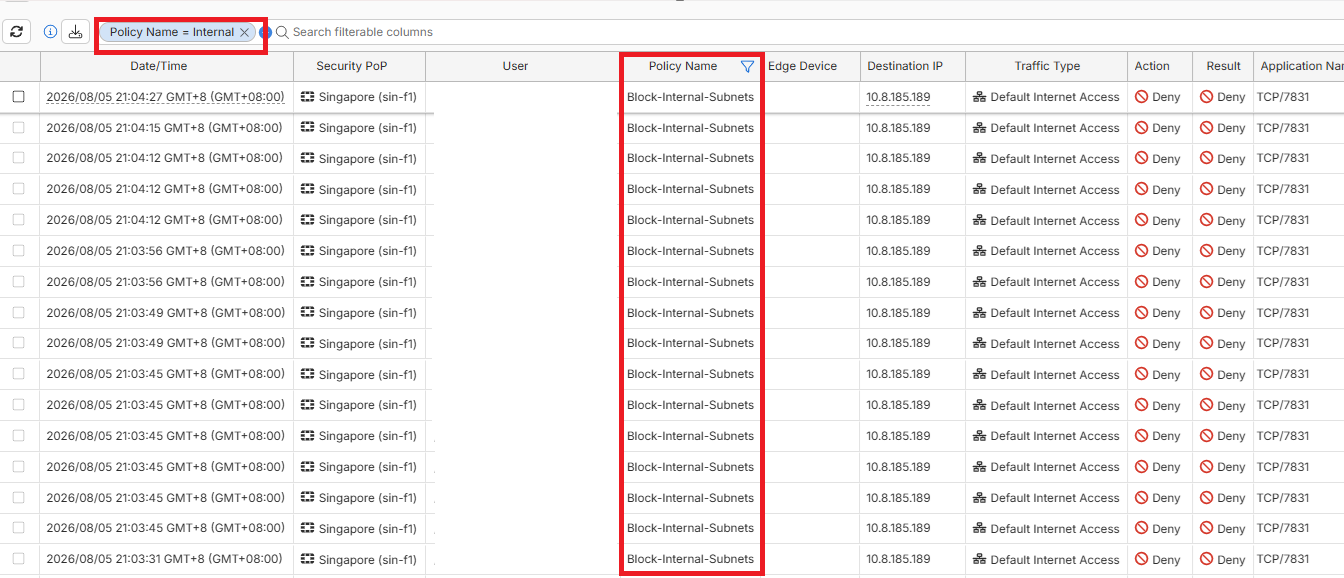
The snapshot below shows an example of Internet traffic logs where Block-Internal-Subnet policy name was matched.
f83e9971.png


Block-Internal-Subnets policy is an internal FortiSASE policy that restricts internet traffics to subnets 10.8.0.0/16 and 10.16.0.0/16 from FortiSASE endpoints.

The policy is hidden in the FortiSASE portal as it is an internally managed policy, and administrators do not have control over this policy.

However, this policy restriction does not apply to the Secure Private Access (SPA) connection. Customers can still access internal resources within the same subnets (10.8.0.0/16 and 10.16.0.0/16) through SPA traffic.

Thought Leadership Security Summit. Outpace New Threats with AI - enhanced defense. Tuesday, Septmeber 15, 8:30 AM - 2:30 PM PT. The Golf Club at Newcastle, WA.
Virtual event | September 2026. SASE summit. The age of autonomous trust. Register here!

