ihaidar
Staff
Staff
May 15, 2025 12:36 PM UTC

Technical Tip: Configuring SWG SSO with Internal IDP behind SPA Tunnel

Description This article describes the requirements and process of configuring SWG SSO when the IDP is behind the SPA Tunnel.
Scope FortiSASE.
Solution

To configure SWG SSO when IDP is behind SPA, its needed to configure the following:


  1. SWG SSO Configuration, refer to the below article for detailed steps: Configuring FortiSASE with Entra ID SSO in SWG agentless mode.


  1. It is necessary to configure deep inspection on both SIA and SPA policies:

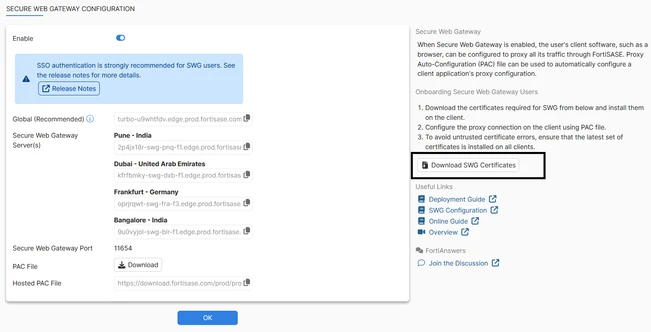
    1. Download the certificate from FortiSASE and install it on the client machine.
       Untitled.png

    2.  


      Configure deep inspection profiles for SIA and SPA.
    3. Add the profiles to SIA and SPA policies. 

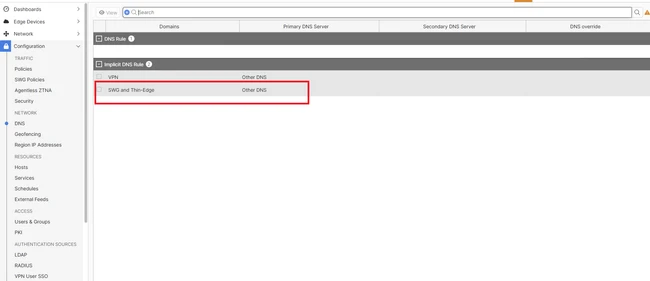
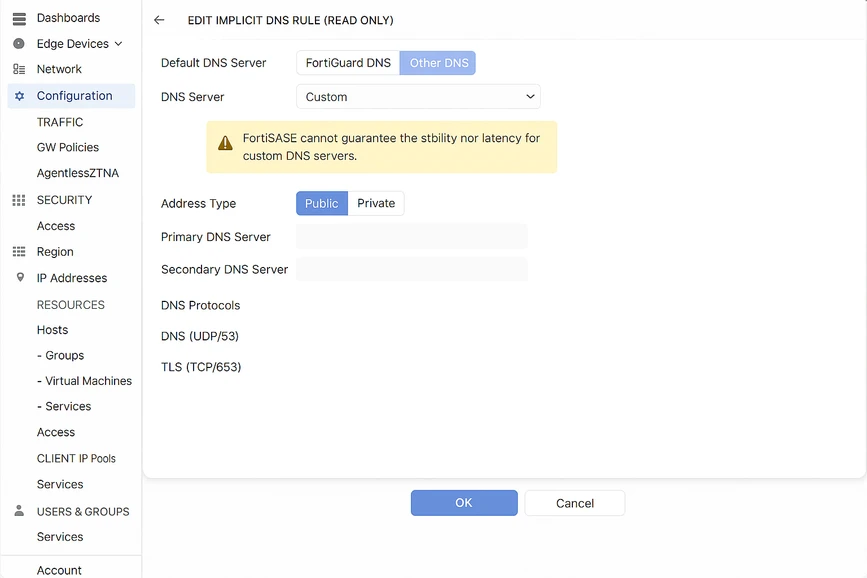
  1. Follow the screenshots below, configure the DNS, and choose the private DNS able to resolve the internal IDP.

DNS1.png


Select 'private' and add the internal DNS servers.

DNS config 2.png


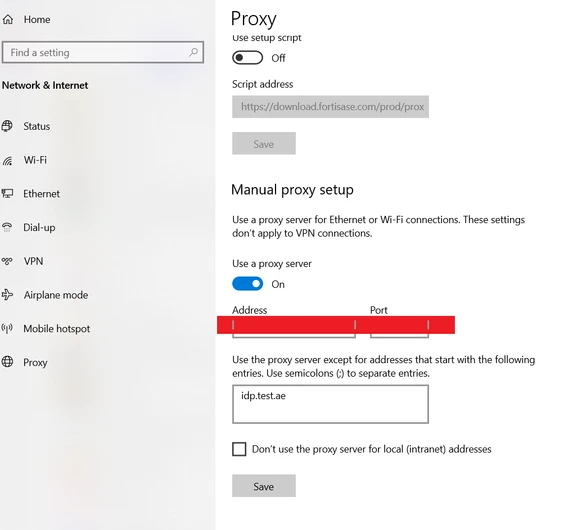
  1. Exempt the IDP URL from the client Machine as shown below:


Exempt.png


    Thought Leadership. Security Summit. Thursday, November 12th, PGA National Resort, Palm Beach Gardens, FL.
    Security Operations Summit: Modernize SecOps. Operate AI-Native.AMER: November 4 | 9:00 AM PST. India and SAARC: November 5 | 10:00 AM IST. EMEA: November 5 | 10:30 AM CET. APAC: November 5 | 11:00 AM SGT