



Technical Tip: How to configure traffic shaping on explicit web proxy interface
Description
This article describes how to configure the traffic shaping on the web proxy interface to limit users traffic.
Scope
Fortiproxy v7.0
Solution
Use the following method to create a traffic shaper profile with a class ID in the GUI:
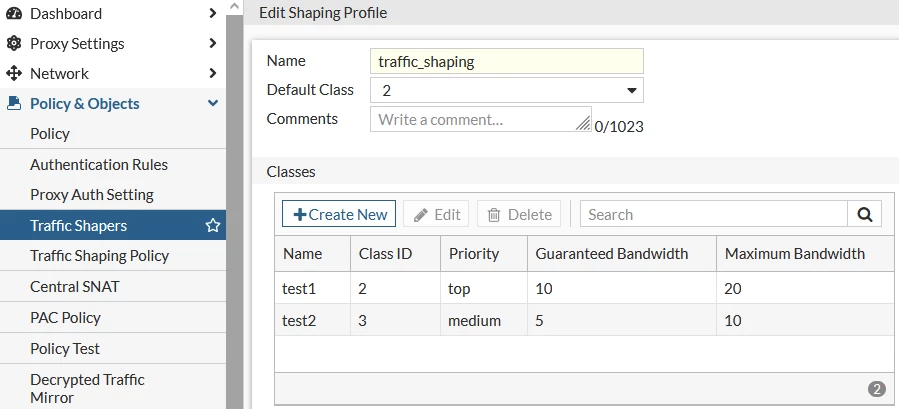
To configure it in the CLI:
config firewall shaping-profile
edit "traffic_shaping"
set default-class 2
config classes
edit "test1"
set class-id 2
set guaranteed-bandwidth 10
set maximum-bandwidth 20
next
edit "test2"
set class-id 3
set priority medium
set guaranteed-bandwidth 5
set maximum-bandwidth 10
next
end
next
end
Configure traffic shaping on the interface with an explicit web proxy enabled in the GUI:
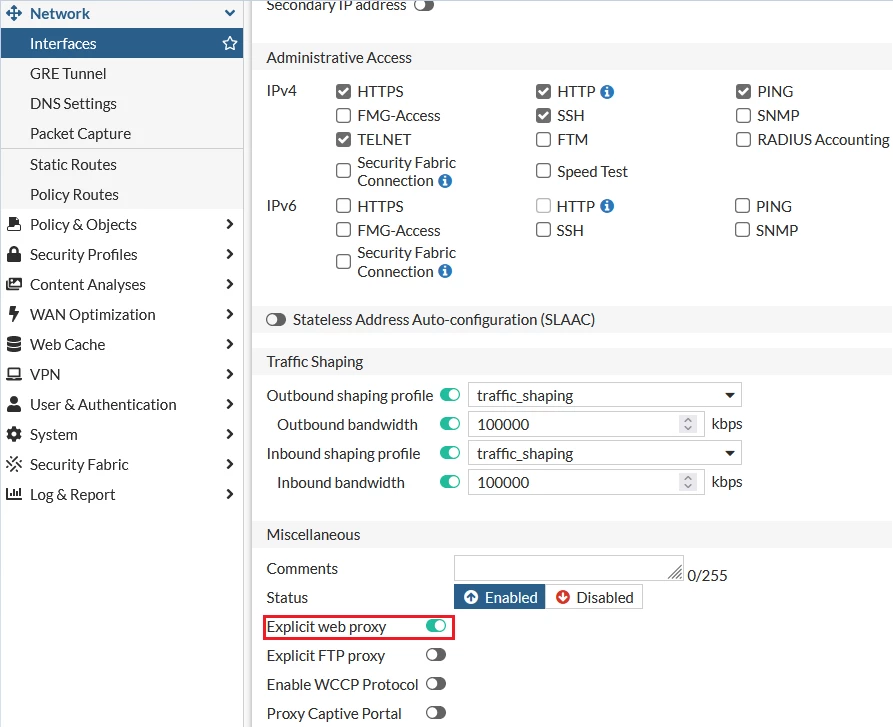
To configure it in the CLI:
config system interface
edit "port2"
set ip 10.211.1.110 255.255.252.0
set allowaccess ping https ssh http telnet
set type physical
set explicit-web-proxy enable
set inbandwidth 100000
set outbandwidth 100000
set egress-shaping-profile "traffic_shaping"
set ingress-shaping-profile "traffic_shaping"
set snmp-index 2
next
end
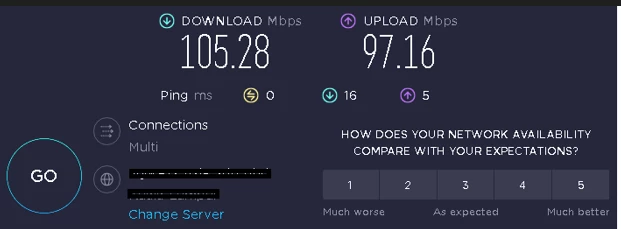
Speedtest result before traffic shaping applies:
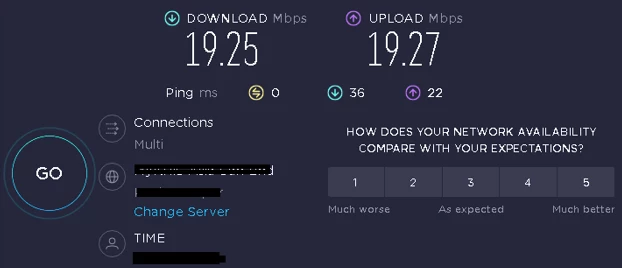
Speedtest result after traffic shaping applies:
More information:
To create or edit a class, see Create or edit a class.
For an alternative way to configure Traffic shaping with a Traffic shaping policy, see traffic shaping policy.
If an explicit proxy interface is defined in the policy and the traffic needs to be controlled as local-in or local-out using traffic shaping, follow the procedure in Local-in and local-out traffic matching.

