Technical Tip: FortiProxy is not connecting to FortiManager with incorrect certificate message
| Description | This article describes an issue in which the hardware FortiProxy devices are not able to connect to the FortiManager. |
| Scope | FortiProxy versions 7.4 and 7.6. |
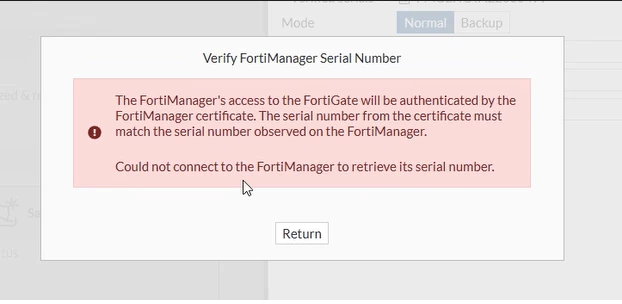
| Solution | A Physical or hardware FortiProxy device can not connect to the FortiManager when the Technical Tip: How to integrate FortiProxy with FortiManager article is followed. The GUI shows the error below in FortiProxy.
The FortiManager debug shows that the FortiProxy is sending the certificate with the incorrect CN, and it does not match the serial Number of the FortiProxy.
kvm74 # diagnose debug timestamp enable kvm74 # diagnose debug application fgfmsd -1 kvm74 # diagnose debug enable
2026-02-03 13:01:09 get auth
2026-02-03 13:01:10 FGFMs(probing...): Cleanup session 0x5642e58b59a0, 10.5.131.8.
As per the FortiProxy, the default Factory certificate shows the CN as 'FortiGate' instead of the serial number of the FortiProxy.
FPX2KE-1 # get vpn certificate local details == [ Fortinet_Factory ]
This issue is seen only for the Hardware or Physical FortiProxy devices, and it is fixed in version 7.4.9 of FortiProxy as part of issue ID 1143143.
One of the workarounds for the issue is to set a custom certificate for the communication between the FortiProxy and FortiManager instead of using the Factory default certificate. Refer to the article Technical Tip: Utilizing factory and custom certificates in tandem for the FortiGate-to-FortiManager (FGFM) protocol. |