Technical Tip: How to disable ZTNA Control from the CLI to restore FortiPAM GUI Access
| Description | This article describes how to restore FortiPAM GUI access by modifying the access-proxy configuration through the CLI when ZTNA Control denies access. |
| Scope | FortiPAM. |
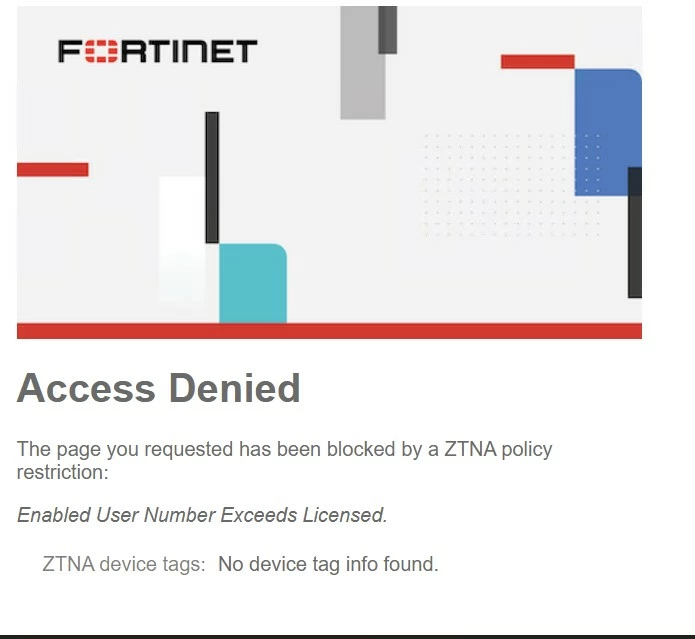
| Solution | Access to the FortiPAM GUI can be denied if ZTNA Control is enabled without completing the FortiClient EMS Fabric connector configuration. In this scenario, the access proxy enforces client certificate verification by allowing only endpoints with matching ZTNA tags.
To resolve the issue using the GUI, disable ZTNA Control in the interface configuration.
Go to System -> Network -> Interface, select the management interface, and disable the ZTNA control option. Refer to the FortiPAM Administration Guide: Editing an interface.
To resolve the issue using the CLI, verify the access proxy configuration and disable client certificate enforcement if it is enabled.
config firewall acess-proxy edit "fortipam_access_proxy" set client-cert disable next end
After applying the configuration, confirm that GUI access is restored. |