



FortiGuard Outbreak Alert: QuickFox Supply Chain Attack
Description | FortiGuard Labs have identified an extended supply chain attack targeting the QuickFox Software. The campaign has reportedly been active since August 2025 before being publicly disclosed in August 2026. QuickFox is a VPN/proxy and gaming-acceleration service primarily used by overseas Chinese users to provide fast, low-latency access back to China-based content and services. The attackers modified the official Windows installer hosted on the QuickFox website, embedding a custom backdoor tracked as FDMTP. |
CVE ID | N/A |
FortiNDR Cloud Coverage | In the QuickFox Supply Chain Attack, the FDMTP implant is downloaded and first connects to a staging domain to retrieve the IP address and port information it will use for subsequent communications. FortiNDR Cloud’s File Analysis feature leverages AV engine and AI-driven analysis to detect the download of the FDMTP loader. 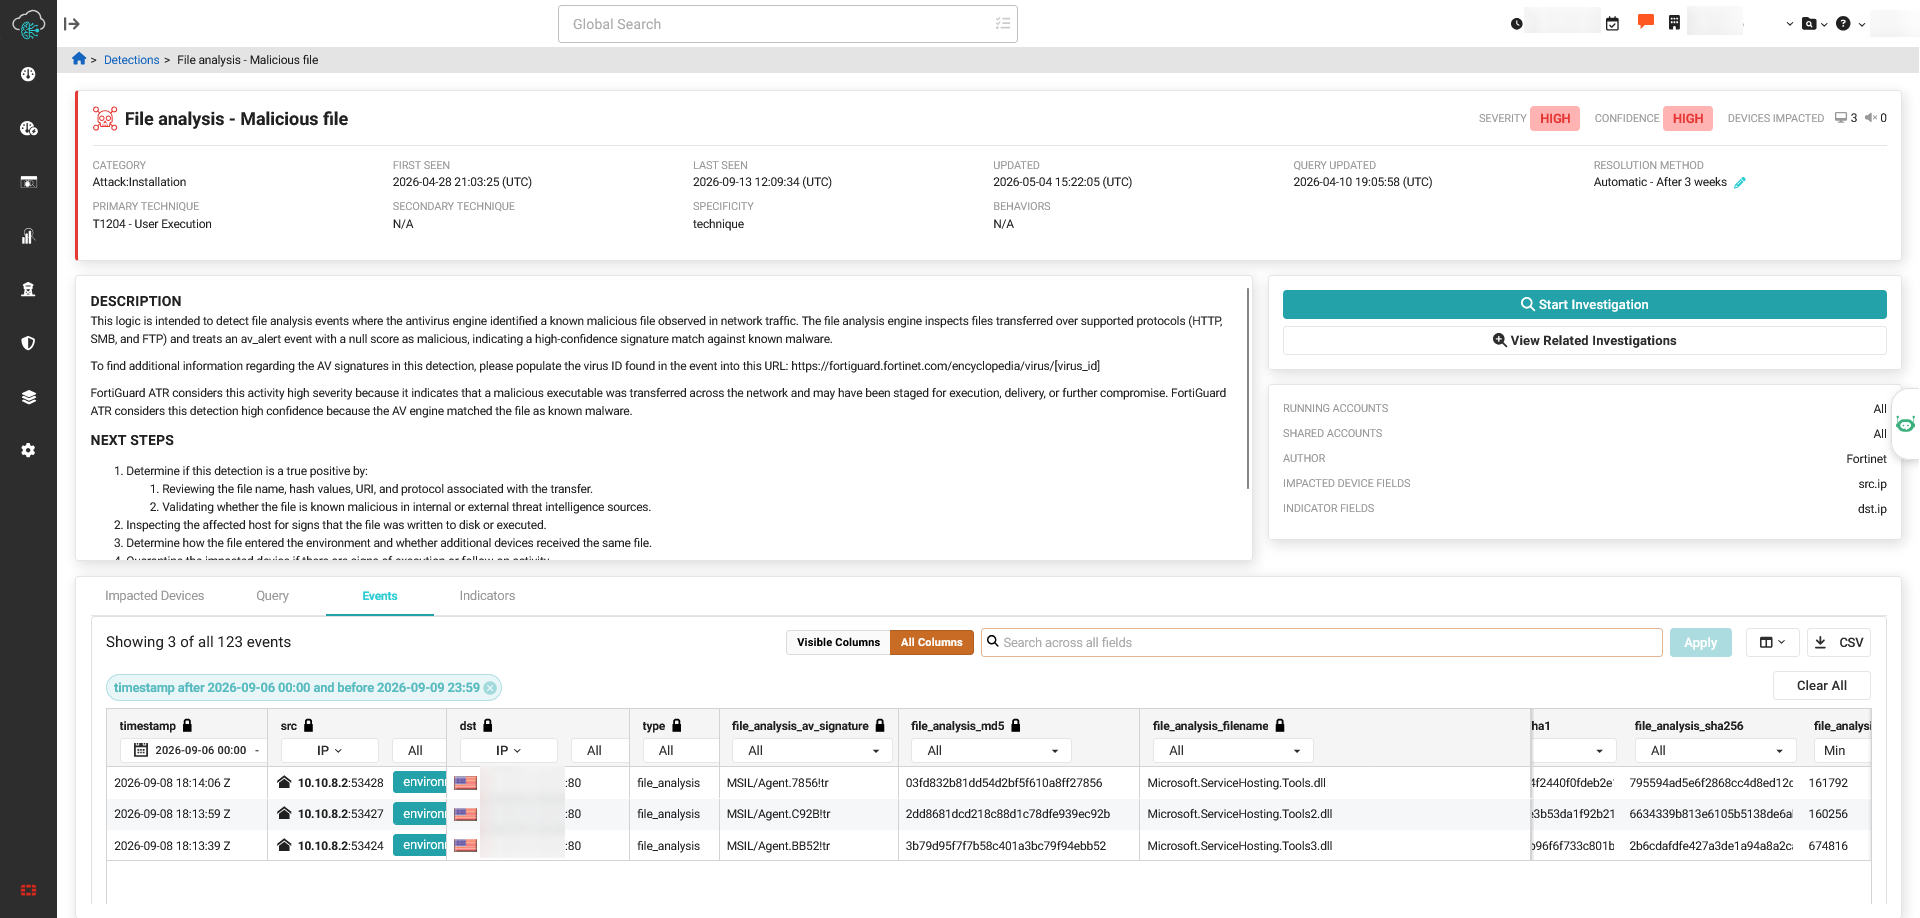 Through behavioral analysis, FortiNDR Cloud identifies the initial staging activity of the FDMTP loader with the detection “SSL Connection to Malicious Domain with Young Age and Newly Seen in Environment.” 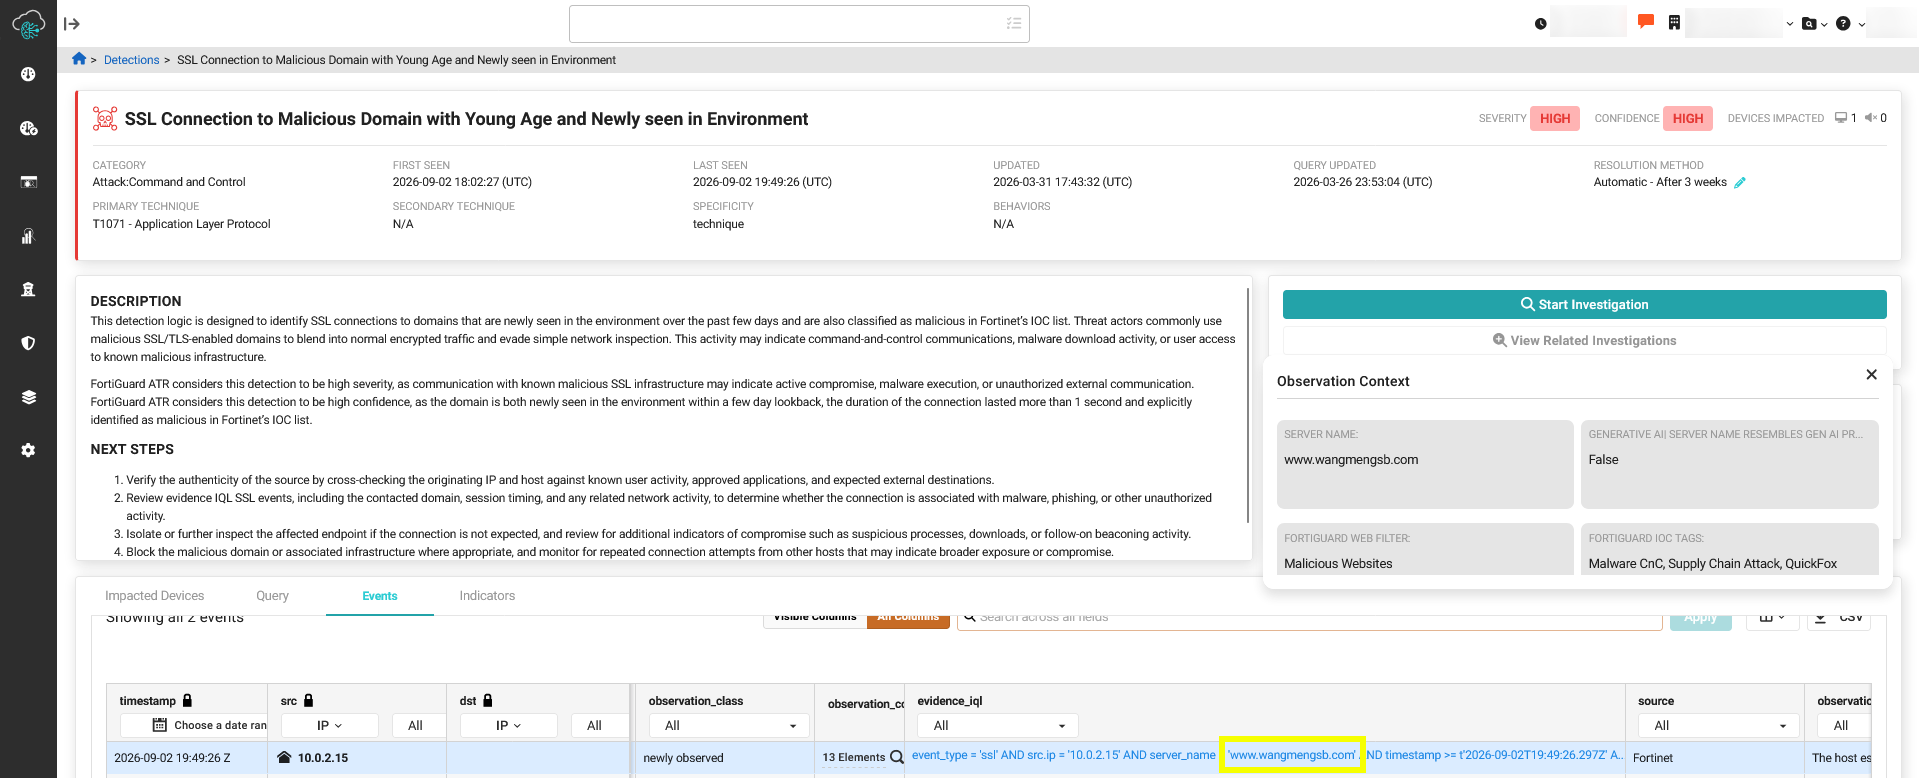 |
Playbook | N/A |
Threat Hunting | FortiNDR Cloud users can use the following IOCs from Fortinet to hunt for "QuickFox Supply Chain Attack" related activities. |
Suricata/DPI Coverage | N/A |
Other Fortinet Products | For more details regarding mitigating the attack by utilizing Fortinet products, please refer to QuickFox Supply Chain Attack. |


