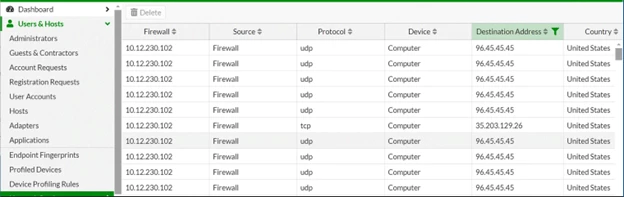
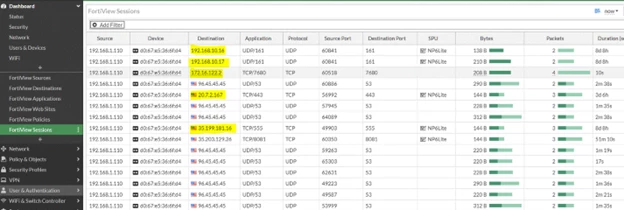
Solution | Verify missing sessions are not included in the API response.
Open a FortiNAC CLI session (configure the application to write output to a text file). Enable the following debug process:
execute enter-shell
nacdebug -name FirewallSessionManager true
In the CLI, enter the following command:
diagnose tail -F output.master
Leave the window open. In the FortiNAC UI, navigate to Network -> Inventory. Right-click the FortiGate model and ensure Set Firewall Session Polling is selected. Select Poll Now, then select OK. The output.master log will list the data returned from the API query.
Log entry example:
yams INFO :: 2024-07-24 10:02:57:307 :: #528 :: PollRunnable-2 FortigateCommon.request from element 10.12.230.102

yams INFO :: 2024-07-24 10:02:57:307 :: #528 :: PollRunnable-2 request uri = https://10.12.230.102:443/api/v2/monitor/firewall/session/select

yams INFO :: 2024-07-24 10:02:57:307 :: #528 :: PollRunnable-2 request details = GET https://10.12.230.102:443/api/v2/monitor/firewall/session/select?seconds=4208&count=500&start=1&global=1 HTTP/1.1

yams INFO :: 2024-07-24 10:02:57:389 :: #528 :: PollRunnable-2 request status = 200, response =
HttpResponseProxy{HTTP/1.1 200 OK [date: Wed, 24 Jul 2024 14:03:12 GMT, set-cookie: session_key_443_59af7de9="8y48G915Qkx8qtf7QbmbcyzGj7dbj7"; path=/; secure; SameSite=Strict, x-frame-options: SAMEORIGIN, content-security-policy: frame-ancestors 'self', x-xss-protection: 1; mode=block, cache-control: no-cache, must-revalidate, content-type: application/json, Connection: keep-alive] org.apache.http.client.entity.DecompressingEntity@2f3bbe1}
If the following error was displayed in the output.master while parsing the FortiGate firewall sessions, then upgrade the FortiNAC to v7.6.7 GA:
=238), command: (HGET), promise: java.util.concurrent.CompletableFuture@37797fc3[Not completed, 1 dependents], params: [RC:FWMCC:byMac, PooledUnsafeDirectByteBuf(ridx: 0, widx: 19, cap: 256)]
com.fasterxml.jackson.databind.exc.InvalidDefinitionException: Cannot construct instance of com.bsc.cache.hibernate.FirewallSessionManagerConnectionCache$DynamicConnectionContainer: non-static inner classes like this can only by instantiated using default, no-argument constructor
In the following:
192.168.1.110 is the source IP. 96.45.45.45 is the destination IP. 10.12.230.102 is the firewall IP.
yams INFO :: 2024-07-24 10:02:57:389 :: #528 :: PollRunnable-2 request response = [
{
"http_method":"GET",
"results":{
"details":[
{
"type":"ipv4",
"proto":"udp",
"srcintf":"lan",
"saddr":"192.168.1.110",
"sport":54926,
"srcmac":"d0:67:e5:36:6f:d4",
"dstintf":"wan1",
"daddr":"96.45.45.45",
"dport":53,
"src_uuid":"17720c1a-c464-51ee-b446-f1c7b069aa40",
"src_uuid_type":"firewall.address",
"dst_uuid":"17720c1a-c464-51ee-b446-f1c7b069aa40",
"dst_uuid_type":"firewall.address",
"country":"United States",
"country_id":21333,
"snaddr":"10.12.230.102",
"snport":54926,
"policyid":1,
"policytype":"policy",
"vf":"root",
"expiry":"155",
"duration":24,
"apps":[
{
"id":0,
"name":"udp\/53",
"protocol":17,
"protocol_str":"udp",
"port":53
}
],
"app_list_id":0,
"sentbyte":79,
"rcvdbyte":141,
"tx_packets":1,
"rx_packets":1,
"tx_shaper_drops":0,
"rx_shaper_drops":0
},
<…>
Once polling is complete, press Ctrl+C to stop the tail. Search the log for the Destination IP(s) missing in the FortiNAC UI. If the IP addresses are present in the response but are not listed in the FortiNAC UI, contact support for further investigation. Provide the following:
Related article:
Technical Tip: FortiNAC - FortiGate firewall session polling
|