Technical Tip: Unable to re-build FortiNAC High Availability 'WARNING: REMOTE HOST IDENTIFICATION HAS CHANGED!'
| Description | This article describes how to re-build FortiNAC High Availability after breaking the HA and a factory reset secondary FortiNAC HA node. The assumption is that the node is already factory reset for some reason, and the HA cannot rebuild. Steps 1+2 will show how this situation is created in the first place. |
| Scope | FortiNAC-F v7.2.6, v7.4.1, v7.6.0 or greater and FortiNAC 9.4.X (CentOS) |
| Solution | Steps to be followed:
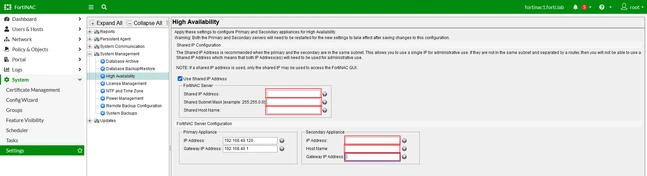
execute factoryreset all-setting
Solution:
On FortiNAC v7.2.6, v7.2.7:
execute ssh-known-hosts remove-host ha <secondary-NAC-IP> On FortiNAC version 7.4.0 and above:
execute ssh-known-hosts show current-user <secondary-NAC-IP> execute ssh-known-hosts remove-host current-user <secondary-NAC-IP>
Note: On FortiNAC v7.2.5 and lower, change the IP of the Secondary Node or upgrade to FortiNAC v7.2.6 or greater.
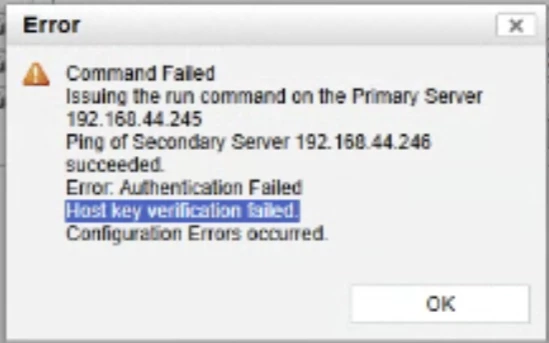
On FortiNAC v9.4.8 (CentOS) and lower: Follow the solution below when a new FortiNAC appliance is being deployed and the following error appears when trying to save HA settings on the Primary NAC Appliance GUI:
"Command Failed. Issuing the run command on the Primary Server 192.168.44.245. Ping of the Secondary Server 192.168.44.246 succeeded. Error: Authentication Failed. Host key verification failed. Configuration Errors occurred".
Notes:
Step 1: Check for SSH keys entries currently added for the IP address on each FortiNAC appliance in the known_hosts file:
cat /root/.ssh/known_hosts
Step 2: Manually add the Secondary FortiNAC SSH key missing in the Primary FortiNAC Known Hosts list:
Notes: When the system prompt if want to continue, type "yes".
Step 3: Manually add the Primary FortiNAC SSH key missing in the Secondary FortiNAC Known Hosts list:
Notes: When the system prompts the user to confirm whether to continue, enter 'yes'.
Step 4: Re-apply the HA settings from the Primary FortiNAC GUI by navigating to System -> Settings -> System Management -> High Availability -> Save Settings. |