scitlak
Staff
Staff
August 17, 2025

Technical Tip: How to send CoA re-authentication request to Cisco WLC

  • August 17, 2025
  • 0 replies
  • 998 views
Description This article describes how to configure FortiNAC to send a custom CoA request to Cisco WLC for re-authentication.
Scope FortiNAC -F 7.4, FortiNAC -F 7.6.
Solution

In some circumstances, while Cisco WLC receives a CoA disconnect (RFC 5176) message, Cisco WLC disconnects the host; however, it does not send any new RADIUS authentication requests for the same host. In these circumstances, FortiNAC can be configured to send a CoA Re-Authentication request with the required RADIUS VSA.


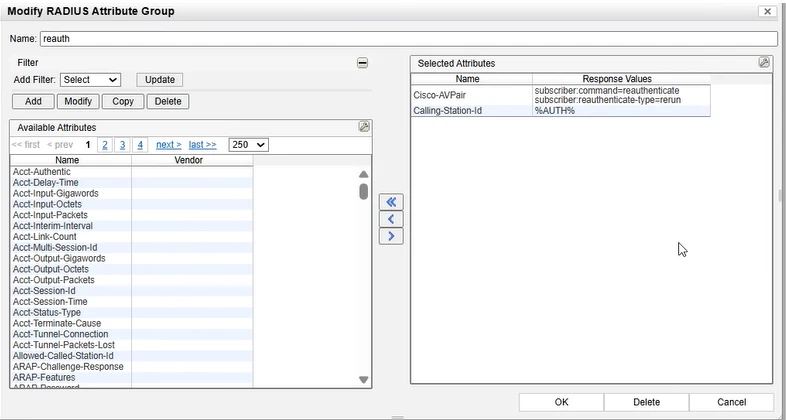
  1. Create a new RFC Attribute group under Network -> RADIUS -> Attribute Groups by using the Cisco RADIUS VSAs below. In addition to the Cisco VSAs shown below, add the 'Calling-Station-id' attribute as a session identifier that is required by Cisco.

Cisco:Avpair=“subscriber:command=reauthenticate”
Cisco:Avpair=“subscriber:reauthenticate-type=rerun”


04.08.2025_15.08.00_REC.png


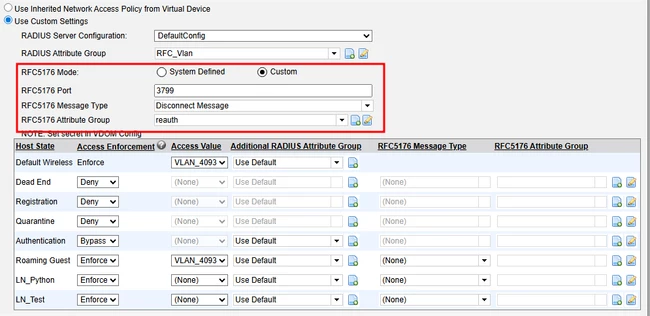
  1. Navigate to SSID configuration and change the RFC5176 Mode to Custom and select the RFC5176 Attribute Group for the newly created RFC Group.


04.08.2025_15.13.35_REC.png


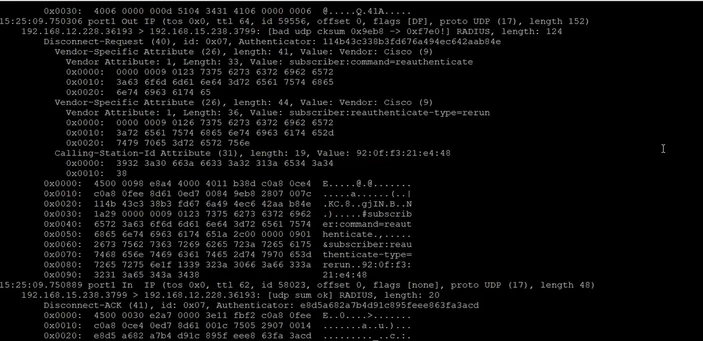
  1. Create a circumstance so that FortiNAC can send a CoA Disconnect message, like Guest Self-Registration, and test the CoA disconnect message.


04.08.2025_15.15.54_REC.png

    Thought Leadership. Security Summit. Thursday, November 12th, PGA National Resort, Palm Beach Gardens, FL.
    Thought Leadership. Security Summit. Thursday, October 8th. Disney's Grand Californian Hotel & SPA, Anaheim, CA.
    Security Operations Summit: Modernize SecOps. Operate AI-Native.AMER: November 4 | 9:00 AM PST. India and SAARC: November 5 | 10:00 AM IST. EMEA: November 5 | 10:30 AM CET. APAC: November 5 | 11:00 AM SGT