scitlak
Staff
Staff
January 23, 2025

Technical Tip: How to configure FortiNAC to set host role by using MSCHAPv2 Machine Authentication

  • January 23, 2025
  • 0 replies
  • 619 views
Description This article describes how to configure FortiNAC to retrieve the LDAP Group membership of a host by using MSCHAPv2 Machine based authentication and to set a host role depending on a host LDAP Group membership.
Scope FortiNAC-F v7.6.
Solution
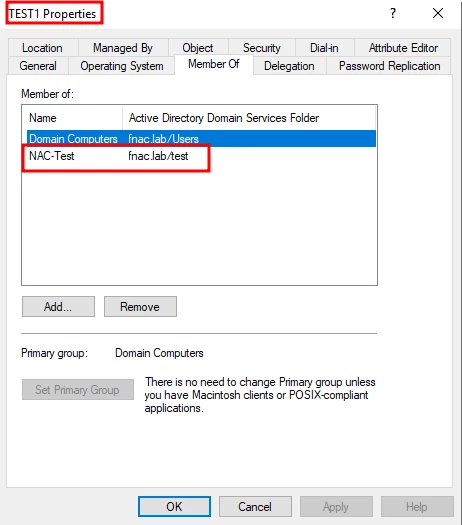
  1. Set the host as a member of one LDAP security group.

    23.01.2025_15.26.04_REC.png
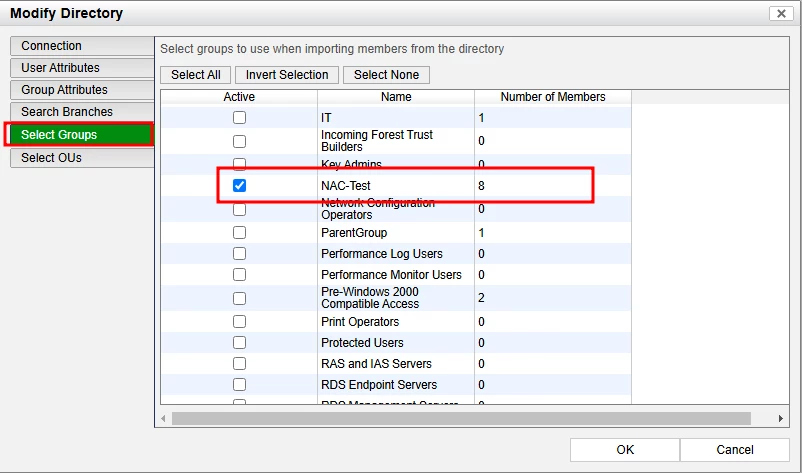
  2. Select the LDAP security group in FortiNAC under System -> Settings -> Authentication -> LDAP.

    23.01.2025_15.26.26_REC.png
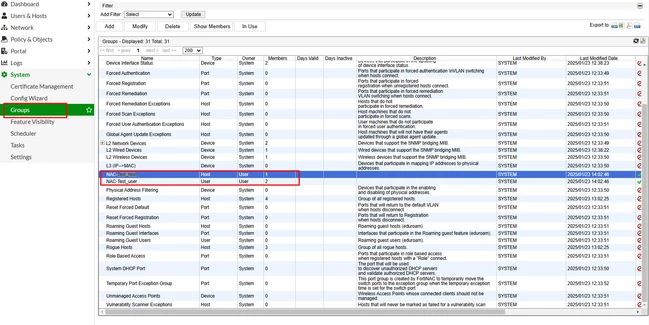
  3. The FortiNAC -F 7.6 creates two groups for the LDAP group under Settings -> Groups. One of them will have a type host and the other one user.

    23.01.2025_15.45.41_REC.png

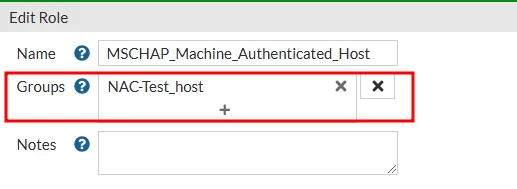
  4. Create a Role under Policy & Objects -> Roles and add the LDAP retrieved group in Groups.

    23.01.2025_15.27.10_REC.png
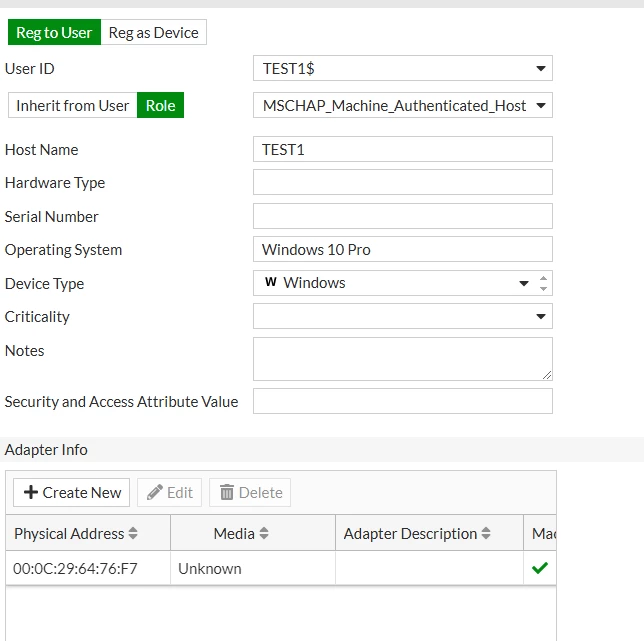
  5. Whenever the host performs an MSCHAPv2 machine-based authentication, FortiNAC will retrieve the LDAP group membership of the host and set the appropriate role.

    23.01.2025_15.56.54_REC.png

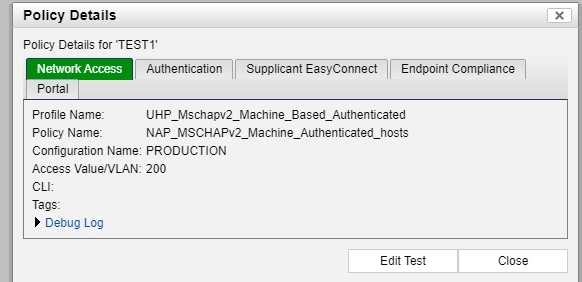
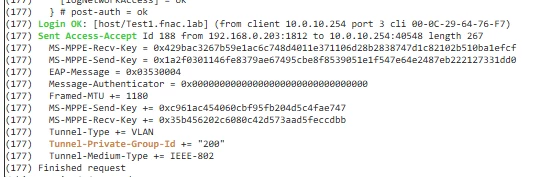
  6. When a User Host Profile is created with the correct host Role criteria, the host matches the Network Access Policy and FortiNAC assigns the correct VLAN ID.


23.01.2025_15.27.36_REC.png


23.01.2025_15.28.16_REC.png


23.01.2025_15.28.40_REC.png


Related articles:
Technical Tip: Groups imported in FortiNAC does not show any Members listed
Technical Tip: Leveraging Domain Group Membership of Client with EAP-TLS Computer-Based Authentication 

    Thought Leadership Security Summit. Outpace New Threats with AI - enhanced defense. Tuesday, Septmeber 15, 8:30 AM - 2:30 PM PT. The Golf Club at Newcastle, WA.
    Virtual event | September 2026. SASE summit. The age of autonomous trust. Register here!