Technical Tip: Groups imported in FortiNAC does not show any Members listed
| Description | This article describes that LDAP Groups imported to FortiNAC do not show any members listed. |
| Scope | FortiNAC, FortiNAC-F. |
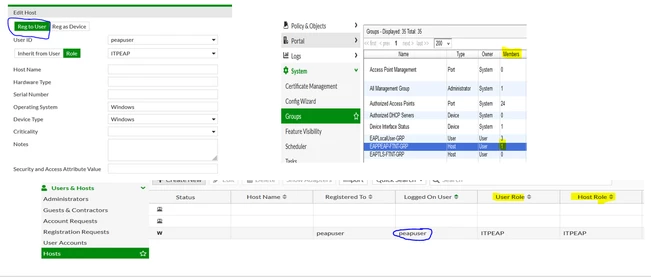
| Solution | After importing LDAP groups into FortiNAC, the Group members under System -> Groups show as '0' (Zero), once a host is registered as a User 'Reg to User' in Hosts view with a domain user account. The members' values will change.
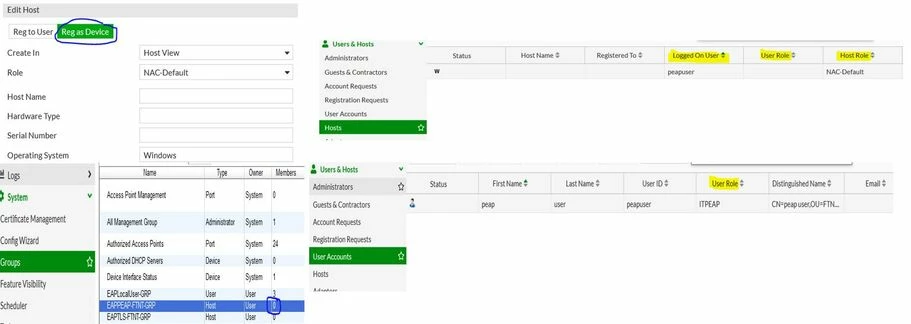
With dot1x Machine/computer Authentication (FortiNAC-F), the Host is 'Reg as Device', and even after dot1x User Authentication the authenticated machine will remain as 'Reg as Device'. Even though the Members value remains '0' FortiNAC will still leverage from LDAP groups in the User/host Profiles, but the user will not appear as a member under System -> Groups (This is an expected behavior).
After FortiNAC automatically imports LDAP groups under System -> Groups, the Group Member Type: Host. (The Group member type will show as Host). Related articles: Technical Tip: FortiNAC v7.6 LDAP group membership based on 'User' or 'Device' type Registration Technical Tip: Role assignment orderTechnical Tip: Using the same host to dynamically change network policies via ‘logged on user’ from LDAP roles |