



Troubleshooting Tip: FortiNAC fails to move rogue switches to registration VLAN
Description
This article describes how to solve an issue where FortiSwitch fails to move rogue switches to the registration VLAN.
Scope
FortiNAC.
Solution
When a switch fails to move rogues to the registration VLAN, check the following:
- SNMP v1 link state or Mac Notification traps are being sent by the switch to FortiNAC.
In FortiNAC this can be validated by enabling the following debugs in CLI.
- FortiNAC (CentOS).
logsnacdebug -name SnmpV1 truenacdebug -name DeviceInterface truenacdebug -name BridgeManager truenacdebug -name TrapHandler truetf output.master | egrep -i "received\|MAC notification" - FortiNAC-F (NACOS).
diagnose debug plugin enable SnmpV1diagnose debug plugin enable DeviceInterfacediagnose debug plugin enable BridgeManagerdiagnose debug plugin enable TrapHandlerdiagnose tail -F output.master | grep -i "received\|MAC notification"
The output will filter for the provided strings that are the trap received events.
Example logs in FortiNAC output.master for MAC traps:
FortiSwitch MAC Notification received for FortiGateLAB:root:SwitchNAME:port3, operation = ADD, vlanId = 60, mac = 00:0C:29:XX:XX:XX, port ifIndex = 3
yams.DeviceInterface FINER :: 2024-05-02 14:57:21:271 :: #69 :: DeviceServer.processMACNotifcation(): passing 1 MAC Notifications from device IP 192.168.1.254 to BridgeManager
yams.BridgeManager FINER :: 2024-05-02 14:57:21:271 :: #69 :: BridgeManager.handleMACNotifications processing 1 notifications
yams.BridgeManager INFO :: 2024-05-02 14:57:21:271 :: #69 :: MAC Notification:
Port Description = FortiGateLAB:root:SwitchNAME:port3
MAC Address = 00:0C:29:XX:XX:XX
VLAN = 60
Operation = ADD
- Traps are being sent from the same IP address as is modeled in inventory view (Elements tab).
The switch model configuration is set up with the Registration VLAN defined.
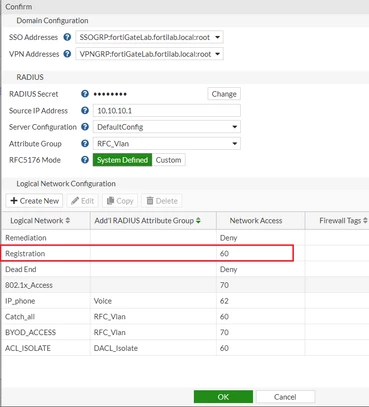 Figure 1. Registration Logical network has a Network access value defined.
-
The VLAN defined in the model configuration is created in the switch.
-
Topology Port View in FortiNAC shows the host connected to the correct port.
-
The host is displayed as a rogue in FortiNAC.
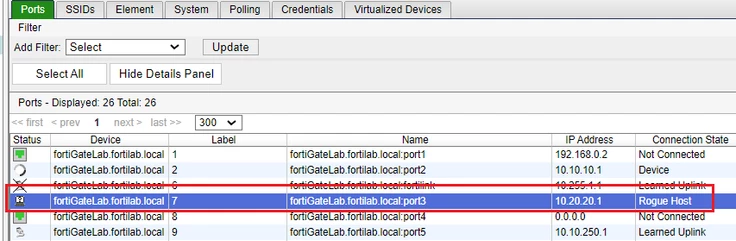 Figure 2. Rogue connected to port3 in enforced port.
- Communication is successful (SNMP and SSH) between FortiNAC and the switch (Validate Credentials).Go to the respective device in Inventory view -> Credentials and select 'Validate Credentials'.If there is a failure in CLI credentials, the issue must be resolved before proceeding with any other configuration or change in FortiNAC.
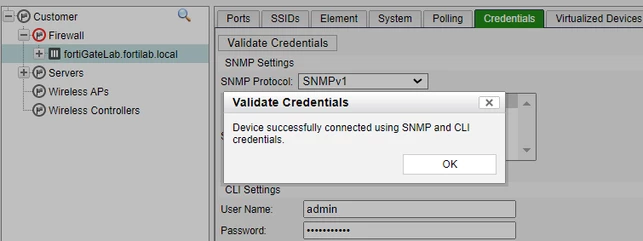 Figure 3. Validation of credentials show success for both SNMP and CLI.
- Port is part of the 'Forced Registration' system group.
'Right-click' the port in the Inventory view on respective device and select 'Group Membership'. Select 'Forced Registration'. 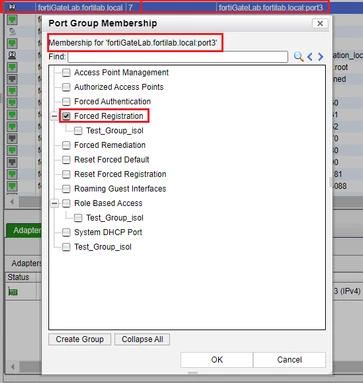 Figure 4. Port is made member of "Forced Registration" system group.
Related articles:
- Technical Tip: Comprehensive guide for a simple FortiNAC deployment
- Technical Tip: 'State based Control' concept and VLAN changes
- See Technical Tip: Wired Enforcement groups for information about Wired Enforcement groups.


