



Technical Tip: Troubleshooting Palo Alto single sign on
Description
Scope
FortiNAC and Palo Alto.
Solution
- While the client is connected, navigate to Users & Hosts -> Hosts view in the Administration UI and verify the User ID is reflected as the logged-on user.
- If logged on User ID is displayed, 'right-click' on the host record and select Policy Details.
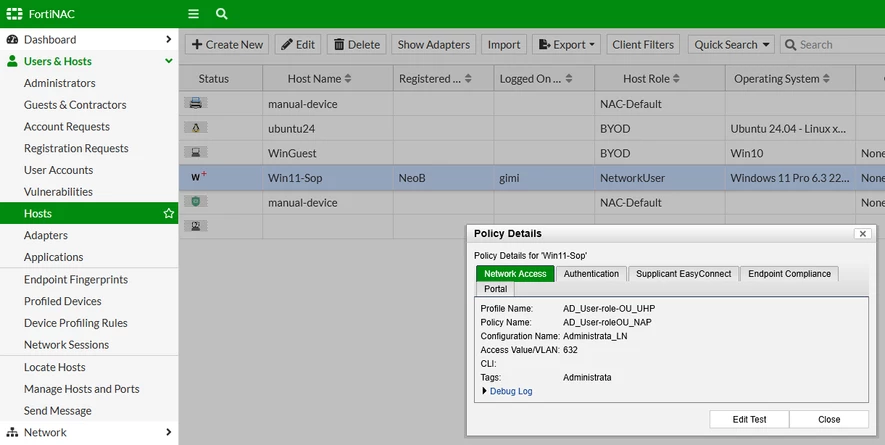
- Verify the correct Network Access Policy matches. This is required; for details, see the related KB article below.
- If the policy is correct, check Palo Alto and verify User ID and IP address are listed.
- If the User ID is not present in Palo Alto, verify FortiNAC is sending the information. Log in to the appliance CLI.
- Enable Palo Alto integration to debug and execute the following command:
nacdebug -name SSOManager true
- Tail output.master log to a separate file. Type
tail -F /bsc/logs/output.master > /bsc/logs/PaloAltoSSOTest.txt
- Have the user logoff and logon to the network.
- Type Ctrl-C to stop tail.
- Check /bsc/logs/PaloAltoSSOTest.txt to verify the IP/Usernames have been sent to Palo Alto.
Example output:
PaloAlto UserIDMessage( 10.34.24.153:jsmith )
Verify that the end host has a valid IP and FortiNAC can read it (usually through L3 polling) and is matching with the subnets configured in the 'SSO Addresses' field under Palo Alto 'Model Configuration' in FortiNAC.
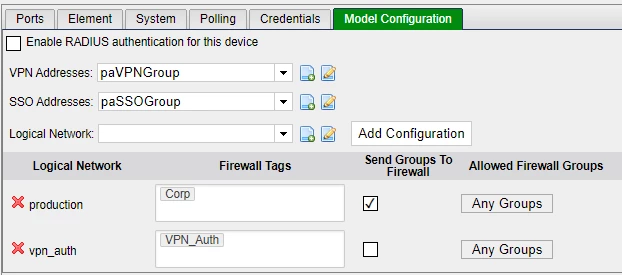
If the subnet does not match, the debug output will be similar to:
2026-01-21 10:10:10.506 +0100 [pool-6-thread-1] DEBUG yams.SSOManager - SSOManager.testAdapterPerAgent logical network = Administrata
2026-01-21 10:10:10.506 +0100 [pool-6-thread-1] DEBUG yams.SSOManager - SSOManager.testAdapterPerAgent no change in logical network Administrata for adapter 01:23:44:AB:CD:EF
2026-01-21 10:10:10.506 +0100 [pool-6-thread-1] DEBUG yams.SSOManager - SSOManager.testAdapterPerAgent process = true agent type = PALOALTO
2026-01-21 10:10:10.506 +0100 [pool-6-thread-1] DEBUG yams.SSOManager - SSOManager.testAdapterPerAgent getting targets for 10.10.60.11
2026-01-21 10:10:10.506 +0100 [pool-6-thread-1] DEBUG yams.SSOManager - SSOManager.getSSOTargetList getting targets from DeviceInterface for 01:23:44:AB:CD:EF 10.10.60.11
2026-01-21 10:10:10.507 +0100 [pool-6-thread-1] DEBUG yams.SSOManager - SSOManager.getSSOTargetList read 2 targets for 10.10.60.11
2026-01-21 10:10:10.507 +0100 [pool-6-thread-1] DEBUG yams.SSOManager - SSOManager.getSSOTargetList(01:23:44:AB:CD:EF) retval = {175=true, 1342=false}
2026-01-21 10:10:10.507 +0100 [pool-6-thread-1] DEBUG yams.SSOManager - SSOManager.testAdapterPerAgent testing agent associated to model 1342
2026-01-21 10:10:10.507 +0100 [pool-6-thread-1] DEBUG yams.SSOManager - SSOManager.canSendToTarget for agent element 1342 send = false
2026-01-21 10:10:10.507 +0100 [pool-6-thread-1] DEBUG yams.SSOManager - SSOManager.hasMessageFor queue size = 0
2026-01-21 10:10:10.507 +0100 [pool-6-thread-1] DEBUG yams.SSOManager - SSOManager.testAdapterPerAgent device 10.10.2.5(null) not applicable for mac 01:23:44:AB:CD:EF
2026-01-21 10:10:10.507 +0100 [pool-6-thread-1] DEBUG yams.SSOManager - SSOManager.testAdapterPerAgent added UserVlan for adapter 01:23:44:AB:CD:EF
-
Disable debug by executing the following command:
nacdebug -name SSOManager false
- Export PaloAltoSSOTest.txt from the appliance to an external FTP/TFTP/SCP server.
- Open a support ticket and provide the following information:
- Problem description.
- Results of the troubleshooting steps listed above.
- IP address and user ID of the affected client(s).
- Date and time of logon during the test.
- Resulting log file (PaloAltoSSOTest.txt).
Related article:
Technical Note: FortiGate and Palo Alto Single Sign-On stop working after upgrade


