Technical Tip: Imported LDAP group membership changes not updated
Description
This article describes the behavior and how to solve an issue with Database synchronization after moving a user account in Active Directory from one group to another and the user is still listed as a member of the original group.
Scope
FortiNAC.
Solution
The database will not reflect LDAP group membership changes until the next scheduled directory synchronization.
- Verify in the directory the user account was moved properly and is listed in the new group.
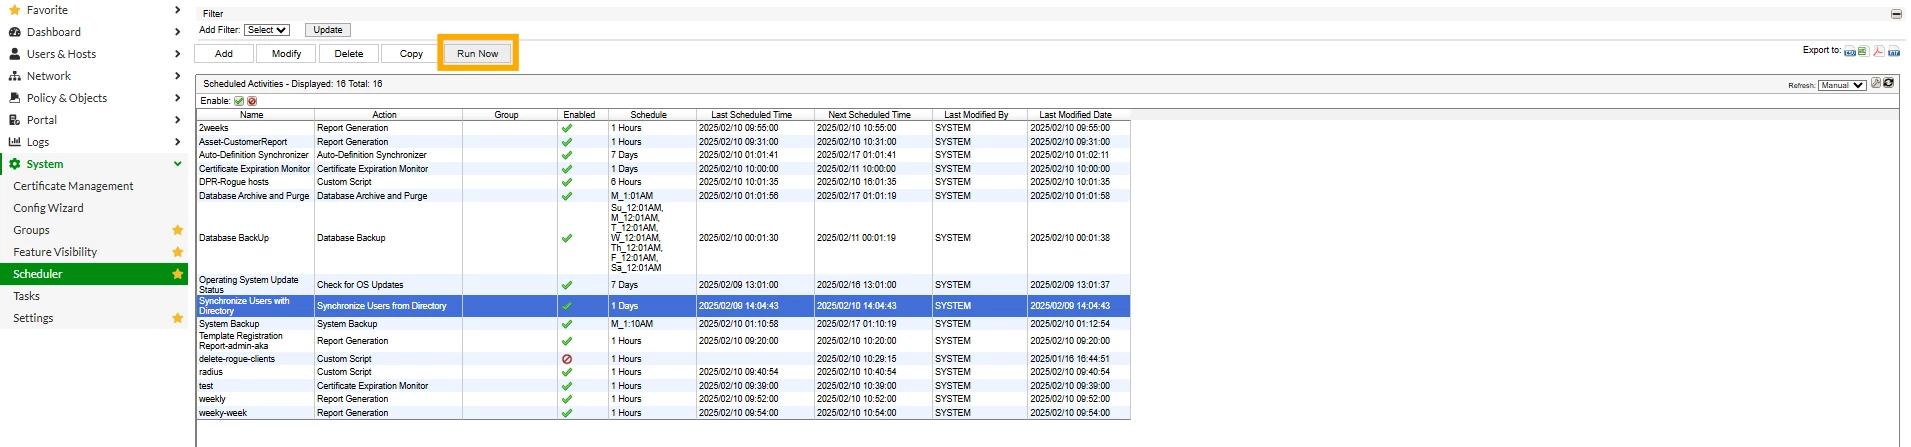
- Manually run the task to synchronize the database with the directory to update the changes immediately.
- In the Administration UI, navigate to Systems -> Scheduler.
- Select Synchronize Users with Directory.
- Select Run Now.