



Technical Tip: Dissolvable agent prompts for server name during VPN registration
Description
This article explains the Dissolvable Agent prompt to enter the server name during VPN registration. This can occur if the agent is unable to locate the appliance due to a domain mismatch.
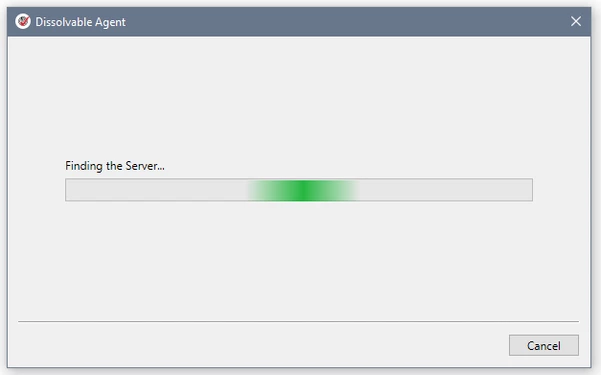
During connection, the agent sends SRV DNS requests (queries) to determine the name of the appliance. SRV queries are answered if they are sourced from the same domain as the appliance VPN interface. If different, the agent will be unable to determine the appliance name, and agent communication will fail. Therefore, if FortiNAC is managing multiple VPN scopes, they must all use the same domain.
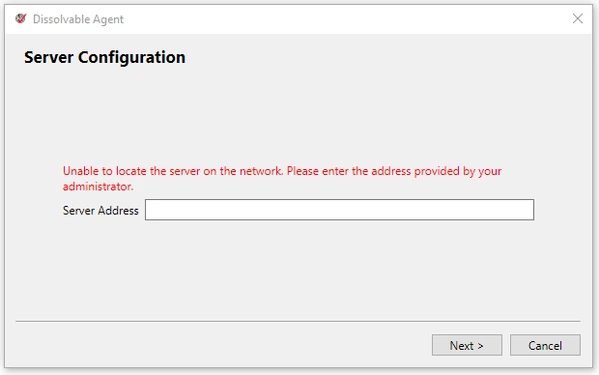
Scope
FortiNAC.
Solution
For integration with Cisco ASA, the 'default-domain value' should match the domain specified in the FortiNAC VPN DHCP scope.
default-domain value <domain in VPN DHCP scope>
For integration with FortiGate VPN, the 'dns-suffix' value should match the domain specified in the FortiNAC VPN DHCP scope.
config vpn ssl web portal
edit "FNAC_SSL_Portal"
set dns-suffix "<domain in VPN DHCP scope>"
Related articles:
Technical Tip: Agent DNS records (SRV) and checks on Microsoft environment
Technical Tip: A simple network example of deploying VPN management with FortiGate
