



Troubleshooting Tip: How to connect FortiGate to FortiManager Cloud and troubleshoot connectivity issues
Description
This article describes how to connect FortiGate to FortiManager Cloud and troubleshoot connectivity issues.
Scope
FortiGate, FortiManager Cloud.
Solution
Before starting, confirm that there is a valid FortiManager Cloud subscription registered to the same FortiCloud Account as the FortiGate that will be connecting to it:
FortiManager Cloud subscription:
The SKU for a FortiManager Cloud subscription follows the pattern of FC<#>-10-MVCLD-227-01-12. For more information, view the following articles:
Additionally, check and confirm that the following account-level requirements/limitations regarding FortiManager Cloud have been met:
A primary FortiCloud account is required for deployment.
Only one FortiManager Cloud instance is supported per FortiCloud account.
Any FortiGates to be managed must be under the same FortiCloud account as the FortiManager Cloud instance.
FortiManager Cloud only supports a single ADOM, so ensure that it is configured to match the firmware running on the managed FortiGates (see also: Updating the ADOM version).
Note that FortiManager Cloud has some feature limitations compared to a standard FortiManager deployment. Check the following section of the FortiManager Cloud Release Notes for more information: Limitations of FortiManager Cloud.
FortiGate license:
Run the following CLI command to check if the FortiGate has a valid contract and that the account matches the same FortiCloud account as FortiManager:
diagnose test update info
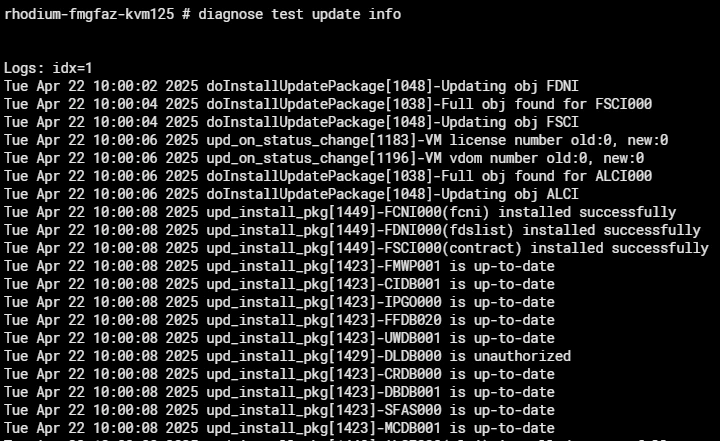
Check the time settings on the FortiGate device:
Ensure that the time settings are set to automatic, using the Network Time Protocol (NTP), and that the time is synchronized with the FortiManager Cloud server.
Connect FortiGate to FortiManager Cloud:
Go to Security Fabric -> Fabric Connectors and edit the Central Management connector, then set the Status toggle to Enabled and select FortiManager Cloud. Select OK to apply the change.
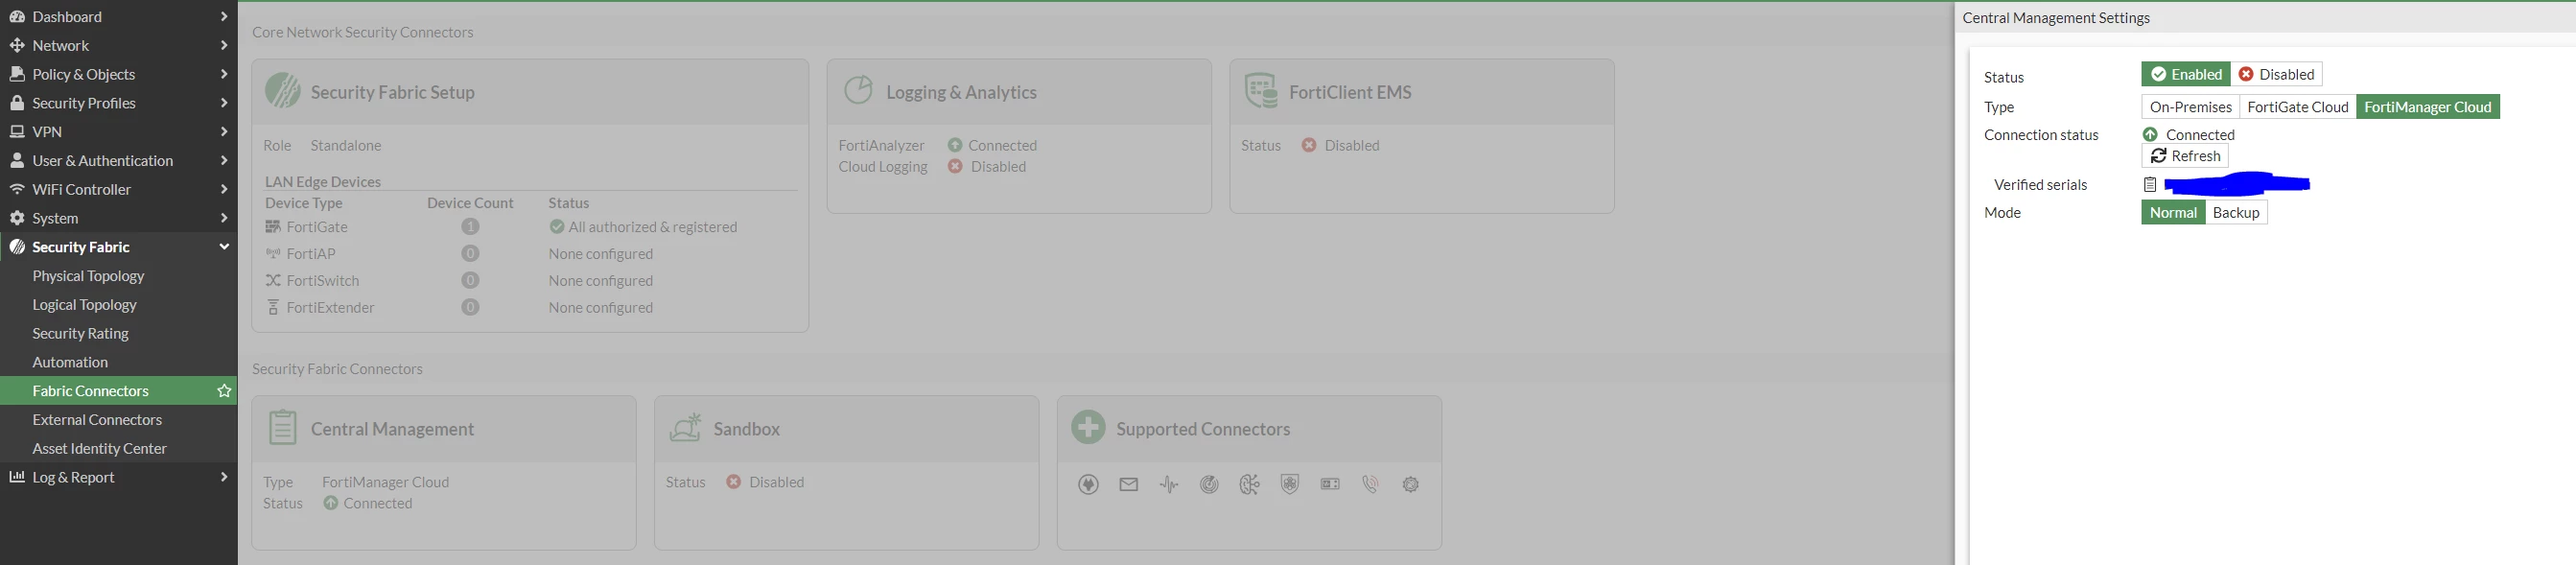
If the FortiManager Cloud option is greyed out on FortiGate, ensure the device has a FortiManager Cloud entitlement. If it does, troubleshoot the device's connection to FortiGuard and refer to the article Technical Tip: FortiManager Cloud option not available (greyed out) in FortiGate central management.
On FortiManager Cloud, navigate to Device Manager and check the Unauthorized Devices list. It should now show the device name and serial number of the FortiGate that was recently configured. Select the entry and then select the Authorize button:
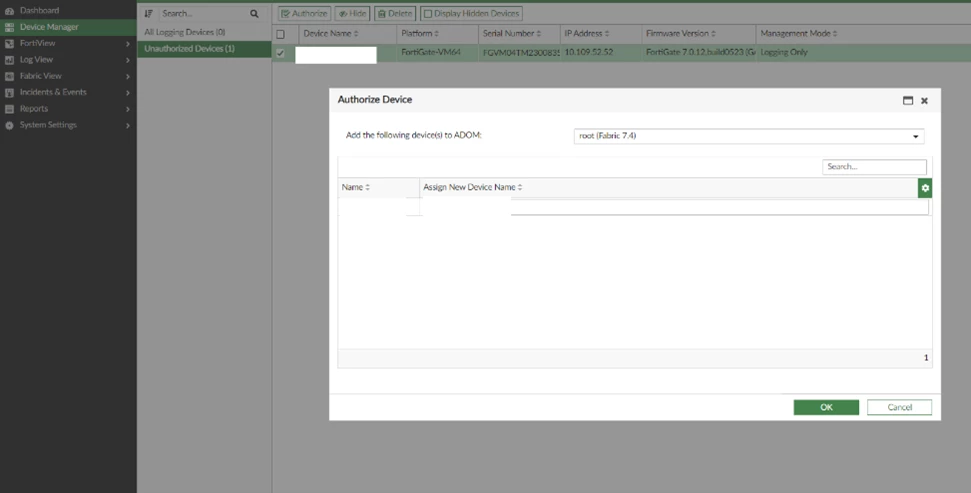
The FortiGate's serial number is used to identify itself to FortiManager. In a working scenario, the connection status should show as connected:
Similarly, FortiManager Cloud should now show this FortiGate in the Managed FortiGates section with a green up arrow indicating that connectivity is established:
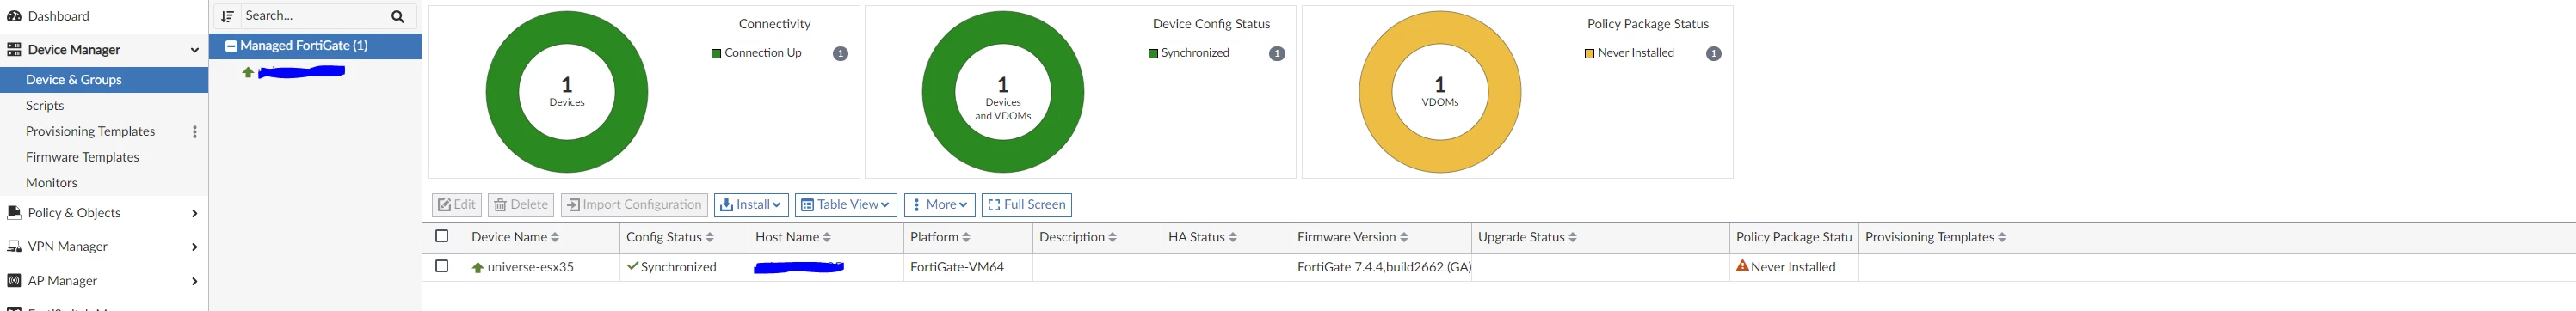
Troubleshooting connectivity:
If the FortiGate's Central Management connector is showing FortiManager Cloud as offline/down, then start by running the following CLI commands on the FortiGate.
For a summary of FortiGate/FortiManager connectivity:
diagnose fdsm central-mgmt-status
To test DNS resolution and TCP/541 connectivity to FortiManager Cloud:
execute telnet fortimanager.forticloud.com 541
To test DNS resolution and general ICMP connectivity to FortiManager Cloud:
execute ping fortimanager.forticloud.com
Example working output (note that the resolved IP address will change depending on FortiGate's geographic location):
FortiGate # diagnose fdsm central-mgmt-status
Connection status: Up
Registration status: Registered
Serial: FMGVCLTMXXXXXXX
FortiGate # execute telnet fortimanager.forticloud.com 541
Trying 160.223.172.25...
Connected to 160.223.172.25.
Connection closed by foreign host.FortiGate # execute ping fortimanager.forticloud.com
PING fortimanager.forticloud.com.geo.fortinet.net (160.223.172.25): 56 data bytes
64 bytes from 160.223.172.25: icmp_seq=0 ttl=60 time=0.6 ms
64 bytes from 160.223.172.25: icmp_seq=1 ttl=60 time=0.4 ms
64 bytes from 160.223.172.25: icmp_seq=2 ttl=60 time=0.3 ms
64 bytes from 160.223.172.25: icmp_seq=3 ttl=60 time=0.3 ms
64 bytes from 160.223.172.25: icmp_seq=4 ttl=60 time=0.3 ms
--- fortimanager.forticloud.com.geo.fortinet.net ping statistics ---
5 packets transmitted, 5 packets received, 0% packet loss
round-trip min/avg/max = 0.3/0.3/0.6 ms
If the connection status of the FortiGate/FortiManager (FGFM) management tunnel is down and there is no response on the telnet or ping tests, then there may be upstream Internet issues that need to be resolved (reach out to the ISP or check any upstream routers/switches, and also ensure that the FortiGate can resolve FQDNs via DNS successfully).
Alternatively, if the management tunnel is down but telnet and pings to fortimanager.forticloud.com are succeeding, then proceed with the next troubleshooting step, which is to run packet captures on the FortiGate and FortiManager Cloud.
Running packet captures:
Run the following command on the FortiGate CLI to capture TCP/541 traffic going to/from fortimanager.forticloud.com:
diagnose sniffer packet any 'host <FortiManager Cloud IP> and port 541' 6 0 l
At the same time, run the following command on the FortiManager CLI.
Related article:
Connecting to the FortiManager CLI using the GUI.
diagnose sniffer packet any 'port 541' 4 0 l
Run both packet captures simultaneously and confirm that the outgoing connection in the FortiGate packet capture corresponds with a similar incoming connection on the FortiManager Cloud capture.
Important: The FortiGate will query DNS for fortimanager.forticloud.com to reach FortiManager Cloud. This FQDN is resolved via Geo DNS, and so the resolved IP address will belong to the Fortinet datacenter nearest to that FortiGate. For example, the FortiGate may resolve the FQDN to a US Central datacenter IP, even though the actual FortiManager Cloud instance is in US West.
This is not typically an issue, as the load-balancers located in these Fortinet datacenters will redirect the FortiGate's connection towards the right datacenter hosting the FortiManager Cloud instance. However, in some cases, this redirection may not function correctly, which can lead to a situation where packet captures, telnet connections, and pings on the FortiGate all indicate working connectivity, but FortiManager Cloud does not show any incoming traffic being received from that FortiGate.
If this occurs, reach out to FortiManager technical support and ask them to have the redirect issue investigated. FortiManager Cloud permissions may need to be granted to the FortiManager team to investigate the issue for the affected FortiManager Cloud instance. See also: Technical Tip: Allow Full Access for Fortinet Backend Support in FortiManager-Cloud.
In the meantime, the following workaround can be added to the FortiGate to override the DNS resolution and have it connect to the region that is hosting the FortiManager Cloud instance:
Obtain the public IP associated with the FortiManager Cloud instance. The following article explains how to check this from the FortiManager Cloud instance directly: Identifying the public IP address.
On the FortiGate, add a new DNS Database entry for fortimanager.forticloud.com and set it to the public IP of the FortiManager Cloud instance retrieved in the previous step. The FortiGate will now resolve this FQDN to the specified public IP, which removes the need for connection redirection by the Fortinet load-balancers.
config system dns-database
    edit "fortimanager.forticloud.com"
        set domain "fortimanager.forticloud.com"
        set authoritative disable
            config dns-entry
                edit 1
                    set hostname "fortimanager.forticloud.com"
                    set ip <public_ip>
                next
            end
    next
end
Further debugging:
If network connectivity between FortiGate and FortiManager Cloud is working, but the management tunnel is still not establishing, then run the following on the FortiGate to gather further debug information:
diagnose debug reset
diagnose debug application fgfmd 255
diagnose debug cli 8
diagnose debug console time enable
diagnose debug enable
To disable the debug commands after troubleshooting is completed:
diagnose debug disable
diagnose debug reset
At the same time, run the following debug commands on FortiManager Cloud:
diagnose debug reset
diagnose debug application fgfmsd 255 <deviceName>
diagnose debug time enable
diagnose debug enable
Once again, disable debug processes:
diagnose debug disable
diagnose debug reset
Additional notes:
The source IP used by the FortiGate to make a connection to FortiManager Cloud can be set using the fmg-source:
config system central-management
    set fmg-source-ip <FGT-IP>
end
FortiManager Cloud may attempt to use the default FortiGate 'admin' account during the standard device authorization workflow. If the default account is unavailable, has been renamed or deleted, or its password has changed, add the FortiGate through the Add Device wizard and provide credentials for another valid local FortiGate administrator account.
After authorization, FGFM communication uses certificate and serial-number authentication and does not depend on the FortiGate account being named 'admin'.
The following CLI command can be used to manually trigger the FortiGate to send an authorization request to FortiManager Cloud:
execute central-mgmt register-device <FMG Serial> <admin>
From FortiManager v7.6.3, a new control feature has been introduced. It will disable new VMs from registering to FortiManager. By default, registration of new FortiGate-VMs is disabled.
Refer to: Security enhancement to control new VM device registration to FortiManager.
To allow VMs to be managed by FortiManager, run the following configuration:
config system global
    set fgfm-allow-vm enable
end
Related articles:
Troubleshooting Tip: How to troubleshoot connectivity issues between FortiGate and FortiManager
Technical Tip: The FortiGate license is needed for firmware upgrade
Troubleshooting Tip: FortiGuard Update Fail: Server certificate failed verification
Troubleshooting Tip: How to troubleshoot connectivity to FortiManager Cloud
Technical Tip: FortiManager Cloud shows unreachable/not connected

