



Technical Tip: pxGrid integration fails after certificate renewal with HTTP 401 unauthorized
Description
This article describes how to identify and troubleshoot pxGrid authentication failures between FortiManager and Cisco ISE, where the TLS handshake succeeds but authentication is rejected with HTTP 401 Unauthorized.
Scope
Product: FortiManager.
Feature: pxGrid Connector.
Solution
After replacing the pxGrid certificate on Cisco ISE, FortiManager can establish network connectivity and complete SSL/TLS negotiation. However, authentication fails during the pxGrid authorization phase.
The pxGrid connector repeatedly disconnects, and no session/user data is retrieved.
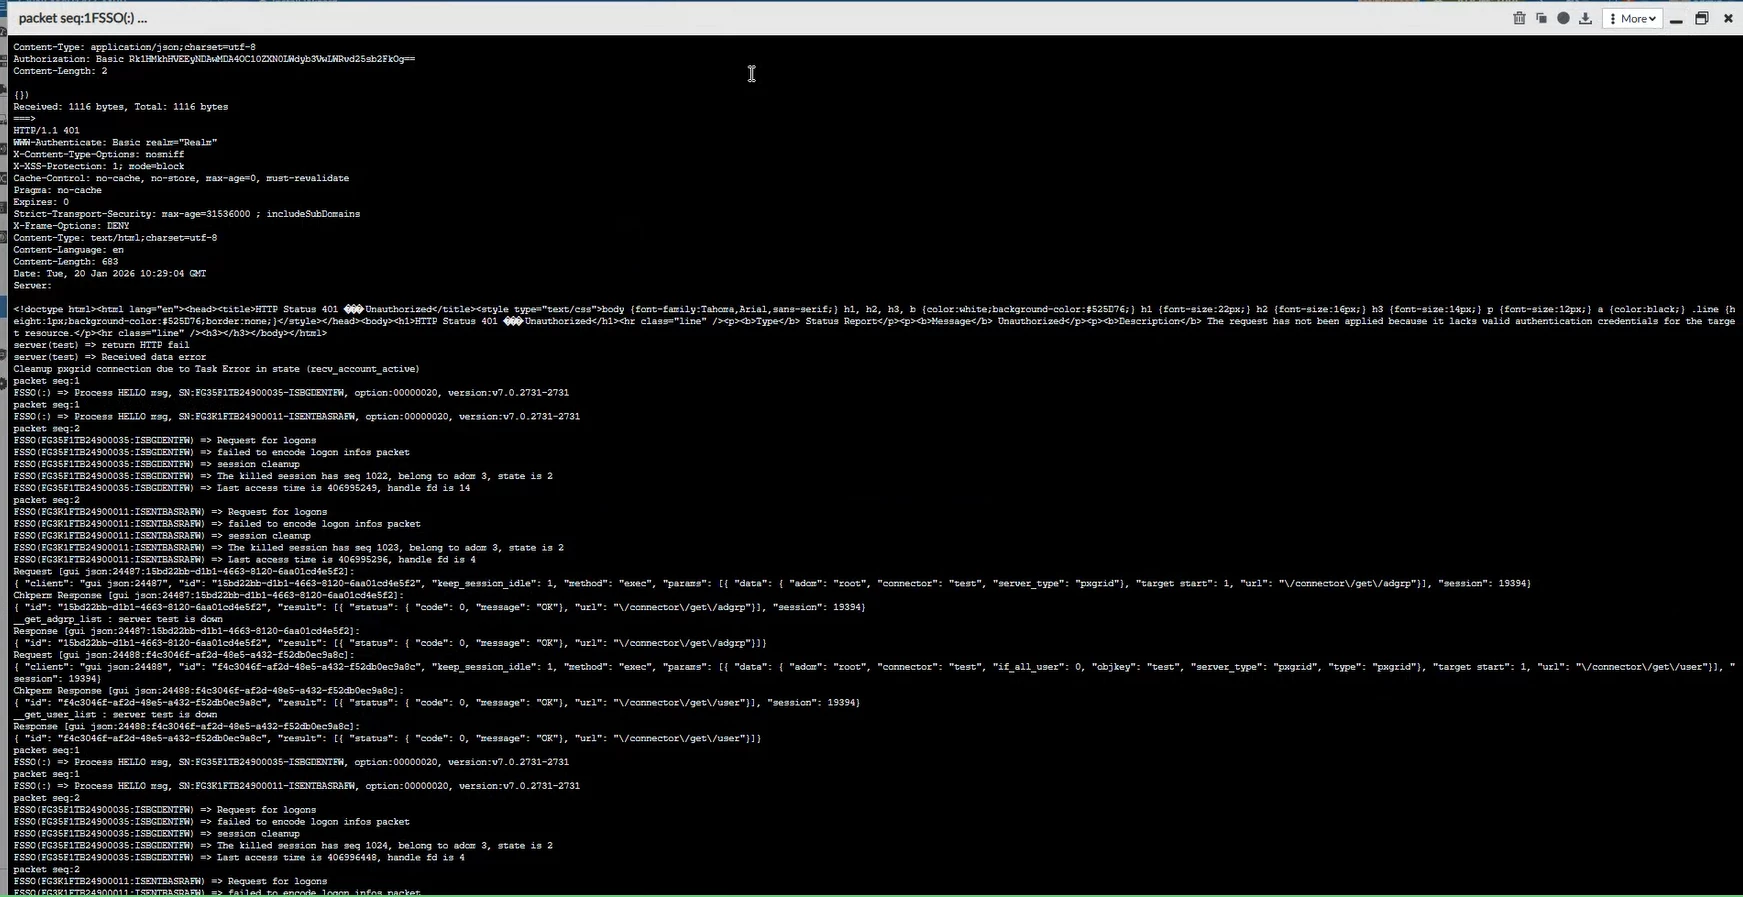
When pxGrid debug is enabled on FortiManager, the following error is observed:
- HTTP/1.1 401 Unauthorized.
- Failed to decode the logon info packet.
- Cleanup pxgrid connection due to task error.
This indicates that Cisco ISE is actively rejecting the pxGrid client authentication.
How to troubleshoot:
Enable debug and timestamps:
diagnose debug reset
diagnose debug console timestamp enable
diagnose debug enable
Enable pxGrid/connector debug (mandatory):
diagnose debug application connector 255
Trigger the issue by reconnecting the pxGrid connector from the GUI (Apply & Refresh button).
Stop debug after capture:
diagnose debug disable
diagnose debug reset
Below is a captured example of the error output:
Highlighted error message:
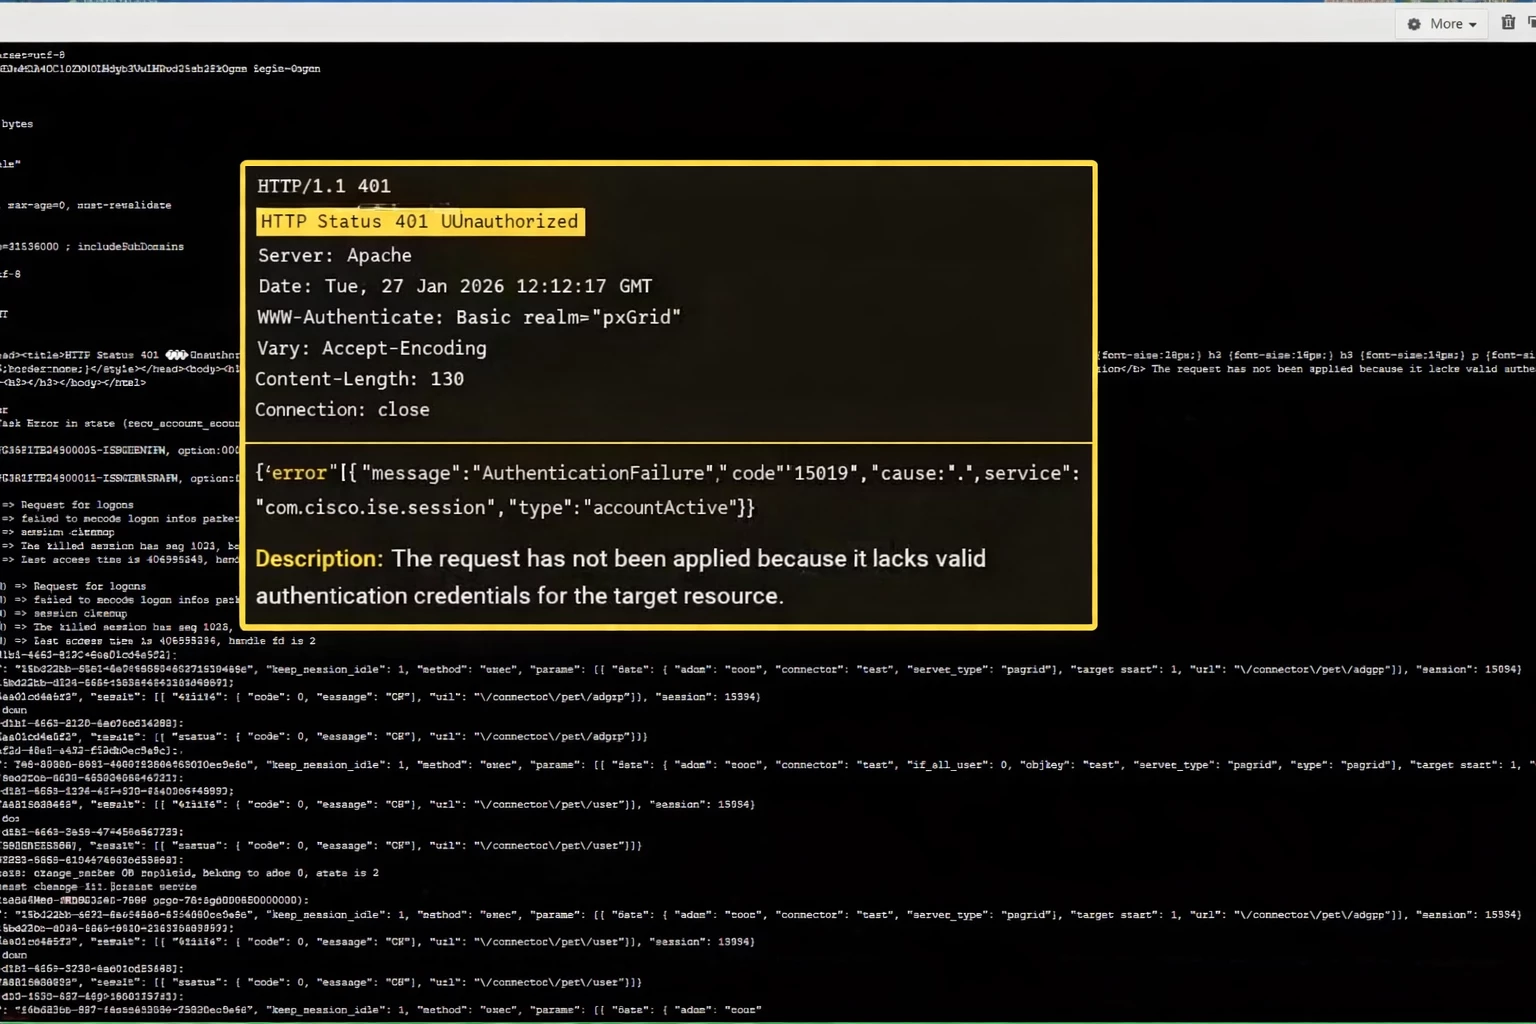
Root cause and explanations:
The issue is not related to FortiManager software, the pxGrid connector, or CA trust configuration.
Although the new pxGrid certificate was issued by the same Root and Intermediate CA and met all cryptographic and technical requirements, Cisco ISE pxGrid does not rely solely on CA trust to authorize clients.
Cisco ISE treats each certificate as a unique pxGrid client identity, based on the certificate’s fingerprint and identity attributes, not just its issuing CA.
When the certificate was replaced on FortiManager:
-
Cisco ISE retained the existing pxGrid client bindings associated with the old certificate.
-
The new certificate was therefore recognized as a different client.
-
The new client identity was not approved or authorized in Cisco ISE.
-
As a result, pxGrid authentication attempts were explicitly rejected by Cisco ISE with HTTP 401 Unauthorized.
This behavior occurs even when the Root CA and Intermediate CA are identical, because pxGrid authorization is tied to the individual certificate identity, not the CA chain.
Resolution on Cisco ISE:
- Navigate to Administration → pxGrid Services → Clients.
- Delete existing FortiManager pxGrid client bindings.
- Restart pxGrid services (recommended).
- Reconnect FortiManager using the new certificate.
- Approve the newly detected pxGrid client.
After re-approval, the pxGrid connection is established successfully without changes on FortiManager.
Related document:


