



Technical Tip: Policy Package gets imported incompletely into FortiManager
Description
This article describes a scenario in which the FortiGate's policies are imported incompletely into a FortiManager Policy Package, due to an Interface Binding Conflict.
After this incomplete Import Policy, the administrator may inadvertently delete the skipped rules and linked objects from the FortiGate.
Scope
FortiManager.
Solution
To prevent this scenario, it is recommended to carefully review the messages in the Import Policy wizard.
The pre-import step would normally detect and indicate Interface Binding Conflicts:
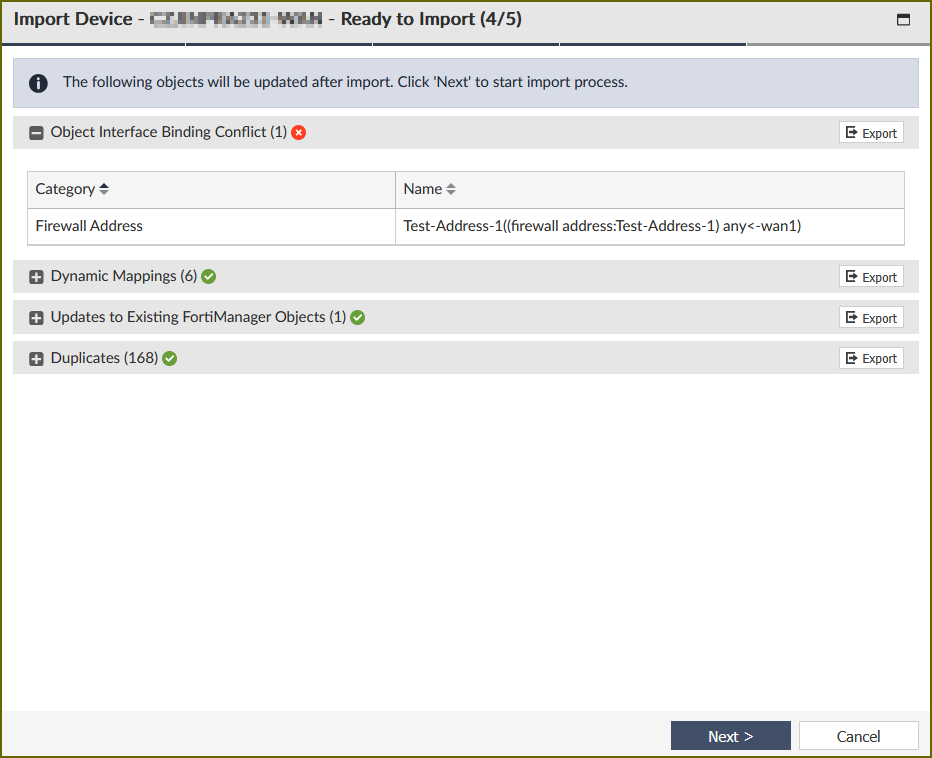
If this warning is missed, at the end of the import process, FortiManager provides an import summary and displays more warnings. The Import Report can be also downloaded for further review:
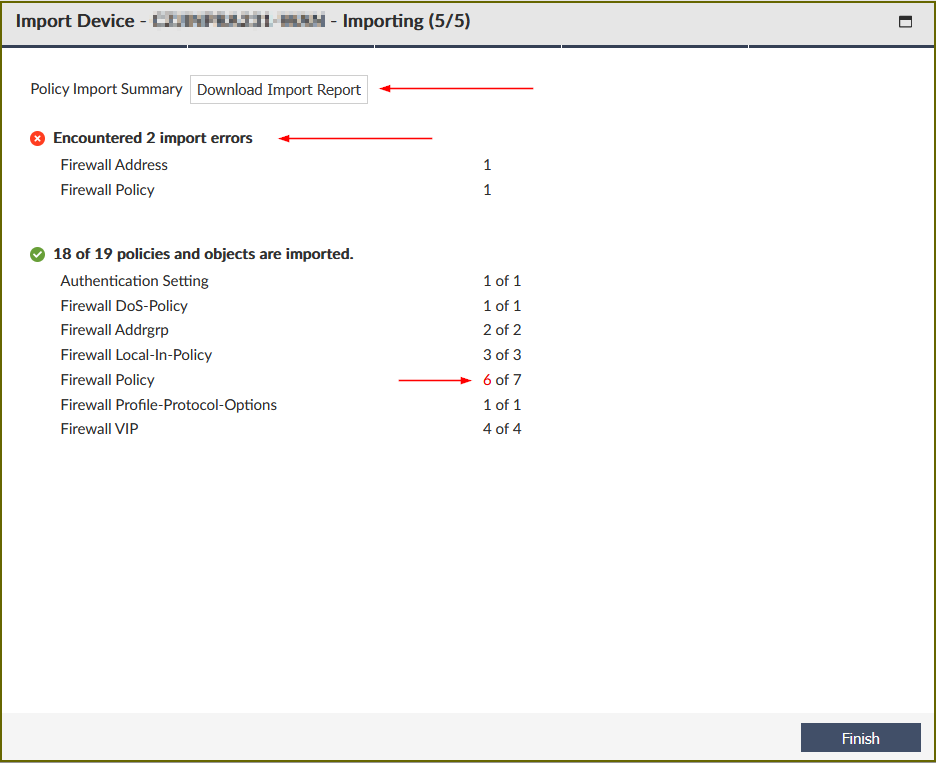
As the report is often too long to review line by line, search for the keyword 'FAIL'.
For example:
...
"firewall address",FAIL,"(name=Test-Address-1, oid=4578, reason=interface((firewall address:Test-Address-1) any<-wan1) binding fail)"
...
"firewall policy",FAIL,"(name=8, oid=4579, reason=interface(interface binding contradiction. detail: (firewall address:Test-Address-1) any<-wan1) binding fail)"
...
The entries above indicate that an address object used by the specific policy already exists in FortiManager's database, but has a different interface association.
In this example, the problem is in a firewall address object 'name=Test-Address-1', used in policy ID 8 (name=8).
In the FortiManager ADOM database, the address is bound to the 'any' interface, while on the imported FortiGate, the interface is 'wan1' (any<-wan1).
After identifying the conflicting object(s), the configuration must be changed to resolve the conflict. There are three possible options from which to choose:
Change the interface association to match on both sides.
Rename the object.
Manage the conflicting FortiGate in another ADOM.
Related article:
Troubleshooting Tip: Import policy package failed due to '(invalid in Virtual_wire_pair)) binding fail'

