| A domain name external feed is a dynamic list that contains domains and is periodically updated from an external server. The list is stored in a text file format on an external server. Domain name threat feed connector can be created on the FortiManager, and that will be pushed to the FortiGate when the Firewall policy with the DNS filter is used. - Go to Fabric View -> External Connectors, and select Create New. The Create New Fabric Connector wizard is displayed.
- Under Threat Feeds, select Domain Name Threat Feed and select Next.
- Domain Name:
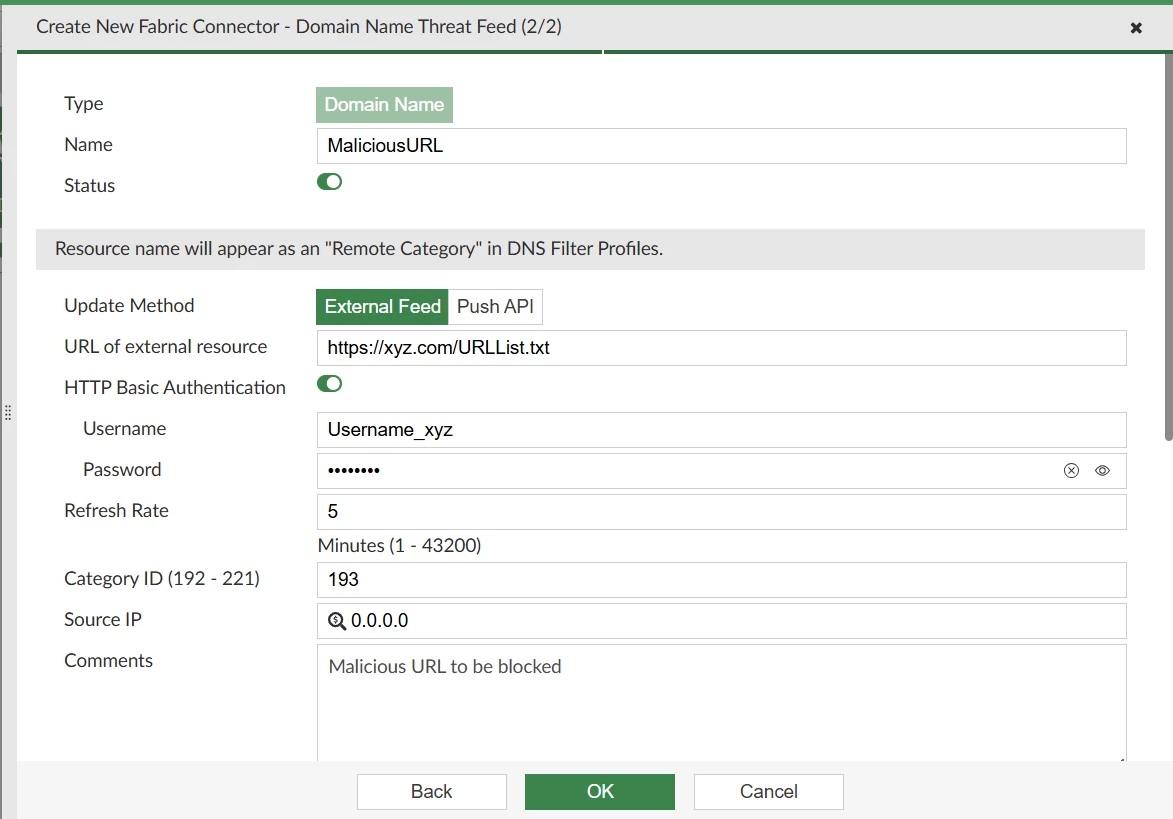
- Create a Domain Name Threat Feed external connector 'MaliciousURL' with the list of URLs to be blocked in the DNS filter.
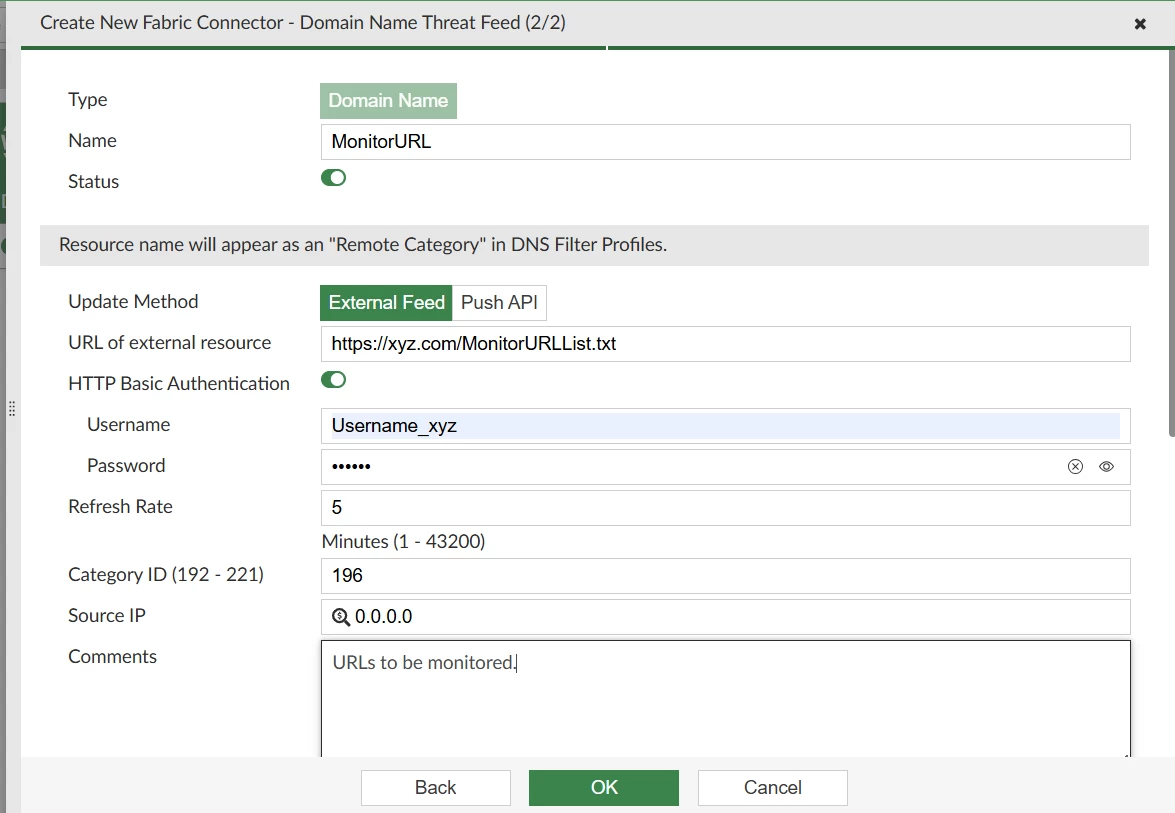
 - Create a Domain Name Threat Feed external connector 'MonitorURL' with the list of URLs to be monitored in the DNS filter.
-
Create a DNS filter 'DNSThreatFilter1' and set the 'MaliciousURL' connectors to be blocked and the 'MonitorURL' connector to be monitored under the remote categories. Policy & Objects -> Security Profiles -> DNS Filter -> Create new. 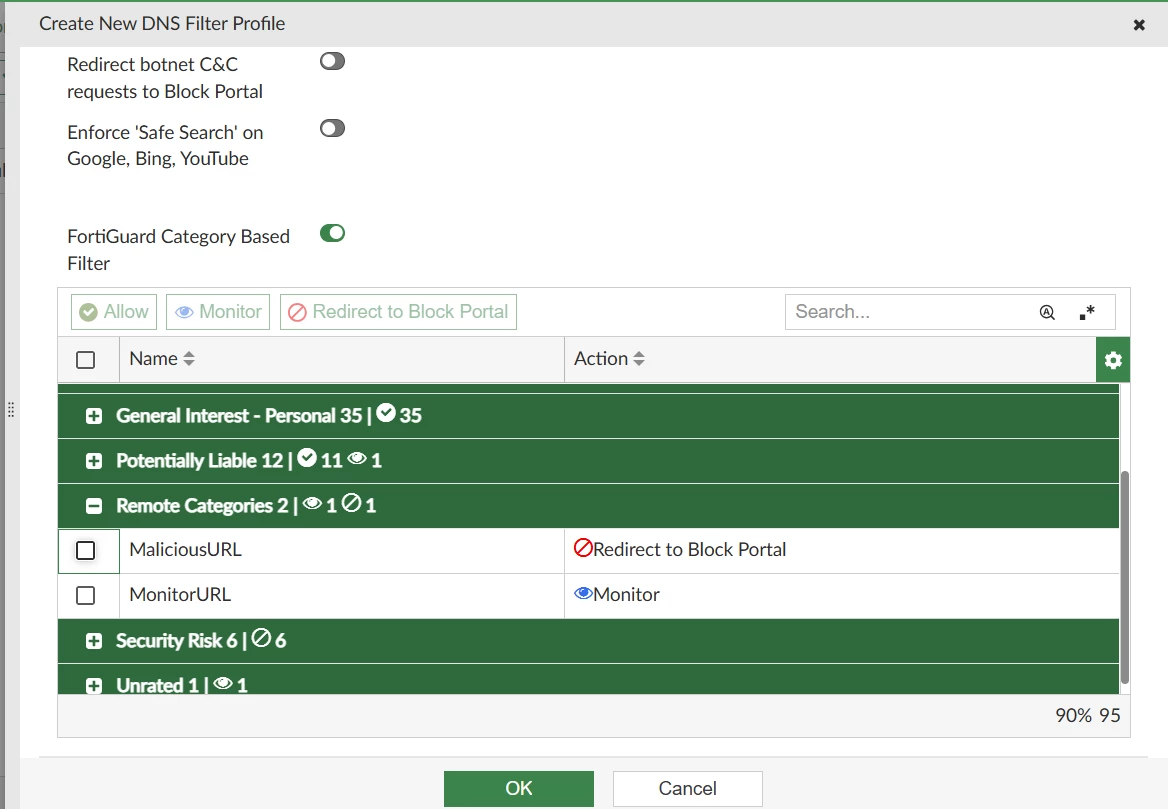
-
Apply the DNS filter under a firewall policy under the Security Profile section. Policy & Objects -> Firewall Policy -> Create/Select the policy -> Security Profiles -> DNS Filter -> Select DNSThreatFilter1. 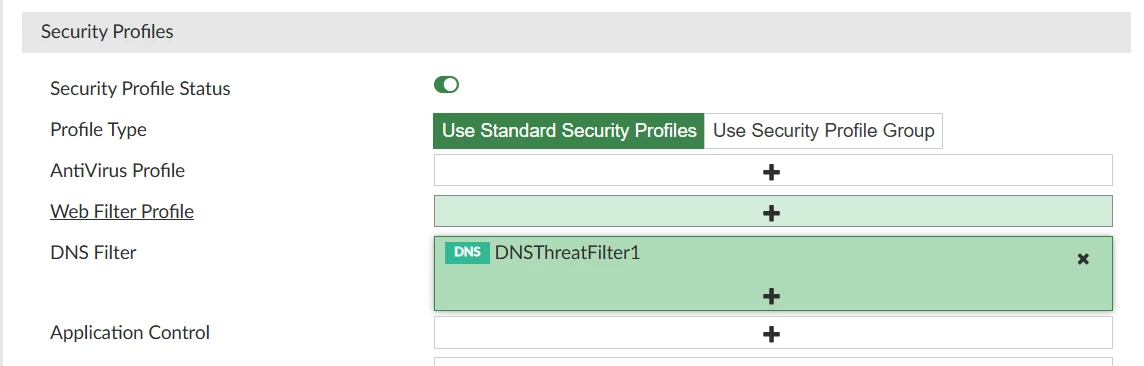
-
Install the policy package on the FortiGate. Install preview: config system external-resource edit "MaliciousURL" set type domain set category 193 set username "Username_xyz" set password ********** set comments "Malicious URL to be blocked" set resource "https://xyz.com/URLList.txt" set uuid e8aa242c-d563-51f0-2a6c-2180af2798ec next edit "MonitorURL" set type domain set category 196 set username "Username_xyz" set password ******** set comments "URLs to be monitored." set resource "https://xyz.com/MonitorURLList.txt" set uuid e8aa4bb4-d563-51f0-e123-3ff8c67e582d next end config dnsfilter profile edit "DNSThreatFilter1" config ftgd-dns config filters edit 1 set category 2 next <trimmed for breivity> edit 17 set category 193 <<< MaliciousURL category set action block <<< Action set to block next edit 18 set category 196 <<< MonitorURL category set to Monitor next end end next end config firewall policy edit 1 set name "Test" set uuid 24eef30c-d557-51f0-07e4-98ee758c3e1d set action accept set srcintf "port5" set dstintf "port6" set srcaddr "all" set dstaddr "all" set schedule "always" set service "ALL" set utm-status enable set logtraffic all set dnsfilter-profile "DNSThreatFilter1" <<<DNS filter applied next end
Note: If the action is set to allow under the remote categories in the DNS filter for an external DNS connector, FortiManager will not push that external DNS connector to the FortiGate. FortiManager will push the external Domain name Threat Feed connectors to FortiGate only when the action is set to monitor or block, and the DNS connector is used in the firewall policy via DNS filter. Selecting the Allow action for the FortiGuard Category-Based Filter does not actually allow the category. It merely implies that no filter has been applied. It is recommended to avoid using the Allow action for remote categories, as it will not override the original action specified in the FortiGuard Category-Based Filter. The Monitor and Block actions for remote categories can override the original action specified in the FortiGuard Category-Based Filter. | 






