| IPsec Aggregate allows grouping multiple IPsec VPN tunnels into a single logical interface for load balancing and redundancy. There are three methods to set up IPsec Aggregate using FortiManager: - Using IPSec Template.
- Creating tunnels on the Device Database.
- Using CLI Template.
Note: The following steps show the configuration required for setting up an IPsec aggregate. Other IPsec configuration details for phase1/phase2 are not covered in this article. Option 1: Use IPsec Template. - Create a new IPsec template: Device Manager -> Provisioning Templates -> IPsec Tunnel -> Create New.
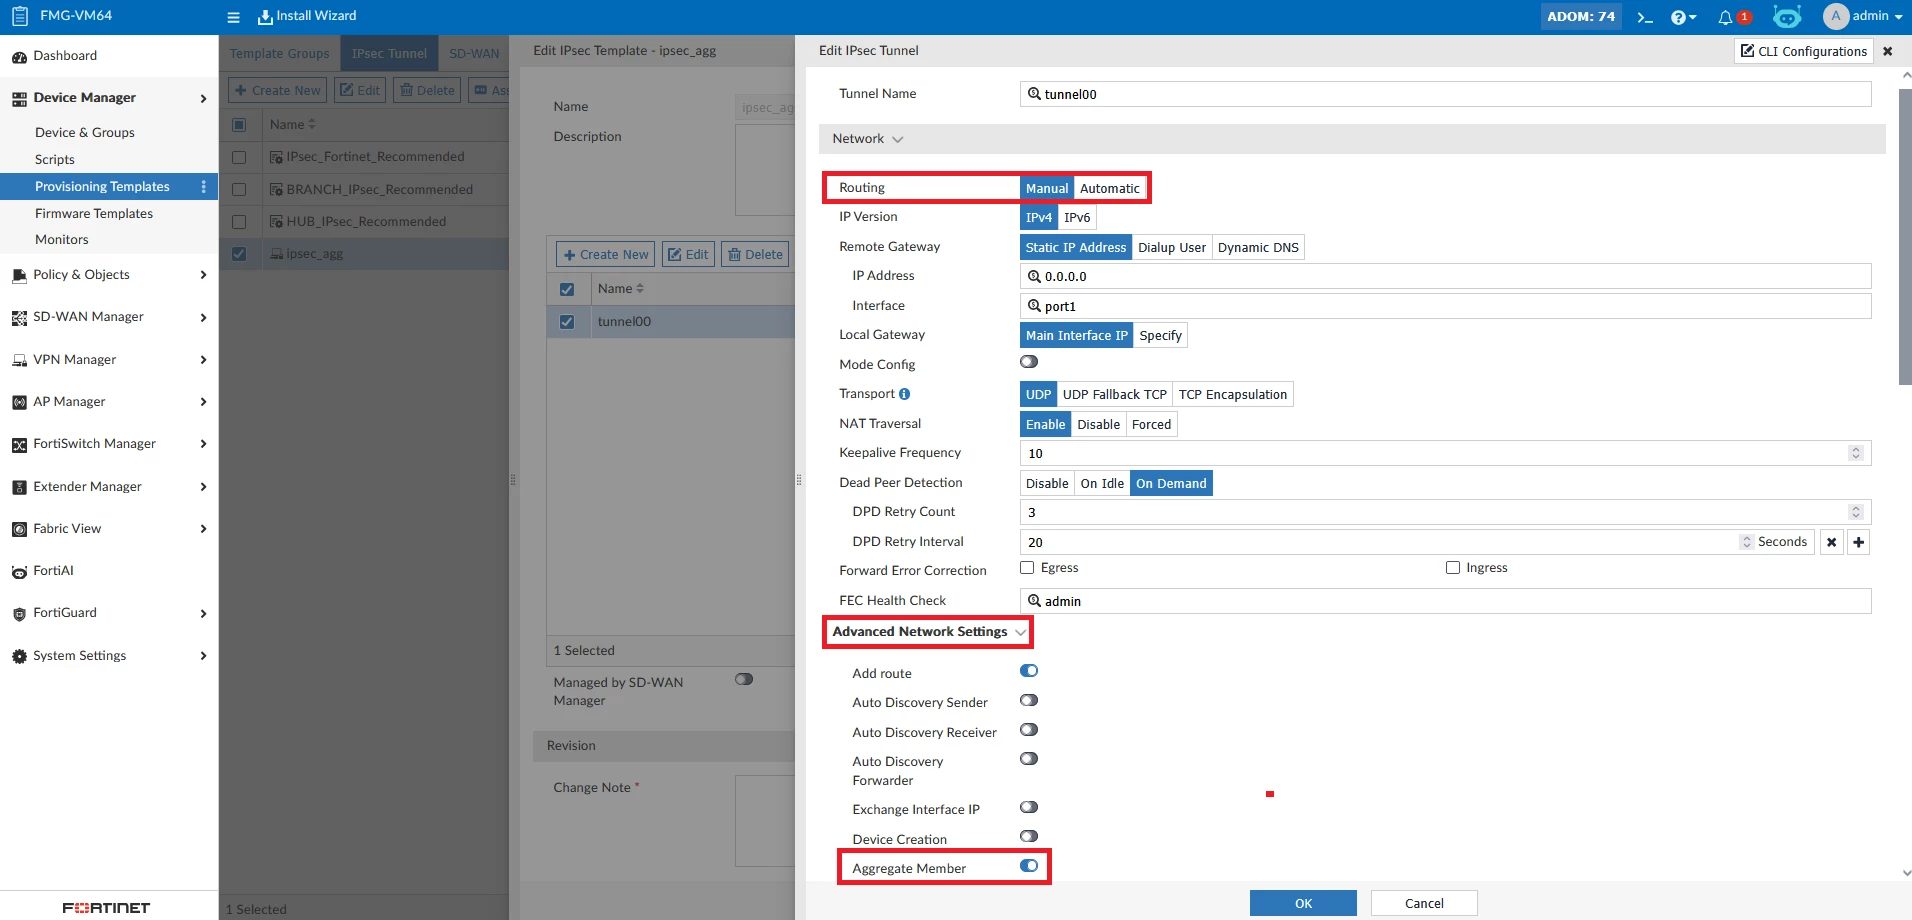
- Set 'Routing' to 'Manual'.
- Under 'Advanced Network Settings': enable 'aggregate-member' option (v7.4, this option is under 'Advanced Options').
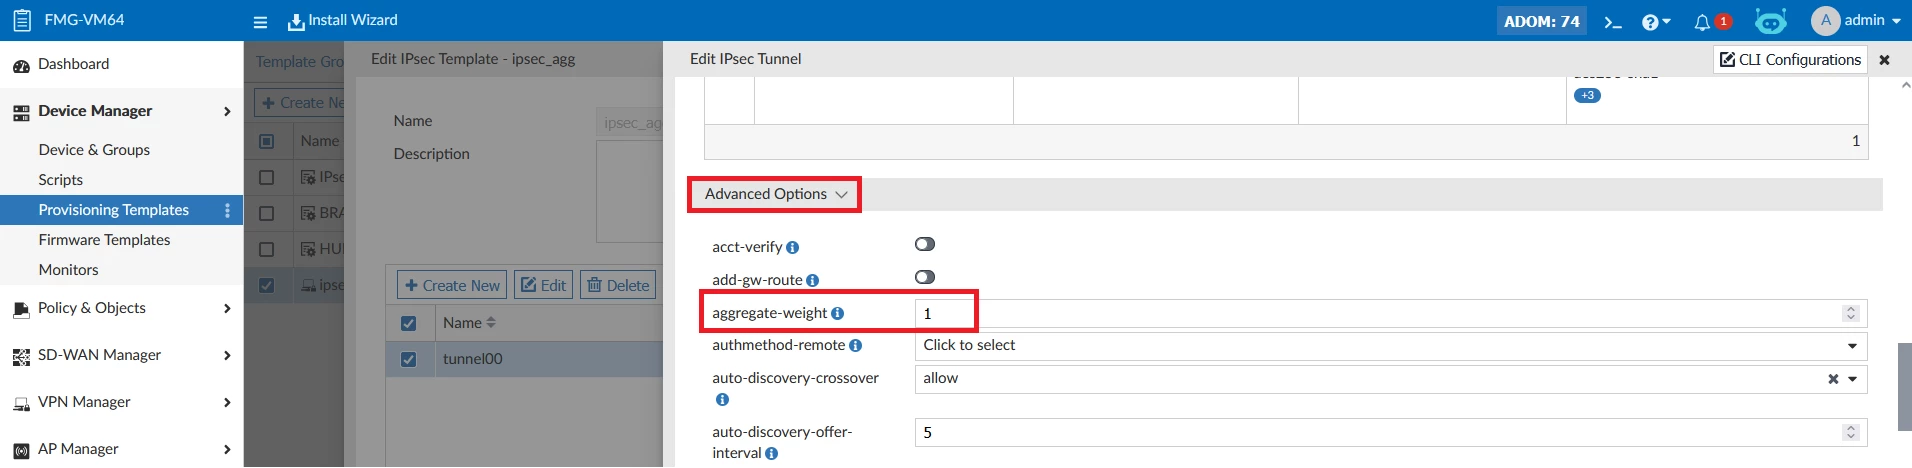
- Under 'Advanced Options', set the aggregate-weight (default is 1).
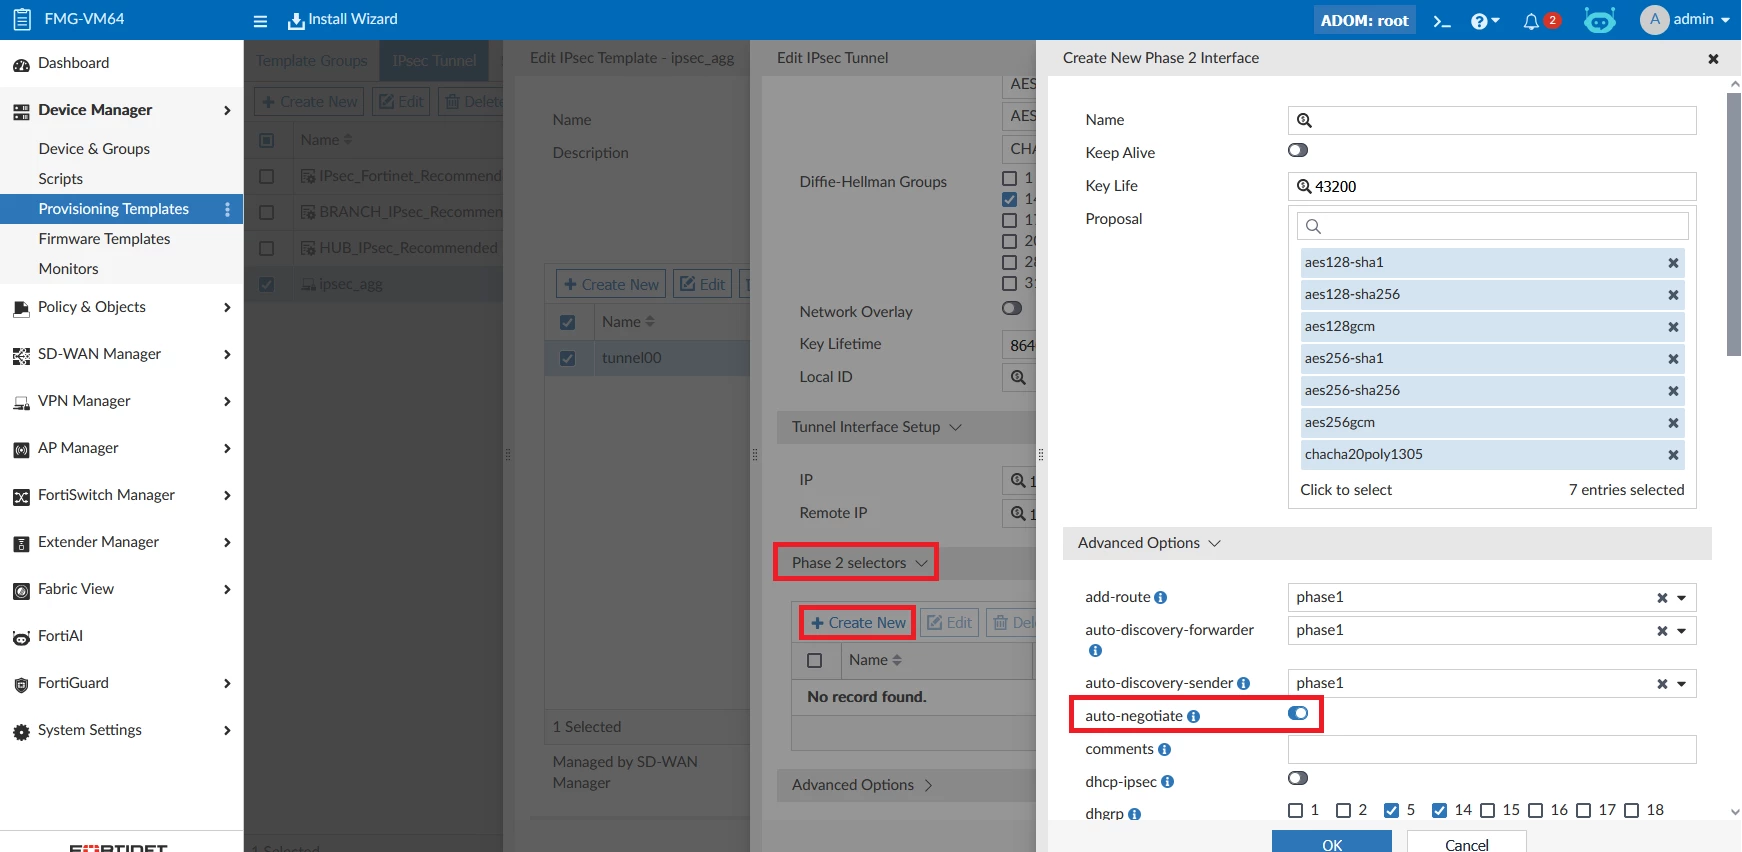
- Create the phase2-interface and under 'Advanced Options' enable 'auto-negotiate'.
- Assign the IPsec Template to a device.
- Push the tunnels to the device(s) using the Install Wizard.
- In Device Manager -> Device & Groups -> Managed FortiGate(s) -> Select the device -> CLI Configurations -> Search for 'ipsec-aggregate' -> Under 'system' select 'ipsec-aggregate' -> Create New and add the desired member tunnel(s). Select OK to save.
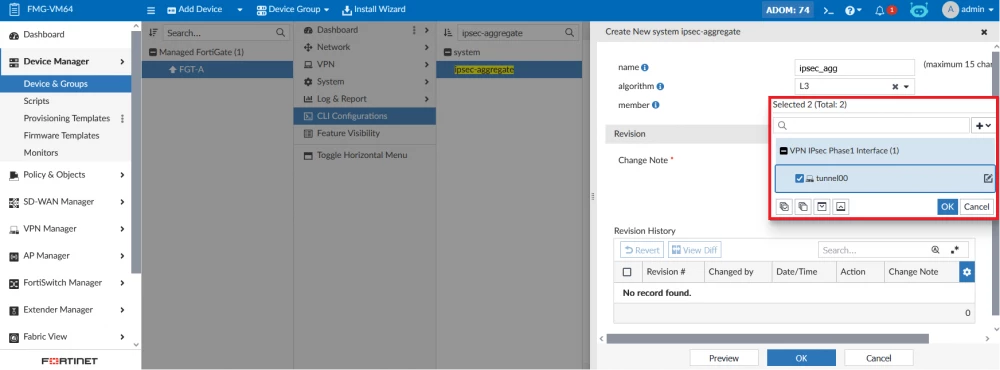
- Push the ipsec-aggregate config to the device(s) using the Install Wizard.
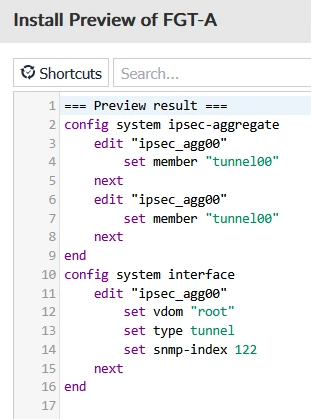
- Add required static routes and policies.
Option 2: Create Tunnels on Device Database. - In Device Manager -> Device & Groups -> Managed FortiGate(s) -> Select the device -> VPN -> IPsec Phase1.
- Create New Phase1 Interface Mode tunnel and enable 'Aggregate Member' (in v7.4 under 'Advanced..(XAUTH,NAT-traversal,DPD)'.
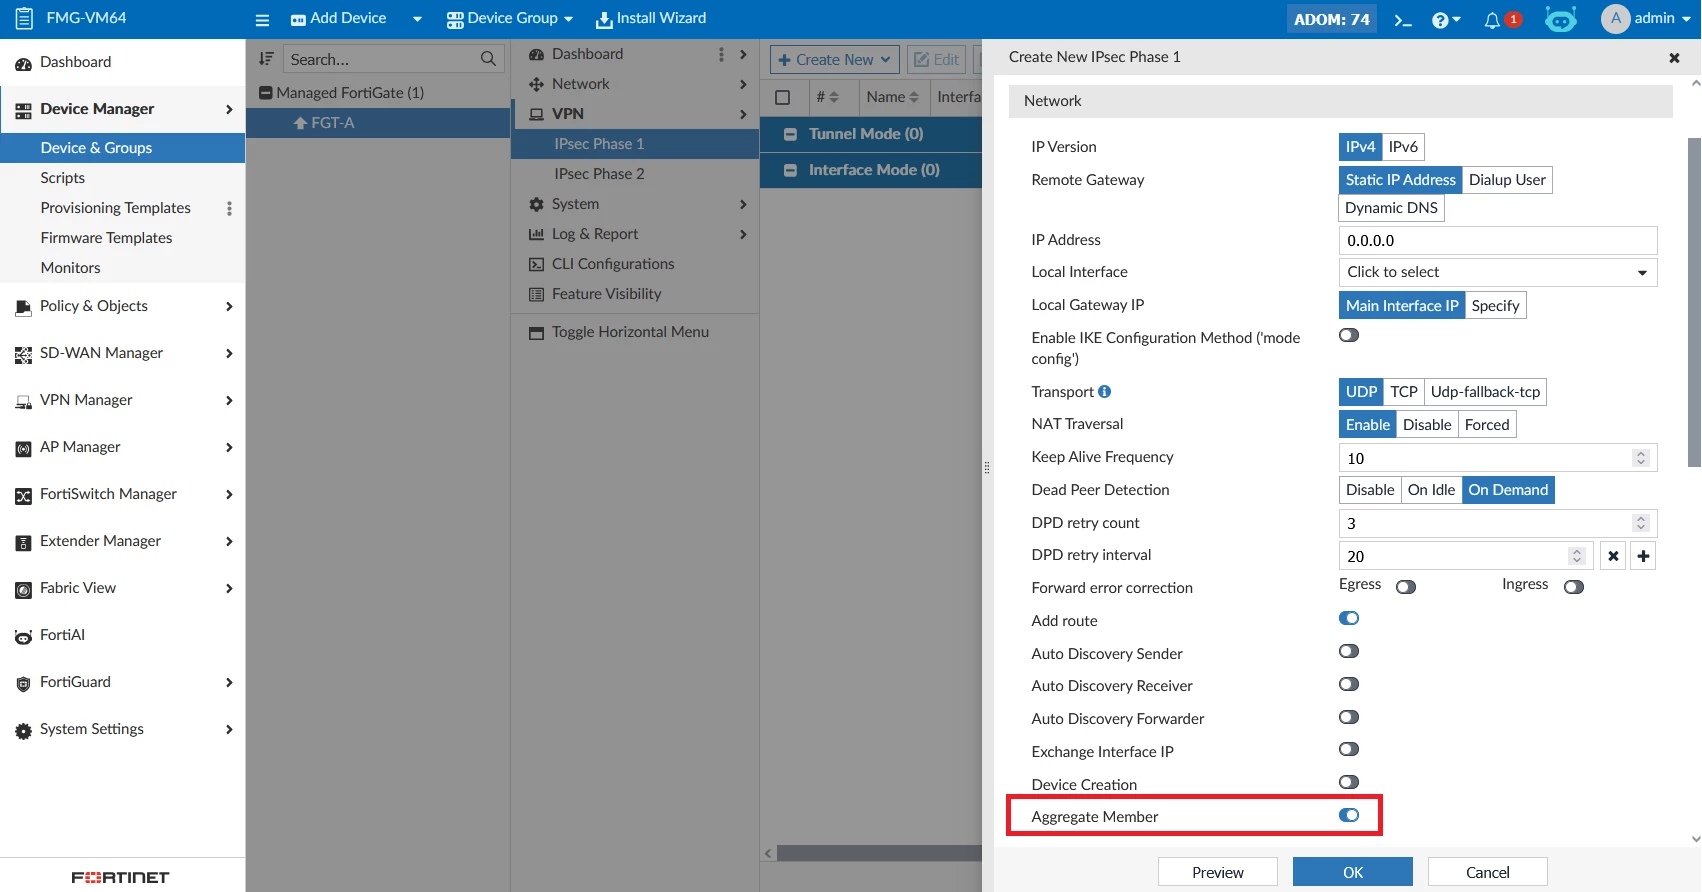
- Set aggregate-weight under Advanced Options:
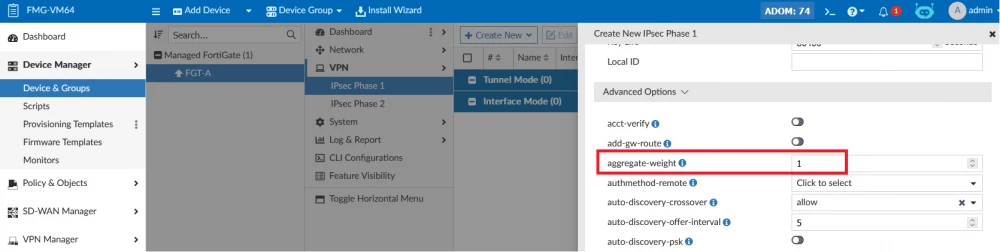
- In Device Manager -> Device & Groups -> Managed FortiGate(s) -> Select the device -> VPN -> IPsec Phase2.
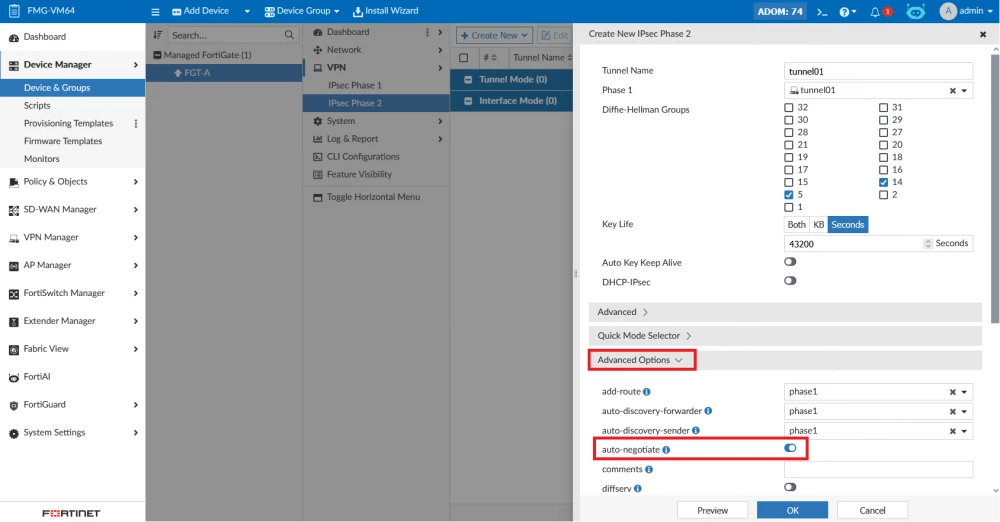
- Create a new Phase2 Interface Mode tunnel and enable 'auto-negotiate' under 'Advanced Options'.
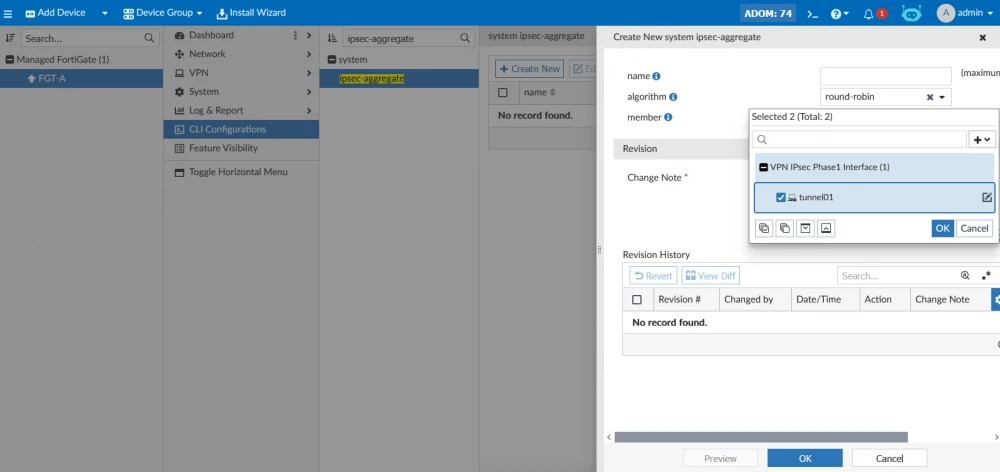
- In Device Manager -> Device & Groups -> Managed FortiGate(s) -> Select the device -> CLI Configurations -> Search for 'ipsec-aggregate' -> Under 'system' select 'ipsec-aggregate' -> Create New and add the desired member tunnel(s). Select OK to save.
- Push the config to the device(s) using the Install Wizard.
- Add required static routes and policies.
Note: Script can also be used to add the config to either the Device Database or directly to the FortiGate. Refer to the document: Scripts. Option 3: Using CLI Template. - Under Device Manager -> Provisioning Templates -> CLI -> Create New -> CLI Template. Refer to the document: Adding CLI templates.
- Add script of creating phase1-interface, phase2-interface, and ipsec-aggregate.
config vpn ipsec phase1-interface edit "<TUNNEL_1>" set interface "<INTERFACE>" set proposal <Algo - for example: aes256-sha256> set remote-gw <REMOTE_GW> set psksecret <PSK> set aggregate-member enable next edit "<TUNNEL_2>" set interface "<INTERFACE>" set proposal <Algo - for example: aes256-sha256> set remote-gw <REMOTE_GW> set psksecret <PSK> set aggregate-member enable next end config vpn ipsec phase2-interface edit "<TUNNEL_1>" set phase1name "<TUNNEL_1>" set proposal <Algo - for example: aes256-sha256> set auto-negotiate enable next edit "<TUNNEL_2>" set phase1name "<TUNNEL_2>" set proposal <Algo - for example: aes256-sha256> set auto-negotiate enable next end config system ipsec-aggregate edit "<IPSEC_AGG_NAME>" set member "<TUNNEL_1>" "<TUNNEL_2>" next end 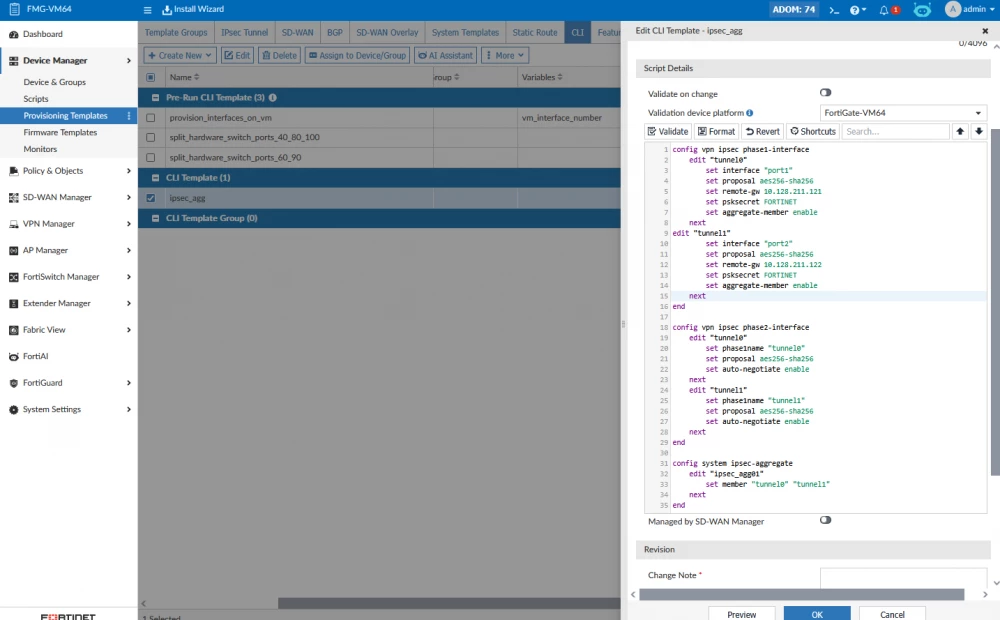
Related documents: |