Admin profile can be used as a best practice for security to apply the least privilege.
There are some options required to show the page in the FortiManager GUI directory tree. Examples are as follows:
System Settings. Device Manager. Policy & Objects.
If any of the pages are disabled, then it will not show as an option in FortiManager GUI.
For managing Administrative Domains (ADOMs), the system settings need to be enabled for the page to be available.
To configure, navigate to System Settings -> Admin Profiles -> Create New.
The configuration should be as follows:
System Settings: Read Only.
Administrative Domain: Read-Write.
All other fields: None.
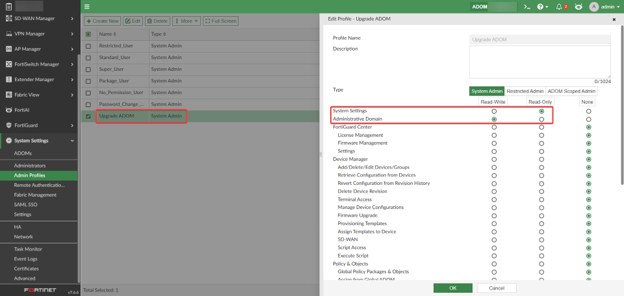
Select OK to save the config. Then navigate to the System Settings -> Administrators -> Create new or edit existing admin.
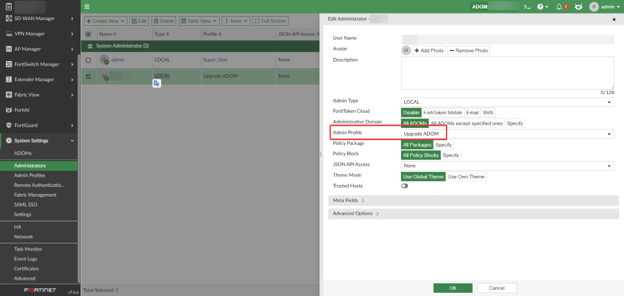
Ensure the 'Admin Profile' field is populated with the newly created profile. Select OK to save the configuration.
Verify by logging in with the admin credentials, and the admin should only be able to see the following pages:
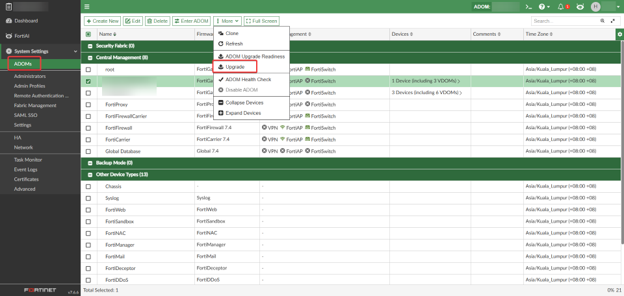
The admin can only perform actions on ADOMs, for example, upgrade, delete, and create a new one.
While other pages in the System Settings sub-directory are available, the admin can only 'read' and unable to perform any actions.
It is not possible to allow the admin to be able to view only System Settings -> ADOMs as the whole system settings directory needs to be enabled for the admin to access the ADOMs page.
|