mvlasak
Staff
Staff
March 31, 2026

Technical Tip: Configuring Geo-Redundant HA with VRRP Failover on FortiManager

  • March 31, 2026
  • 0 replies
  • 589 views
Description

This article describes the configuration of a simple Geo-Redundant High Availability (HA) cluster using two FortiManager-VM64 instances located in different subnets. The design highlights the use of VRRP failover mode with a dummy Virtual IP (VIP), unicast communication between cluster nodes, and specific certificate requirements.

It also outlines considerations for deployments where firewalls exist between FortiManager devices, managed FortiGate devices, and administrative users, ensuring required communication paths are permitted for proper cluster operation and management.

Scope FortiManager-VM64 v7.6.6 and later.
Solution

Diagram.
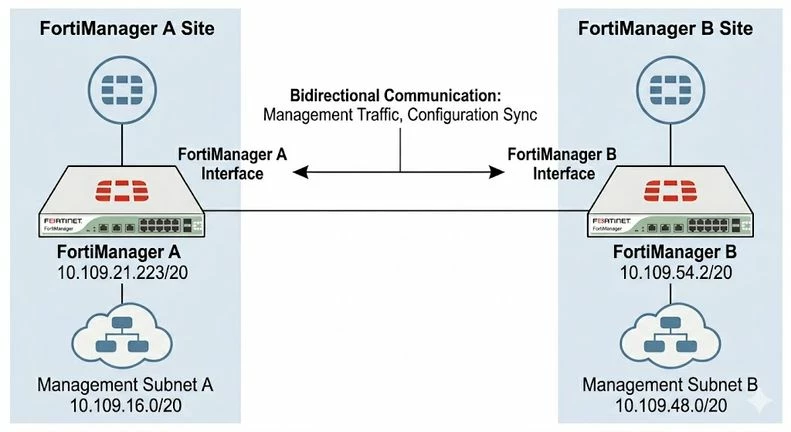
The following diagram illustrates the direct connection between the two FortiManager units across their respective subnets without an intermediary firewall.


FMG-geo-vrrp-ha.jpg


Components and requirements:

  • FortiManager A (Primary): 10.109.21.223/20 (Subnet A).
  • FortiManager B (Secondary): 10.109.54.2/20 (Subnet B).
  • Interface: Only 'port1' is used for both management and HA heartbeat traffic.
  • Unicast: Enabled (required for communication across different subnets/L3 boundaries).
  • Certificate: Both units must use the 'Fortinet_Local' certificate for HA authentication.


Configuration.

  1. Primary Unit (FortiManager A).


config system ha
    set failover-mode vrrp
    set mode primary
        config peer
            edit 1
                set ip 10.109.54.2
                set serial-number "FMGVMSTM25001XXXX"
            next
        end
    set clusterid 5
    set local-cert "Fortinet_Local"
    set password malape
    set priority 253
    set unicast enable
    set vip "192.168.11.2"
    set vrrp-interface "port1"
end


  1. Secondary Unit (FortiManager B).


config system ha
    set failover-mode vrrp
    set mode secondary
        config peer
            edit 1
                set ip 10.109.21.223
                set serial-number "FMGVMSTM2500YYYY"
            next
        end
    set clusterid 5
    set local-cert "Fortinet_Local"
    set password malape
    set unicast enable
    set vip "192.168.11.2"
    set vrrp-interface "port1"
end


Key Considerations and important notes.

  • Dummy VIP: In this Geo-Redundant VRRP configuration, the Virtual IP (VIP) address (e.g., 192.168.11.2) acts as a 'dummy' identifier. While it is not used for routing in this specific L3 setup, the VIP must be identical on both cluster units for the HA state machine to synchronize correctly.
  • Monitored IP: Although the official documentation mentions monitored IPs to trigger failover, it is not mandatory. In this simple configuration, the monitored IP can be removed or left unconfigured, and the cluster will rely on the peer connectivity and VRRP heartbeat.


  • Firewall Requirements (HA between Subnet A and Subnet B):
    If a firewall is introduced between Subnet A and Subnet B, the following traffic must be explicitly allowed bidirectionally:
  1. HA communication: TCP port 5199 (default) used for configuration synchronization.
  2. VRRP protocol: IP protocol 112 must be allowed for VRRP traffic.


Connectivity: Ensure the default gateway is correctly configured on both instances to allow the unicast packets to route between both subnets.


  • Firewall Requirements (Management access and device communication):

If a firewall is introduced between the management network (where FortiManager administrators are located) and either Subnet A / Subnet B (managed FortiGates / FortiManager devices), the following must be allowed:


  1. Administrative access: HTTPS (TCP 443) and SSH (TCP 22) from admin subnets to the devices.

  2. FGFM communication: TCP port 541 for FortiGate–FortiManager communication.


FortiManager v7.6.6 Admin Guide: Configuring geo-redundant HA with VRRP failover.

    Thought Leadership Security Summit. Outpace New Threats with AI - enhanced defense. Tuesday, Septmeber 15, 8:30 AM - 2:30 PM PT. The Golf Club at Newcastle, WA.
    Virtual event | September 2026. SASE summit. The age of autonomous trust. Register here!