
Troubleshooting Tip: URL re-written but user able to access malicious website
| Description | In this article is described how to troubleshoot why a suspicious URL is re-written but user is still able to access website. |
| Scope | FortiMail. |
| Solution | To troubleshoot this scenario, check if these two different protection mechanisms are enabled:
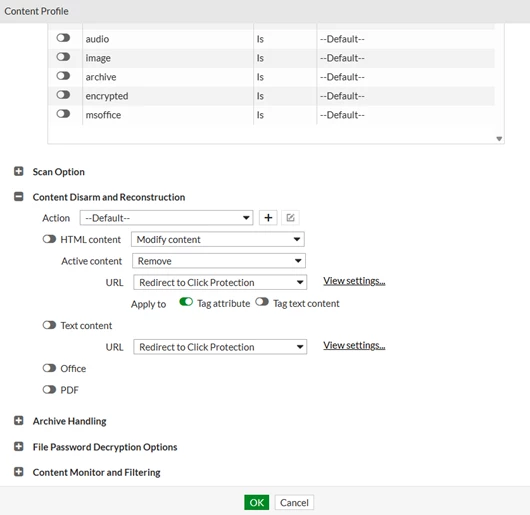
For (1), check Profile -> Content -> Content -> 'CF_Inbound' content profile, as in Figure 1. This settings aim to sanitize email that contains hyperlinks and scripts, including in attachments, in order to reduce risk of spam, malware, and tracking.
Figure 1: Content disarm and reconstruction.
In this case, HTML content are modified using the following settings 'Redirect to Click Protection'. This means that if the user selects the URL, it scans the URL and then performs the click protection action configured in (2).
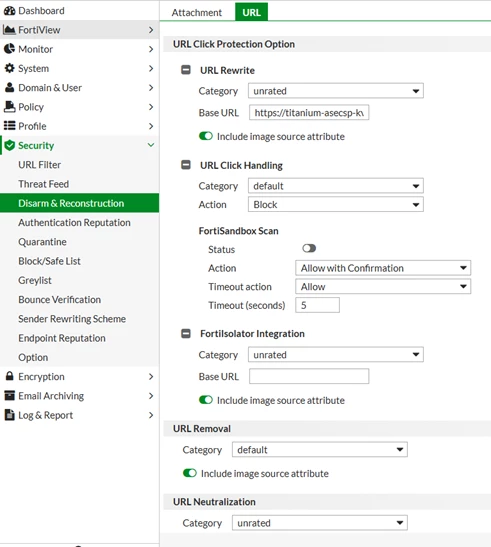
Depending on the inspection results from FortiGuard and FortiSandbox, decide if users should be allowed to access the URLs or block them.
Figure 2: URL click protection.
When the user opens the email URL at a later time, the URL request goes through FortiMail for a second rating query. If the URL rating changes from unrated to a malicious rating, FortiMail is then able to block the request.
If the rating is not changed, the request will succeed.
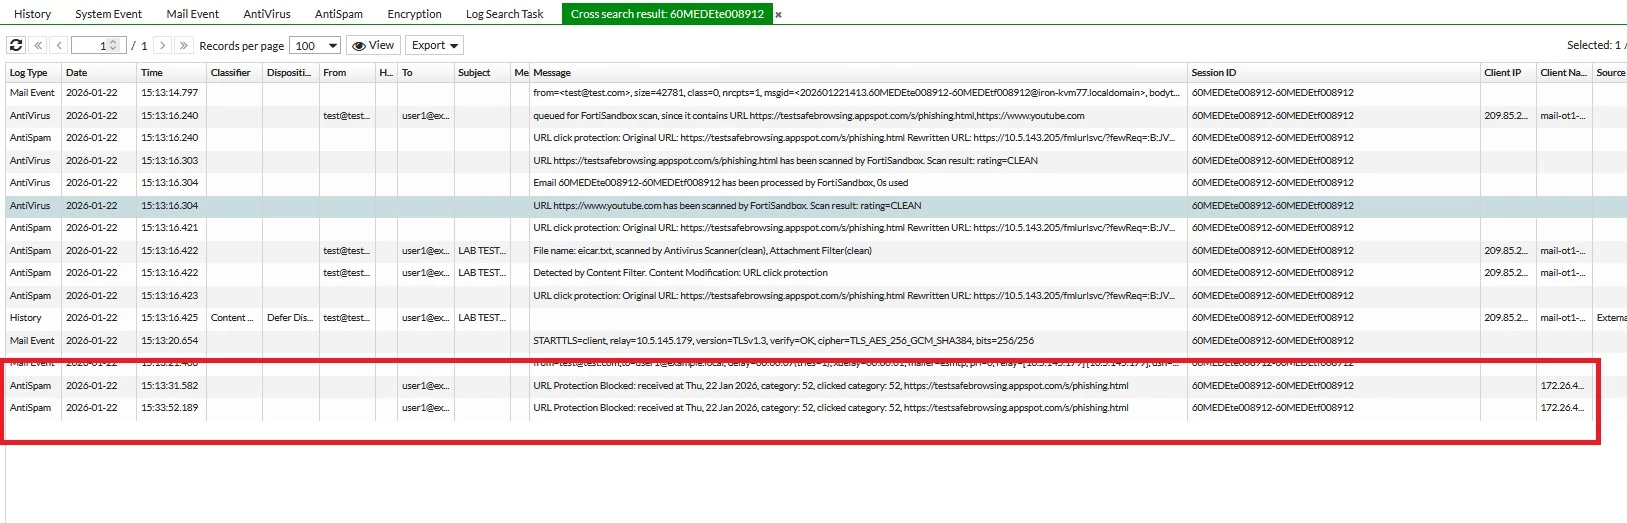
Example logs where the URL rating was not changed even after 20 minutes and FortiMail kept it blocked:
Related documents: |