melkady
Staff
Staff
November 12, 2025

Technical Tip: Using session profile safelisting to bypass remaining antispam checks

  • November 12, 2025
  • 0 replies
  • 353 views
Description

This article describes how to bypass antispam inspection for specific senders using an email address safelist entry within a Session Profile.

Scope FortiMail, all versions.
Solution

To allow a trusted sender to bypass remaining antispam checks:

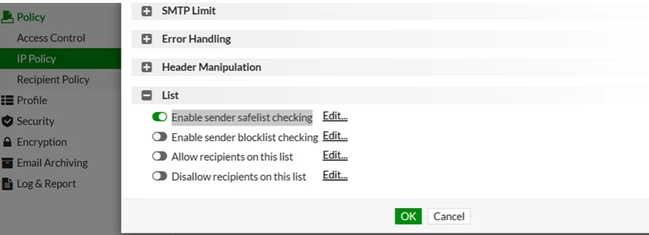
  1. Navigate to Policy -> IP Policy -> Find the Preferred Session Profile -> Edit.
  2. Under List, enable the option Enable sender safelist checking.


image.png


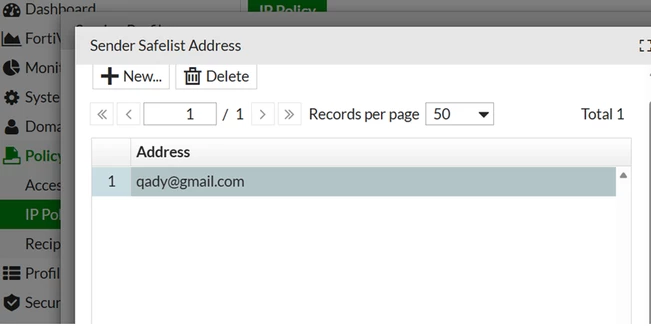
  1. Select Edit.

  2. Select New, then add the sender email address.


image.png

Emails matching this safelist entry will:

  • Bypass remaining AntiSpam checks.
  • Not bypass antivirus inspection.
  • Not bypass content checks.


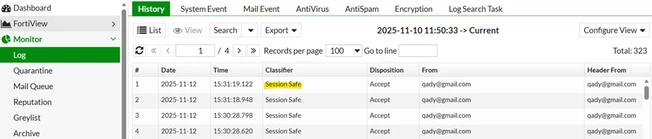
To confirm the behavior:

  1. Open Monitor -> Log.
  2. Locate the processed email.
  3. Verify the Classifier shows: Session Safe.
                                                                           

image.png


This indicates AntiSpam filtering was skipped due to the sender safelist.

    Thought Leadership Security Summit. Outpace New Threats with AI - enhanced defense. Tuesday, Septmeber 15, 8:30 AM - 2:30 PM PT. The Golf Club at Newcastle, WA.
    Virtual event | September 2026. SASE summit. The age of autonomous trust. Register here!