Technical Tip: Policy IDs column in FortiMail history log
Description
This article describes that an additional column called 'Policy IDs' was added to the History Log in FortiMail firmware v5.0. This is very useful in troubleshooting which policies or access controls are generating the log entries.
Scope
FortiMail.
Solution
Up to v5.4, the Policy ID value is separated into 3 different columns:
<Access Control> : <IP Policies> : <Recipient Policies>
For example: Policy IDs 9:1:3.
This means it is hitting Access Control ID 9, IP Policy 1 and Recipient Policy 3.
Note:
If no access control policies are matched, Fortimail will use the default access control policy which has the number '0' to relay inbound emails.
Starting from v5.4, there are 4 columns as FortiMail supports system-level and domain-level recipient policies.
<Access Control> : <IP Policies> : <Recipient Policies> :<SYSTEM/DOMAIN-NAME of Recipient>
For example:
Policy IDs 3:5:2:externaltest.com: This indicates that Access Control ID 3, IP Policy 5, and Domain-based Recipient Policy 2 were triggered.
Policy IDs 3:5:1:SYSTEM: This indicates that Access Control ID 3, IP Policy 5, and System-based Recipient Policy 1 were triggered.
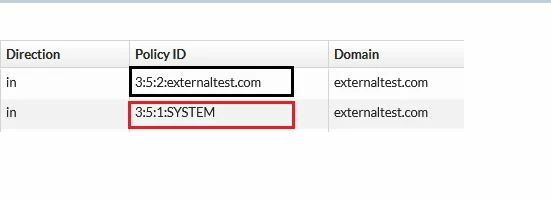
The last field displays a protected domain name like externaltest.com if the email matches a recipient-based policy. Otherwise, if it is an outbound email address or if there is no recipient domain-based policy, it displays SYSTEM.
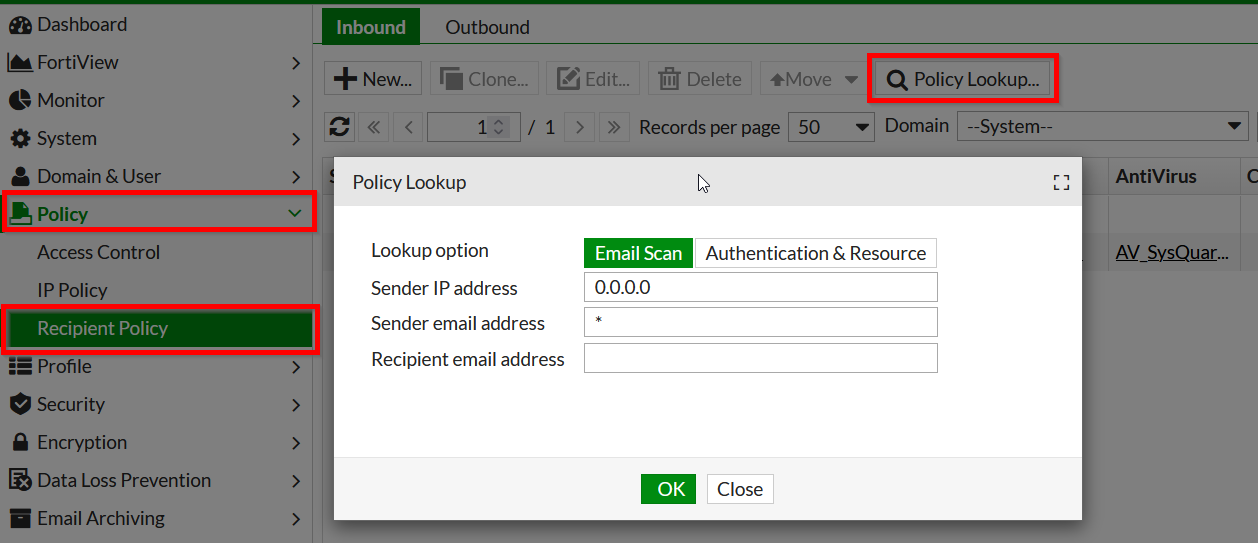
Note: There is also the Policy Lookup tool to determine which IP Policy and Recipient Policy are matched based on the sender’s IP address or the sender’s and recipient’s email addresses. See
Policy -> Recipient Policy -> Policy Lookup: