



Technical Tip: How to enable Header From Check on Access Control Rule
Description
This article describes how to enable a Header From Check on an Access Control Rule.
Scope
FortiMail v8.0.
Solution
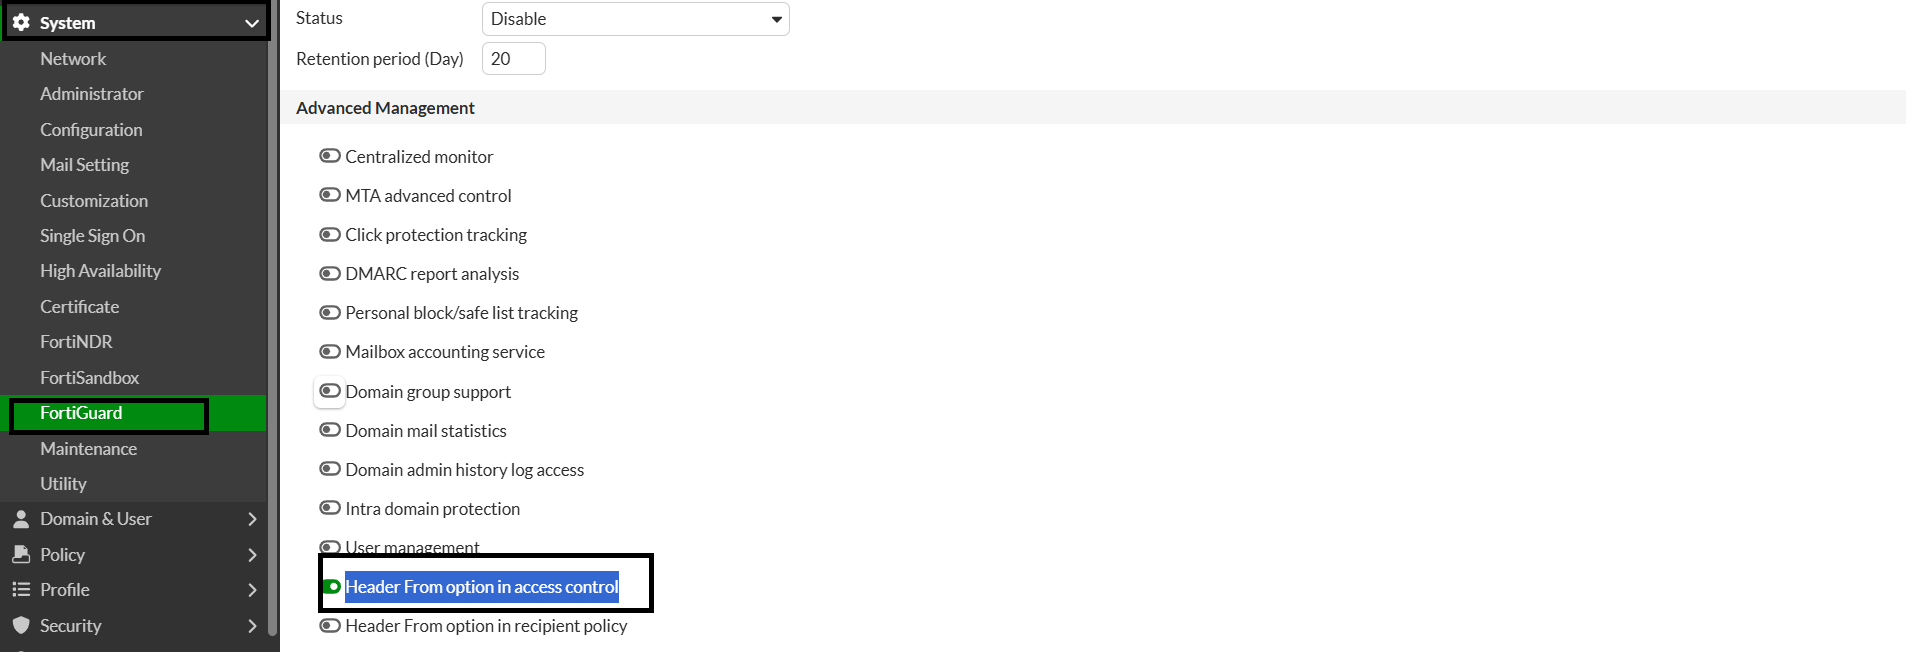
Enable the Header From option in access control.
GUI:
Note: An Advanced Management License is required to enable this option. In the GUI, navigate to the System -> FortiGuard -> Licensed Feature -> Advanced Management -> Header From option in access control, select 'Enable', and select Apply.
A message will appear stating 'Licensed feature setting has been changed. The GUI will now reload'.
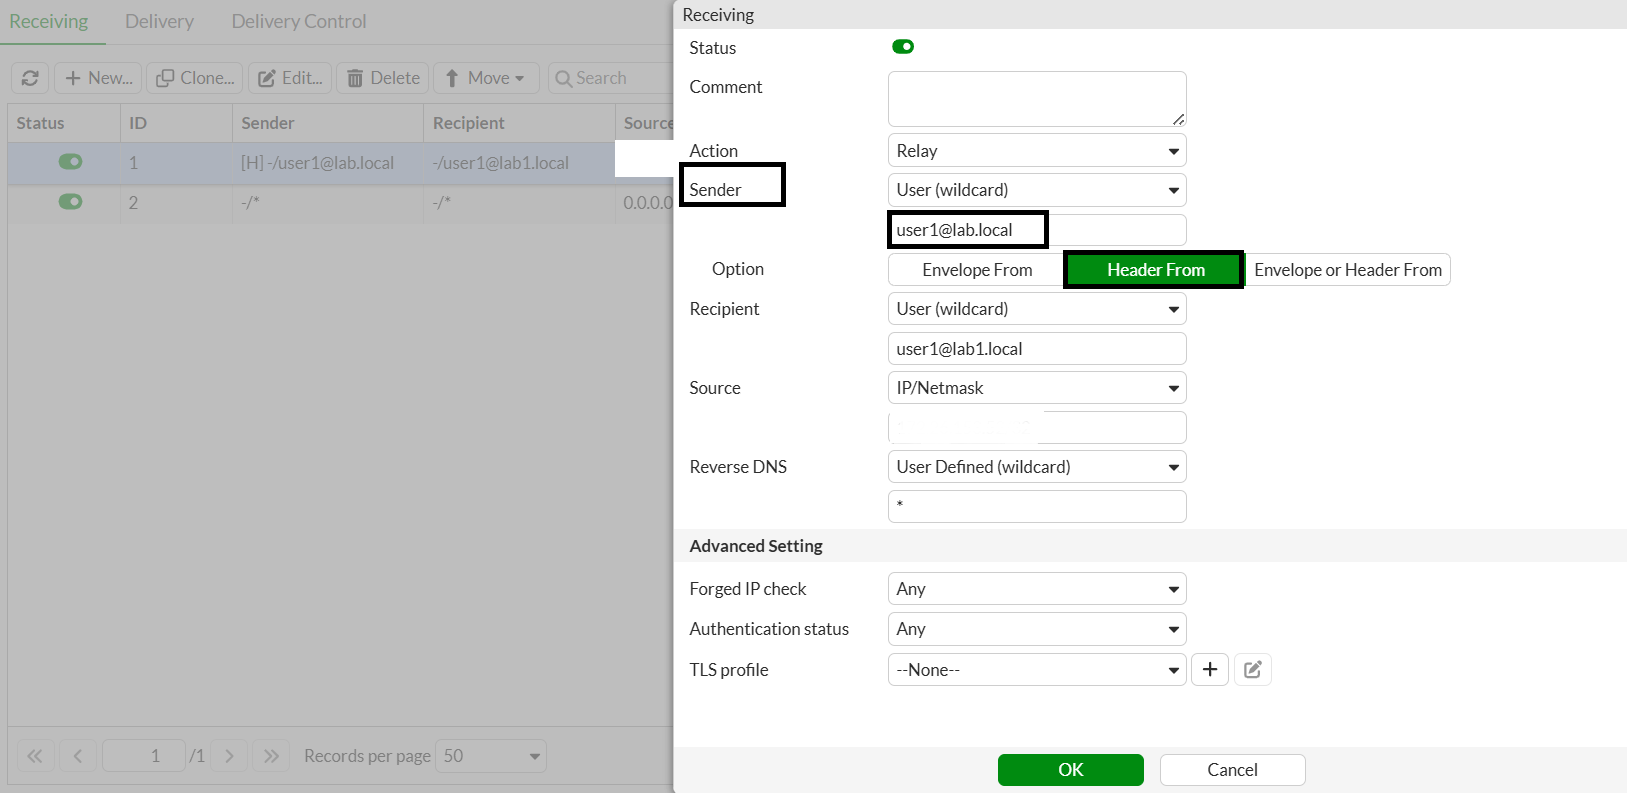
To create a new access control rule checking the Header From:
Navigate to Policy -> Access Control -> New -> Configure the rule parameters as needed -> Choose any of the following options: Envelope From, Header From, Envelope or header from.
CLI:
#config policy access-control receive
(receive)#edit <rule_id>
(1)#set sender-option {envelope-from | envelope-or-header-from | header-from}
(1)#end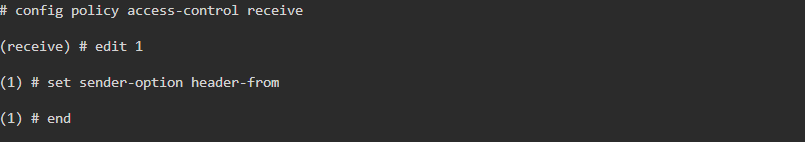
Results:
If an Email is sent with a different Header From as configured, it will not match the rule and will be moved to the next rule with the configured action. In this test, it is a deny rule.

If an Email is sent with the configured Header From, it will match the rule and the configured action will be taken.


