In this example, sites belonging to the 'Gambling' category cannot be blocked because those sites use ECH. Here is the Web Filter configured to block this category: Examples: 1xbets-ar.com. bets-ar.com.
Diagram:
Client-PC ----> [VLAN1] FortiGate [SD-WAN] ----> Internet.
config firewall policy
    edit 25
        set srcintf "VLAN1"
        set dstintf "SD-WAN"
        set action accept
        set srcaddr "pc-test"
        set dstaddr "all"
        set schedule "always"
        set service "HTTPS" "HTTP" "DNS" "Quic"
        set utm-status enable
        set inspection-mode flow
        set ssl-ssh-profile "certificate-inspection_Alumnos"
        set av-profile "AV_Alumnos"
        set webfilter-profile "NavegacionAlumnos"
        set dnsfilter-profile "DF-Alumnos"
        set application-list "AC-Alumnos"
        set logtraffic all
        set auto-asic-offload disable
        set nat enable
    next
end
config webfilter profile
    edit "NavegacionAlumnos"
        set feature-set flow
        ...
            config filters
            ...
                edit 11
                    set category 11
                    set action block
                    set log enable
                next
                ...
            end
        set rate-javascript-urls enable
        set rate-css-urls enable
        set rate-crl-urls enable
end
  ...
    next
end
With the previous configuration, the sites cannot be blocked, identifying that those sites use ECH, generating logs like the following:
date=2025-08-08 time=12:38:16 eventtime=1754667495655478890 tz="-0300" logid="1702062103" type="utm" subtype="ssl" eventtype="ssl-negotiation" level="information" vd="root" action="info" policyid=25 poluuid="916a1a8a-ab4a-51ef-8238-c0f79567272e" policytype="policy" sessionid=54164787 service="SSL" profile="certificate-inspection_Alumnos" srcip=10.1.1.35 srcport=64432 srccountry="Reserved" dstip=172.67.178.119 dstport=443 dstcountry="United States" srcintf="VLAN1" srcintfrole="lan" dstintf="wan2" dstintfrole="wan" srcuuid="bc5355aa-c400-51ed-6f23-4fa5e520c8f9" dstuuid="5a9b4e2a-bf4c-51ed-dc50-e448f485ac50" proto=6 sni="cloudflare-ech.com" eventsubtype="encrypted-client-hello" hostname="cloudflare-ech.com"
There are two different ways to block ECH currently in the FortiGate:
Method 1: This method uses an SSL profile certificate-inspection.
To achieve the desired behavior, apply the following configuration changes within the SSL profile: config firewall ssl-ssh-profile
edit "certificate-inspection_Alumnos"
config https
set ports 443
set status certificate-inspection
set quic inspect
set unsupported-ssl-cipher block
set encrypted-client-hello allow
end
end
end
The SNI can be filtered by using the 'ech-outer-sni' under ssl-ssh-inspection profile settings:
config firewall ssl-ssh-profile
    edit "certificate-name"
        config ech-outer-sni
            edit <name>
                set sni <string>
            next
        end
    next
end
For example, for the SNI 'cloudflare-ech':
config firewall ssl-ssh-profile
    edit "certificate-name"
        config ech-outer-sni
            edit cloudflare
                set sni cloudflare-ech
            next
        end
    next
end
After those changes, even if the Gambling websites use ECH, the FortiGate will be able to block them:
date=2025-09-24 time=14:30:24 eventtime=1758735023765172940 tz="-0300" logid="1704062220" type="utm" subtype="ssl" eventtype="ssl-handshake" level="information" vd="root" action="info" policyid=25 poluuid="916a1a8a-ab4a-51ef-8238-c0f79567272e" policytype="policy" sessionid=28987146 service="SSL" profile="certificate-inspection_Alumnos" srcip=10.1.1.35 srcport=50293 srccountry="Reserved" dstip=104.21.93.125 dstport=443 dstcountry="United States" srcintf="VLAN1" srcintfrole="lan" dstintf="wan2" dstintfrole="wan" srcuuid="bc5355aa-c400-51ed-6f23-4fa5e520c8f9" dstuuid="5a9b4e2a-bf4c-51ed-dc50-e448f485ac50" proto=6 tlsver="tls1.3" sni="1xbets-ar.com" cipher="0x1301" authalgo="ecdsa" kxproto="ecdhe" kxcurve="x25519" eventsubtype="handshake-done" hostname="1xbets-ar.com" handshake="full" mitm="yes"
date=2025-09-24 time=14:30:24 eventtime=1758735023535901859 tz="-0300" logid="0316013056" type="utm" subtype="webfilter" eventtype="ftgd_blk" level="warning" vd="root" policyid=25 poluuid="916a1a8a-ab4a-51ef-8238-c0f79567272e" policytype="policy" sessionid=28987145 srcip=10.1.1.35 srcport=50292 srccountry="Reserved" srcintf="VLAN1" srcintfrole="lan" srcuuid="bc5355aa-c400-51ed-6f23-4fa5e520c8f9" dstip=104.21.93.125 dstport=80 dstcountry="United States" dstintf="wan2" dstintfrole="wan" dstuuid="5a9b4e2a-bf4c-51ed-dc50-e448f485ac50" proto=6 httpmethod="GET" service="HTTP" hostname="1xbets-ar.com" agent="Mozilla/5.0 (Windows NT 10.0; Win64; x64; rv:143.0) Gecko/201001" profile="NavegacionAlumnos" action="blocked" reqtype="direct" url="http://1xbets-ar.com/" sentbyte=355 rcvdbyte=0 direction="outgoing" msg="URL belongs to a denied category in policy" cat=11 catdesc="Gambling" ratemethod="domain"
This traffic can be observed in a Wireshark capture output. After ECH is blocked, the client requests the destination hostname in plaintext (the client hello is not encrypted). As a result, certificate inspection can be performed properly to block URLs based on FortiGuard categories
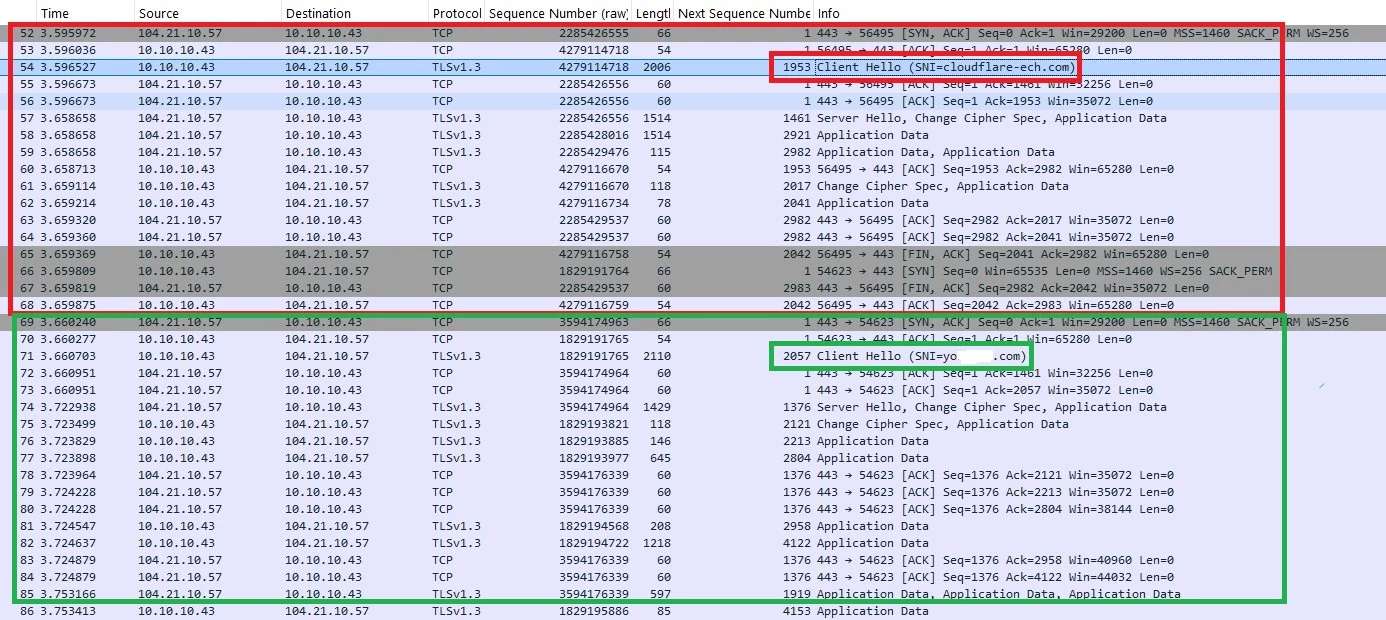 Note 1: For deep-inspection mode, ECH is stripped automatically, which is why it works properly. In certificate-inspection mode, ECH must be blocked at SSL profile level first. Otherwise, Webfilter cannot extract hostname and category filtering will not apply.
Handling of Encrypted SNI (ECH) in proxy-mode is supported from FortiOS v7.4.4 and above.
Release Notes 7.4.4
Feature ID - 968303: Add support to control TLS connections that utilize Encrypted Client Hello (ECH), with options to block, allow, or force the client to switch to a non-ECH TLS connection.
Note 2:
For flow-based inspection, the Encrypted ClientHello (ECH) feature is supported from FortiOS v7.6.3 and above:
Release Notes 7.6.3
Feature ID - 1025233: Flow mode can block TLS ClientHello that uses ECH, allowing TLS to fall back to using a plaintext ClientHello
Method 2:
This approach requires enabling a specific option in the DNS filter profile that is applied to the policy. 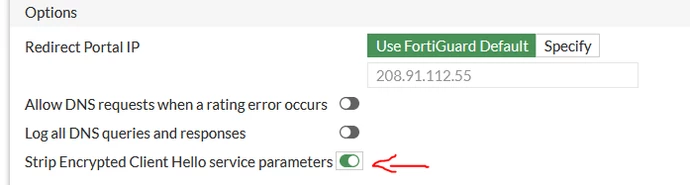 ECH is set up via DNS over HTTPS, and this option prevents that process from completing.
For more information on how ECH and the FortiGate interact, see Control TLS connections that utilize Encrypted Client Hello 7.4.4. Method 3: Block ECH-Related Domain : *cloudflare-ech*. *whos.amung*. Note: For v7.2.x, only Method 3 works.
Related article:
Technical Tip: FortiGate Fails to block HTTPS website due to encrypted traffic |