| Assuming FortiGate HA has the following IP configuration: Active FortiGate: port1 (external) - 172.17.0.4 (primary IP) 172.17.0.6 (secondary IP) 172.17.0.7 (secondary IP) port2 (internal) - 172.17.0.68 port3 (HASync) - 172.17.0.132 port4 (HAMgmt) - 172.17.0.196 Passive FortiGate: port1 (external) - 172.17.0.5 (primary IP) 172.17.0.8 (secondary IP) 172.17.0.9 (secondary IP) port2 (internal) - 172.17.0.69 port3 (HASync) - 172.17.0.133 port4 (HAMgmt) - 172.17.0.196 SDN configuration. config system sdn-connector edit "AzureSDN" set type azure set use-metadata-iam disable set ha-status enable set tenant-id "XXXXXX" set client-id "XXXXXX" set client-secret XXXXX set subscription-id "XXXXX" set resource-group "SYAO-RG" config nic edit "FGT-FGT-A-Nic1" config IP edit "ipconfig1" set public-ip "YAOS-FGT-PIP" next edit "ipconfig2" set public-ip "YAOS-FGT-PIP-2" next edit "ipconfig3" set public-ip "YAOS-FGT-PIP-3" next end next end config route-table edit "FGT-RouteTable-ProtectedSubnet" config route edit "toDefault" set next-hop "172.17.0.68" next end next end end Secondary:
config system sdn-connector edit "AzureSDN" set type azure set use-metadata-iam disable set ha-status enable set tenant-id "XXXXXX" set client-id "XXXXXX" set client-secret XXXXX set subscription-id "XXXXX" set resource-group "SYAO-RG" config nic edit "FGT-FGT-B-Nic1" config ip edit "ipconfig1" set public-ip "YAOS-FGT-PIP" next edit "ipconfig2" set public-ip "YAOS-FGT-PIP-2" next edit "ipconfig3" set public-ip "YAOS-FGT-PIP-3" next end next end config route-table edit "FGT-RouteTable-ProtectedSubnet" config route edit "toDefault" set next-hop "172.17.0.69" next end next end end Run the following debug commands in Secondary FortiGate:
diagnose debug application azd -1
diagnose debug application azd-ha -1 diagnose debug console timestamp enable diagnose debug enable - FortiGate identifies itself as the Primary node in the cluster.
- The SDN connector searches for resources within the SYAO-RG resource group.
- It examines the public IP resources and retrieves their IP configuration IDs.
FGT-FGT-B # 2024-11-06 19:07:18 HA event
2024-11-06 19:07:21 HA state: primary
2024-11-06 19:07:21 AzureSDN: resourcegroup: SYAO-RG, sub: <--your subscription ID-->
2024-11-06 19:07:21 get pubip YAOS-FGT-PIP in resource group SYAO-RG
2024-11-06 19:07:21 found pub ip YAOS-FGT-PIP in resource group SYAO-RG
2024-11-06 19:07:21 ipconfig id: /subscriptions/<--your subscription ID-->/resourceGroups/SYAO-RG/providers/Microsoft.Network/networkInterfaces/FGT-FGT-A-Nic1/ipConfigurations/ipconfig1
2024-11-06 19:07:21 get pubip YAOS-FGT-PIP-2 in resource group SYAO-RG
2024-11-06 19:07:21 found pub ip YAOS-FGT-PIP-2 in resource group SYAO-RG
2024-11-06 19:07:21 ipconfig id: /subscriptions/<--your subscription ID-->/resourceGroups/SYAO-RG/providers/Microsoft.Network/networkInterfaces/FGT-FGT-A-Nic1/ipConfigurations/ipconfig2
2024-11-06 19:07:21 get pubip YAOS-FGT-PIP-3 in resource group SYAO-RG
2024-11-06 19:07:21 found pub ip YAOS-FGT-PIP-3 in resource group SYAO-RG
2024-11-06 19:07:21 ipconfig id: /subscriptions/<--your subscription ID-->/resourceGroups/SYAO-RG/providers/Microsoft.Network/networkInterfaces/FGT-FGT-A-Nic1/ipConfigurations/ipconfig3
2024-11-06 19:07:21 Disable interface: port1
2024-11-06 19:07:22 Disable interface: port2 - Detach the public IPs from FGT-FGT-A-NIC1.
- Attach the public IPs to FGT-FGT-B-NIC1.
2024-11-06 19:07:22 removing pubip
2024-11-06 19:07:22 query nic FGT-FGT-A-Nic1
2024-11-06 19:07:22 query nic FGT-FGT-A-Nic1, rc: 0
2024-11-06 19:07:22 remove public ip YAOS-FGT-PIP in ipconfig ipconfig1 of nic FGT-FGT-A-Nic1
2024-11-06 19:07:22 remove public ip YAOS-FGT-PIP-3 in ipconfig ipconfig3 of nic FGT-FGT-A-Nic1
2024-11-06 19:07:22 remove public ip YAOS-FGT-PIP-2 in ipconfig ipconfig2 of nic FGT-FGT-A-Nic1
2024-11-06 19:07:22 updating nic: FGT-FGT-A-Nic1
2024-11-06 19:07:24 updating nic: FGT-FGT-A-Nic1, rc: 0
2024-11-06 19:07:24 operation: "updating nic: FGT-FGT-A-Nic1", status: InProgress
2024-11-06 19:07:30 operation: "updating nic: FGT-FGT-A-Nic1", status: InProgress
2024-11-06 19:07:35 operation: "updating nic: FGT-FGT-A-Nic1", status: InProgress
2024-11-06 19:07:40 operation: "updating nic: FGT-FGT-A-Nic1", status: InProgress
2024-11-06 19:07:45 operation: "updating nic: FGT-FGT-A-Nic1", status: InProgress
2024-11-06 19:07:50 operation: "updating nic: FGT-FGT-A-Nic1", status: InProgress
2024-11-06 19:07:55 operation: "updating nic: FGT-FGT-A-Nic1", status: Succeeded
2024-11-06 19:07:55 adding pubip
2024-11-06 19:07:55 query nic FGT-FGT-B-Nic1
2024-11-06 19:07:56 query nic FGT-FGT-B-Nic1, rc: 0
2024-11-06 19:07:56 add public ip YAOS-FGT-PIP in ipconfig ipconfig1 of nic FGT-FGT-B-Nic1
2024-11-06 19:07:56 add public ip YAOS-FGT-PIP-3 in ipconfig ipconfig3 of nic FGT-FGT-B-Nic1
2024-11-06 19:07:56 add public ip YAOS-FGT-PIP-2 in ipconfig ipconfig2 of nic FGT-FGT-B-Nic1
2024-11-06 19:07:56 updating nic: FGT-FGT-B-Nic1
2024-11-06 19:07:57 updating nic: FGT-FGT-B-Nic1, rc: 0
2024-11-06 19:08:03 operation: "updating nic: FGT-FGT-B-Nic1", status: InProgress
2024-11-06 19:08:08 operation: "updating nic: FGT-FGT-B-Nic1", status: InProgress
2024-11-06 19:08:13 operation: "updating nic: FGT-FGT-B-Nic1", status: Succeeded - Update the Default route entry in the route table with a next hop IP of 172.17.0.69.
- Display the latest interface configuration of the VM (note: the other two public IPs are not shown here; it is possible to use the command 'diag test app azd 6' for details).
2024-11-06 19:08:13 query route table FGT-RouteTable-ProtectedSubnet in resource group SYAO-RG of subscription <--your subscription ID-->
2024-11-06 19:08:13 route table query, rc: 0
2024-11-06 19:08:13 matching route:toDefault:toDefault
2024-11-06 19:08:13 set route toDefault nexthop 172.17.0.69
2024-11-06 19:08:13 updating route table FGT-RouteTable-ProtectedSubnet in resource group SYAO-RG of subscription <--your subscription ID-->
2024-11-06 19:08:14 updating route table FGT-RouteTable-ProtectedSubnet in resource group SYAO-RG of subscription <--your subscription ID-->, rc: 0
2024-11-06 19:08:14 operation: "updating route table FGT-RouteTable-ProtectedSubnet in resource group SYAO-RG of subscription <--your subscription ID-->", status: Succeeded
2024-11-06 19:08:14 Enable interface: port1
2024-11-06 19:08:14 Enable interface: port2
2024-11-06 19:08:14 refreshing public IP in interface config
2024-11-06 19:08:14 azd getting instance metadata
2024-11-06 19:08:15 NIC: 172.17.0.5, public IP: 52.187.167.185
2024-11-06 19:08:15 NIC: 172.17.0.69
2024-11-06 19:08:15 NIC: 172.17.0.133
2024-11-06 19:08:15 NIC: 172.17.0.197, public IP: 13.76.31.34
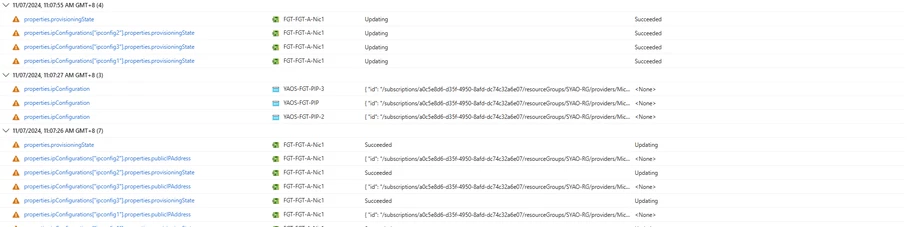
It is also possible to check the changes from the Azure activity event log-change analysis:
Removing public IP from the Primary FortiGate:
Attaching the public IP to the Secondary FortiGate and updating the route entry: 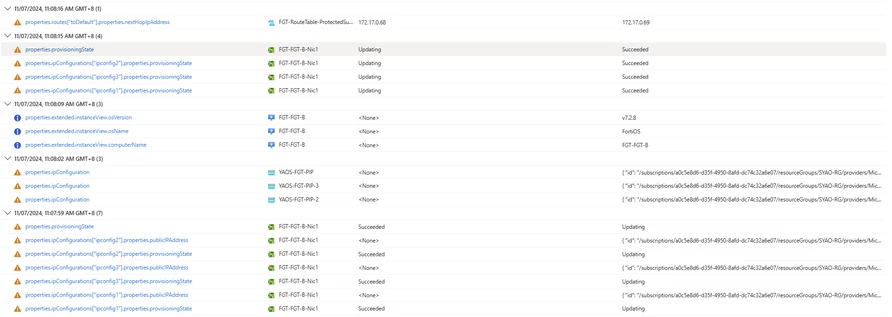
| 




