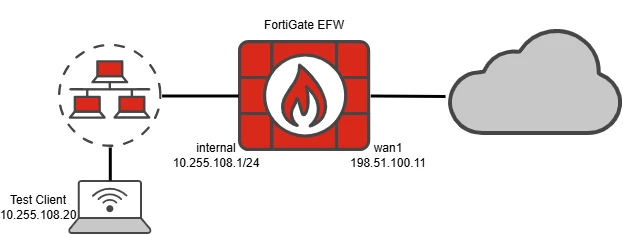
Troubleshooting Tip: Using Port Block Allocation IP pools to correlate packet captures taken before and after source NAT
| Description | This article describes a method to enforce a particular source port range for a local test client's internet traffic and demonstrates example filters to capture this traffic on firewall internal and external-facing interfaces. |
| Scope | FortiGate |
| Solution | Use Case: When troubleshooting network issues, it can be useful to restrict the focus to a particular test client and test firewall policy and take packet captures on the firewall. On internal networks without NAT, the test client’s traffic can be easily isolated for packet capture using an IP address filter. However, filtering traffic on WAN interfaces performing NAT can be a challenge.
In smaller enterprise environments, there is often only one public IP address available, and all Internet-bound traffic egresses the firewall using the same source IP address. Since only one IP address is used, the test traffic cannot be isolated using an IP address. Configuring a port block allocation (PBA) IP pool on a test policy makes it possible to filter for test traffic using a port range.
Example Configuration:
config firewall address edit "h-10.255.108.20" set subnet 10.255.108.20 255.255.255.255 next end
config firewall ippool edit "pba-198.51.100.11" set type port-block-allocation set startip 198.51.100.11 set endip 198.51.100.11 set num-blocks-per-user 1 next end
config firewall policy edit <index> set name "Test Client Internet Access" set srcintf "internal" next end
When this configuration is applied and the test policy is placed above the existing internet policy, all internet TCP and UDP traffic from the example client 10.255.108.20 will be NATted with a predictable range of source ports.
diagnose firewall ippool list pba
Note:
TCP & UDP traffic: Perform packet captures in the CLI using the internal IP address for the LAN interface, and 'portrange' for the WAN interface.
diagnose sniffer packet internal 'host 10.255.108.20' 6 2000 l diagnose sniffer packet wan1 'portrange 5117-5244' 6 2000 l
ICMP Echo traffic (Ping): ICMP Echo Identifier is analogous to TCP and UDP ports for ICMP Echo (ping) traffic. The built-in libpcap-style options FortiOS provides cannot filter by this value directly, but a custom filter checking the 5th and 6th byte of icmp packets can be used to achieve the same effect, see below.
diagnose sniffer packet internal 'host 10.255.108.20' 6 2000 l Debug flow does not require PBA IP pool: Another commonly used troubleshooting tool is debug flow. This tool supports filtering directly based on the existing internal IP address and does not require any PBA ippool to capture both directions.
diagnose debug flow filter addr 10.255.108.20 diagnose debug enable diagnose debug flow trace start 2
To stop the debug:
diagnose debug reset diagnose debug disable
Related articles: Technical Tip: How Port Block Allocation Works in FortiGate Troubleshooting Tip: Advanced filters for FortiOS packet capture |