Troubleshooting Tip: Using Cloudflare DNS with DNS over TLS showing as unreachable
| Description | This article explains the behavior when utilizing Cloudflare DNS as FortiGate's DNS server. |
| Scope | FortiGate. |
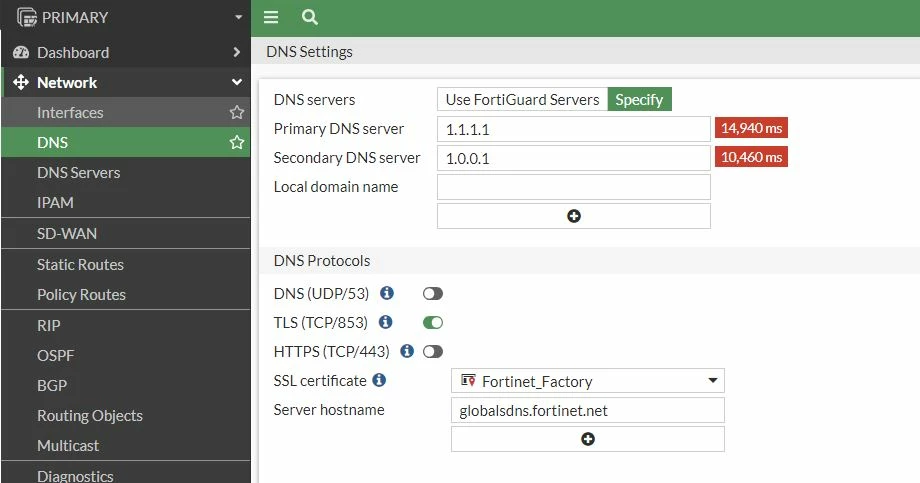
| Solution | When utilizing a third-party DNS server such as CloudFlare (1.1.1.1 & 1.0.0.1) in FortiGate and selecting TLS as the DNS Protocol, it will show as 'Unreachable'. As a result, FortiGate will not be able to resolve the hostname.
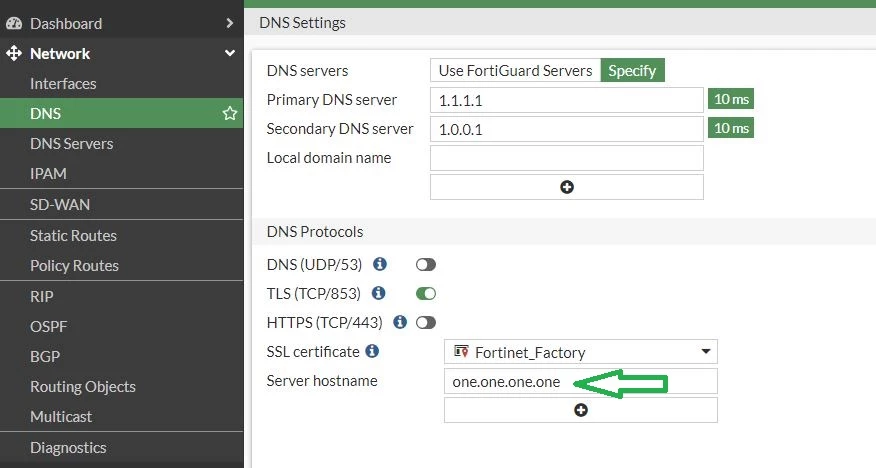
This is due to the server hostname mismatched with the DNS server IPs selected. To resolve this, it is needed to update the 'Server Hostname' under the DNS configuration.
config system dns set primary 1.1.1.1 end
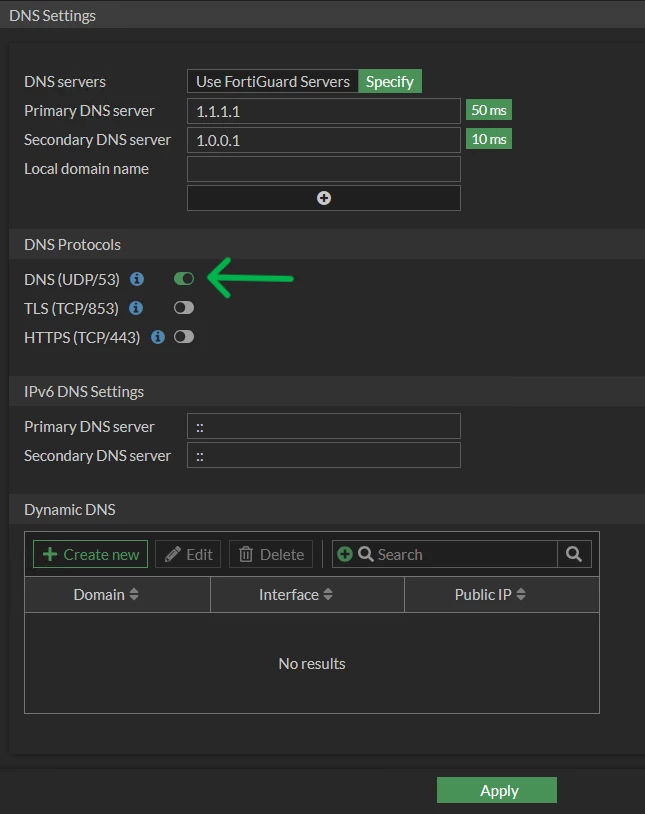
Alternatively, if utilizing TLS is not a requirement, then it is possible to enable the DNS protocol 'DNS (UDP/53)' and disable 'TLS (TCP/853)' instead. This configuration allows FortiGate to resolve hostnames without needing to specify the server hostname.
Related articles: Troubleshooting Tip: Google DNS with DNS over TLS showing as unreachable Technical Tip: DNS server is unreachable when using custom DNS |