Troubleshooting Tip: User cannot connect to an L2TP over IPsec tunnel and receives the following error 'port 4500: L2TPD encountered an internal error. This may be a sign that the firewall is low on resources.'
| Description | This article describes how to resolve the issue when a user is unable to connect using L2TP over IPsec and experiences the following error: 'port 4500: L2TPD encountered an internal error. This may be a sign that the firewall is low on resources.'. |
| Scope | FortiGate. |
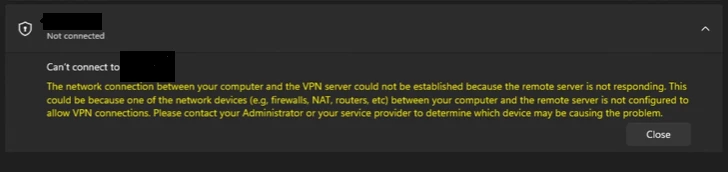
| Solution | The user is unable to connect to L2TP over IPsec despite the configuration being correct. Configuration guide: L2TP over IPsec The user encounters the following error while connecting to the tunnel:
Run IKE and L2TP debug commands while attempting to connect:
diagnose debug reset diagnose debug application ike -1 diagnose debug application l2tp -1 diagnose debug console time enable
To stop the debug:
diagnose debug disable
After the IPsec tunnel is established, the L2TP negotiation takes place,e and it shows the following error.
2025-07-02 11:12:16 handle_one_network_packet()-154: Received L2TP packet from xx.xx.xx.xx:4500, len=105, tun=0, call=0
The FortiGate is using optimal resources, and the cause is not due to high CPU or memory utilization.
Restarting the L2TP process can resolve the issue temporarily: 'fnsysctl killall l2tpd'. However, after some time, the problem can reappear.
The proper workarounds are either:
config vpn l2tp set enforce-ipsec enable
config vpn l2tp
Note: This issue has been identified as Bug 1169860 and has been resolved in versions 7.4.9, 7.6.4, 8.0.0, and later. |