



Troubleshooting Tip: Unable to select high encryption options such as 3DES or AES when configuring the IPsec tunnel
Description | This article describes a situation where high-encryption 3DES and AES cannot be selected in the IPsec tunnel configuration, along with potential causes for this issue. |
Scope | Applicable to FortiGate versions. |
Solution | Check device compatibility: It is important to ensure that the hardware or software FortiGate device supports high encryption algorithms, as some older devices may not support AES or 3DES.
This is how it looks when configuring over the GUI:
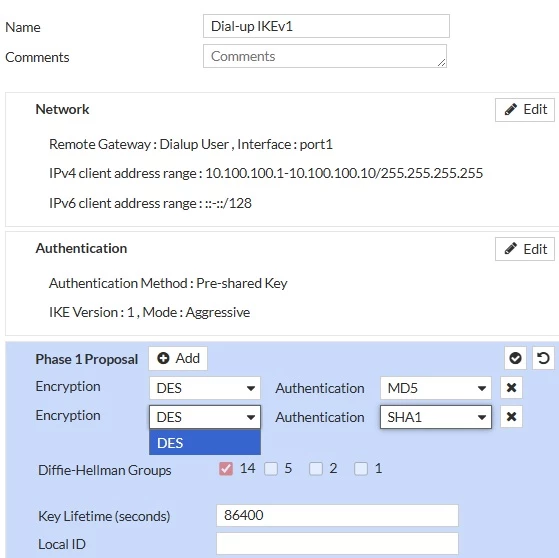
Consider the following example:
The FortiGate device displays a license status of Low-Encryption (LENC), indicating that it supports only low encryption algorithms.
In cases like this, it is recommended to upgrade to a full encryption device by acquiring a strong encryption upgrade license key.
In order to apply a strong encryption license key (or to apply a LENC key) obtained for the device, use the following command:
Note: The LENC license also utilizes TLS version 1.0, which is deprecated and no longer supported by FortiGuard Server. As a result, validation attempts are unsuccessful due to the inability to negotiate a more secure encryption cipher with this license. More information here:
|
