



Troubleshooting Tip: Troubleshooting FortiGate Authorization Issues in FortiManager
Description
This article describes the troubleshooting steps for resolving issues when attempting to authorize a FortiGate device in FortiManager.
Scope
FortiGate v7.2.8.
Solution
After completing the central management configuration on the FortiGate, the device needs to be authorized in FortiManager. However, during the authorization process, it gets stuck at 5%.
The below response can be seen on the FortiManager debug:
Response:
{ "id": 1, "result": [{ "status": { "code": 2, "message": "no permission"}, "url": "start\/tunnel"}]}
Response [unknown]:
{ "id": 1, "result": [{ "status": { "code": 2, "message": "no permission"}, "url": "start\/tunnel"}]}
Response [unknown]:
{ "id": 1, "result": [{ "status": { "code": 2, "message": "no permission"}, "url": "start\/tunnel"}]}
__on_state,469: dev_oid=163, start_tunnel, done, events=8 r=0
__on_start_tunnel_cb,379: dev_oid=163, start tunnel failed, error 2(noperm)
Starting from v7.2.8:
As part of a security enhancement, FortiGate requires specific configurations when initiating connections to an on-premise FortiManager for central management. Administrators must configure FortiManager's serial number in the central management settings before establishing the connection via CLI.
So set the FortiManager serial number too under the FortiGate central Management Configuration, and then the device can be authorized.
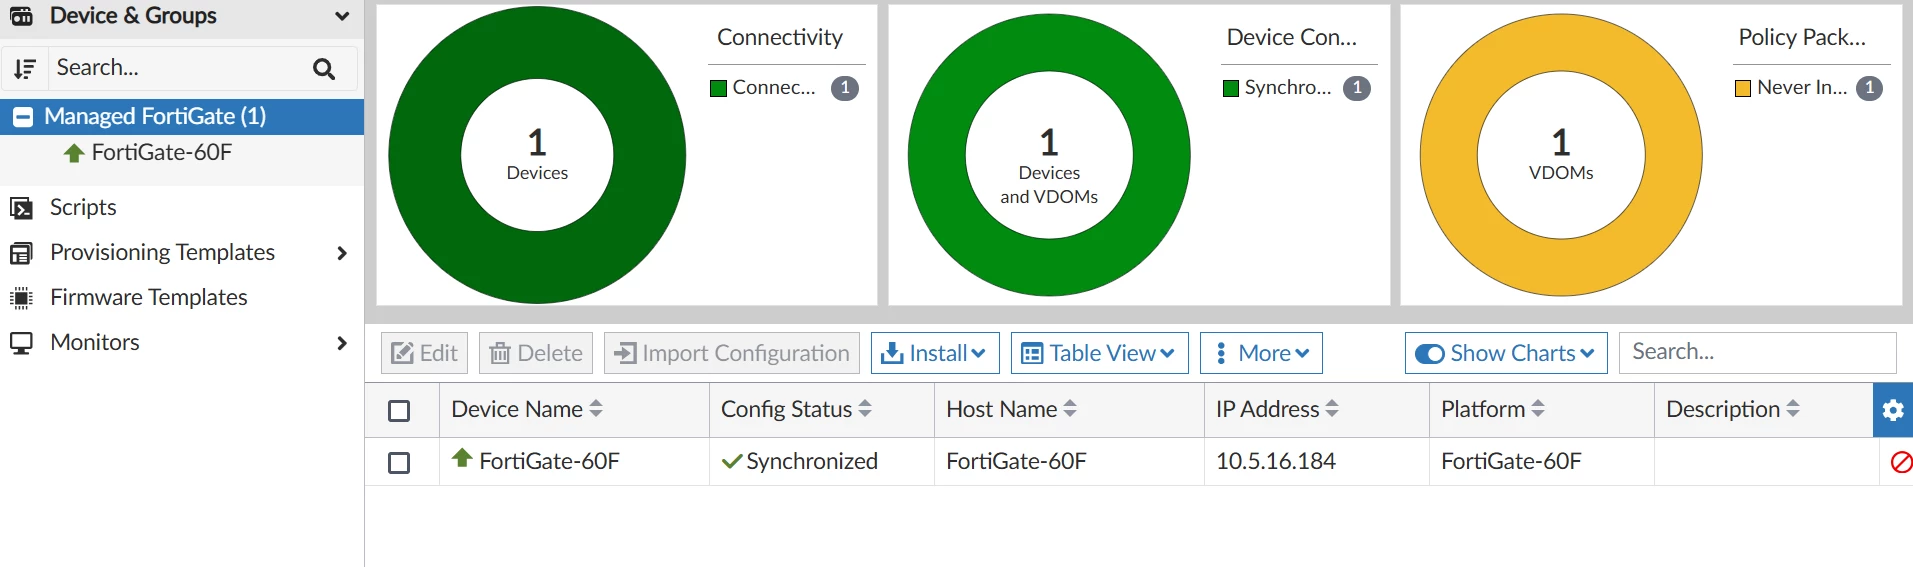
To add the FortiManager serial number from the FortiGate CLI, use below configurations:
config system central-management
set type fortimanager
set serial-number "<FortiManager_serial_number>"
set fmg "<FortiManager_IP>"
end
Compatibility tool between FortiGate and FortiManager: FortiOS Compatibility Tool.

