| Topology: 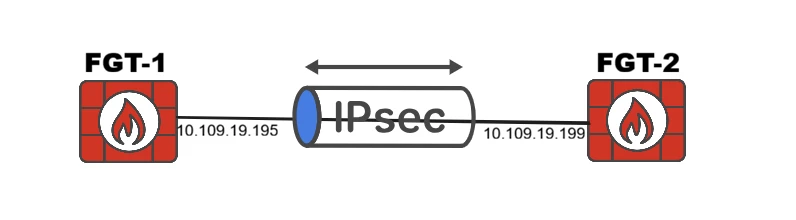
On FGT-1:
FGT-1 # diagnose vpn ike gateway list vd: root/0
name: IPSEC
version: 2
interface: port1 3
addr: 10.109.19.195:9591 -> 10.109.19.199:4442
tun_id: 10.109.19.199/::10.109.19.199
remote_location: 0.0.0.0
network-id: 0
transport: TCP <------------------- TCP protocol is used on FGT-1.
created: 12s ago
pending-queue: 0
PPK: no
IKE SA: created 1/1
IPsec SA: created 1/1 id/spi: 11 b956228fd5f53990/0000000000000000
direction: responder
status: connecting, state 3, started 12s ago
On FGT-2:
FGT-2 # diagnose vpn ike gateway list vd: root/0
name: IPSEC
version: 2
interface: port1 3
addr: 10.109.19.199:500 -> 10.109.19.195:500
tun_id: 10.109.19.195/::10.109.19.195
remote_location: 0.0.0.0
network-id: 0
transport: UDP <-----------------UDP protocol is used on FGT-2.
created: 2s ago
pending-queue: 0
PPK: no
IKE SA: created 1/1
IPsec SA: created 1/1 id/spi: 3 7c5f9b27372b5747/0000000000000000
direction: responder
status: connecting, state 3, started 2s ago Diagnostics: Enable IKE debug:
diagnose debug reset diagnose debug reset
diagnose debug application ike -1
diagnose debug console timestamp enable
diagnose debug enable To disable debug:
diagnose debug disable
Debug output :
ike V=root:0:1411c654163ab506/0000000000000000:81: SA proposal chosen, matched gateway IPSEC
ike V=root:0:IPSEC:IPSEC: created connection: 0x55aa85712940 3 10.109.19.195->10.109.19.199:500.
ike V=root:0:IPSEC: duplicate connection detected on insert, dropping this connection
ike V=root:0:IPSEC: reset TCP ports
ike V=root:0:1411c654163ab506/0000000000000000:81: failed to create a connection
ike V=root:could not send IKE msg (RETRANSMIT_SA_INIT): still waiting for tcp-transport(vd=0, vrf=0, intf=3:3, 10.109.19.195:1897->10.109.19.199:4442 sock=42 refcnt=1 ph1=0x55aa85708ba0)
This issue is occurring due to a mismatch in the protocol used for the IPsec tunnel on the firewall. To resolve it, change the transport port on FGT-1 to UDP:
config vpn ipsec phase1-interface
edit "IPSEC"
set transport udp next end
|