| A PKI user is configured on FortiGate with the following configuration:
config user peer
edit "minh"
set ca "CA_Cert_1"
set subject "cn=minh"
next
end
Running fnbamd and SSL VPN debug, the following error can be observed:
[394] peer_subject_cn_check-Cert subject 'CN = minh'
[352] __cert_subject_RDN_compare-Total matched RDNs in cert: 0
[410] peer_subject_cn_check-Subject checking failed.
[525] __check_add_peer-'minh' check ret:bad
[198] __get_default_ocsp_ctx-def_ocsp_ctx=(nil), no_ocsp_query=0, ocsp_enabled=0
[1051] __cert_verify_do_next-req_id=13181408841842
[99] __cert_chg_st- 'Validation' -> 'Done'
[1098] __cert_done-req_id=13181408841842
[1524] fnbamd_auth_session_done-Session done, id=13181408841842
[1144] __fnbamd_cert_auth_run-Exit, req_id=13181408841842
[1567] create_auth_cert_session-fnbamd_cert_auth_init returns 0, id=13181408841842
[1480] auth_cert_success-id=13181408841842
[1256] fnbamd_cert_auth_copy_cert_status-req_id=13181408841842
[884] fnbamd_cert_check_matched_groups-checking group with name 'PKI VPN'
[954] fnbamd_cert_check_matched_groups-not matched
Compared with the subject field from the client certificate, the one configured on FortiGate uses 'cn' instead of 'CN'. 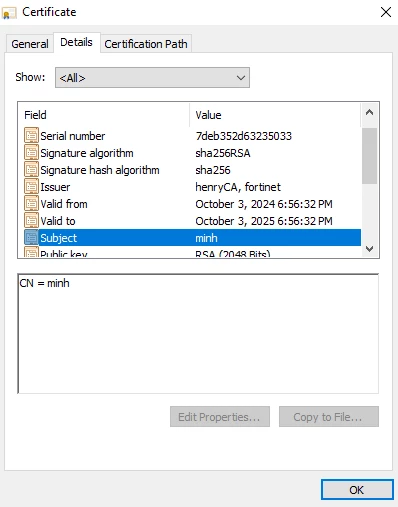
Changing the config on FortiGate to match the subject value from 'cn' to 'CN' would make the subject match and pass certificate check.
[394] peer_subject_cn_check-Cert subject 'CN = minh'
[322] __RDN_match-Checking 'CN' val 'minh' -- match.
[352] __cert_subject_RDN_compare-Total matched RDNs in cert: 1
[419] peer_subject_cn_check-Subject is good.
[525] __check_add_peer-'minh' check ret:good
[640] __peer_user_clear_unmatched-Clear all user(s) other than 'minh'
[661] __peer_user_clear_unmatched-
[198] __get_default_ocsp_ctx-def_ocsp_ctx=(nil), no_ocsp_query=0, ocsp_enabled=0
[778] fnbamd_cert_check_group_list-Peer users
[781] fnbamd_cert_check_group_list- 'minh' ('N/A','N/A','N/A')
[1051] __cert_verify_do_next-req_id=13181408841853
[99] __cert_chg_st- 'Validation' -> 'Done'
[1098] __cert_done-req_id=13181408841853
[1524] fnbamd_auth_session_done-Session done, id=13181408841853
[1144] __fnbamd_cert_auth_run-Exit, req_id=13181408841853
[1567] create_auth_cert_session-fnbamd_cert_auth_init returns 0, id=13181408841853
[1480] auth_cert_success-id=13181408841853
[1256] fnbamd_cert_auth_copy_cert_status-req_id=13181408841853
[1264] fnbamd_cert_auth_copy_cert_status-Matched peer user 'minh' | 




