Troubleshooting Tip: SLAs SD-WAN VPN health checks not working in a redundant HUB and Spoke Topology
| Description | This article describes a behavior where users deploy an SD-WAN VPN redundant HUB and Spoke topology, but the Health checks are not working, although the user is using the correct destination addresses. |
| Scope | SD-WAN VPN Redundant HUB and Spoke topology. |
| Solution | Users may deploy a topology with redundant VPN tunnels from Spokes to HUBs:
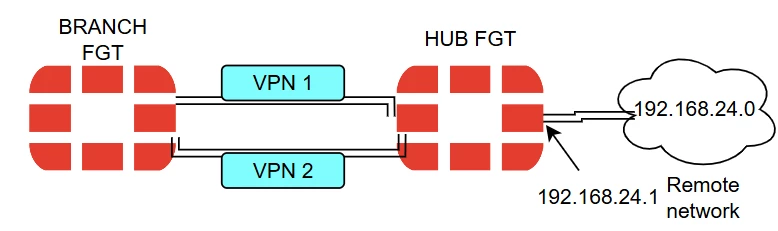
Both VPNs in the Spoke are using SD-WAN SLA Healthchecks, and the destination configured is the IP 192.168.24.1 on the HUB's side. However SLA of VPN1 is working, butthe SLA of VPN2 is not working.
From the HUB side, the HUB is answering the pings from SLA VPN2 using VPN1. This is not the default behavior, as HUB should answer through the same VPN interface the ping is coming
Solution: On the HUB side, validate if the feature asymmetric route feature is enabled and disable it: Technical Tip: How the FortiGate behaves when asymmetric routing is enabled
This will force FortiGate HUB to always answer the health check through the same VPN incoming interface. |