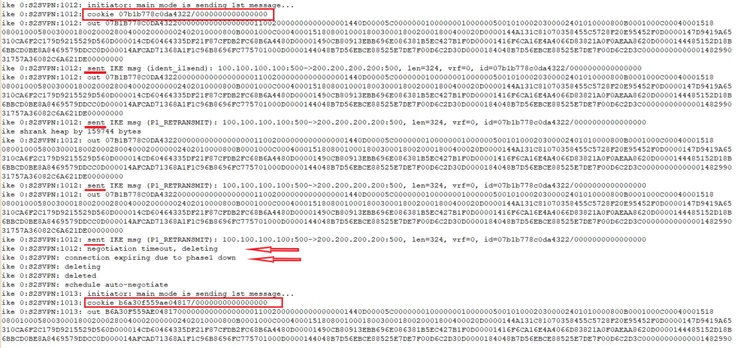
Troubleshooting Tip: Site-to-Site VPN failed to establish between FortiGate and ZYXEL with cookie xxxxxxxxxxxxxxxx/0000000000000000
| Description | This article describes how to fix an issue where Site-to-Site VPN between FortiGate and ZYXEL failed to establish and a cookie from FortiGate goes out to ZYXEL with a non-zero number/letter cookie value, but no cookie is seen from ZYXEL (for example, xxxxxxxxxxxxxxxx/0000000000000000). |
| Scope | FortiGate. |
| Solution | An IKE debug will show something similar to the below screenshot. Notice that in this case, FortiGate is the initiator and sent its cookie to ZYXEL, but did not receive any response.
07b1b778c0da4322/0000000000000000
After some time, the negotiation times out (see the above screenshot for details). FortiGate deletes the cookie and sends a new one with no response, just like before, and the cycle repeats. If this situation occurs, the issue is caused by having a password for the VPN configuration that is too complex: in this case, it is 20 characters long. Reduce the password length until the tunnel establishes (it is recommended to use 10 characters).
Note: Complex passwords (with different combinations of special symbols, upper case, lower case, numbers) of 20 characters or more in length are not an issue for FortiGate to FortiGate connections. This issue only occurs in connections between FortiGate and ZYXEL. |