Troubleshooting Tip: Site-to-Site IPsec VPN phase 1 not forming despite same SA on both local and remote site
| Description | This article describes resolving Site-to-Site IPsec VPN phase 1 not forming despite the same SA. |
| Scope | FortiGate. |
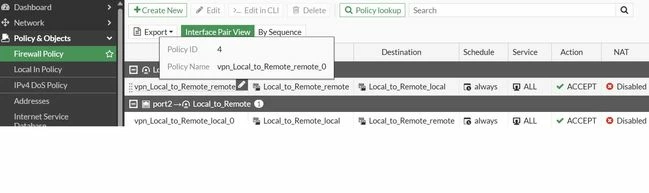
| Solution | To troubleshoot this, make sure firewall policy/policies is/are configured to allow bi-directional traffic from local to remote destinations is configured. It is quite common to omit firewall policy when configuring a Site-to-Site IPsec VPN without using the wizard.
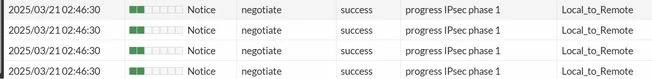
Before the firewall policy is configured, phase 1 cannot be formed.
After the firewall policy is configured, phase 1 is formed.
Result: Phase 1 is formed.
diagnose vpn ike log-filter dst-addr4 <Remote_GW_IP>
To disable:
diagnose debug disable
If both sides are FortiGate Firewalls the debugging needs to be run on both of the devices to get a better overview of the negotiation. Related article: |