ianderson
Staff
Staff
December 31, 2025

Troubleshooting Tip: Resolve 'could not connect to the FortiManager to retrieve its serial number' on FortiGate-VM

  • December 31, 2025
  • 1 reply
  • 2276 views
Description This article describes a change in behavior on FortiGate-VM registering to FortiManager.
Scope FortiGate VM 7.6.x & FortiManager 7.4.7+.
Solution

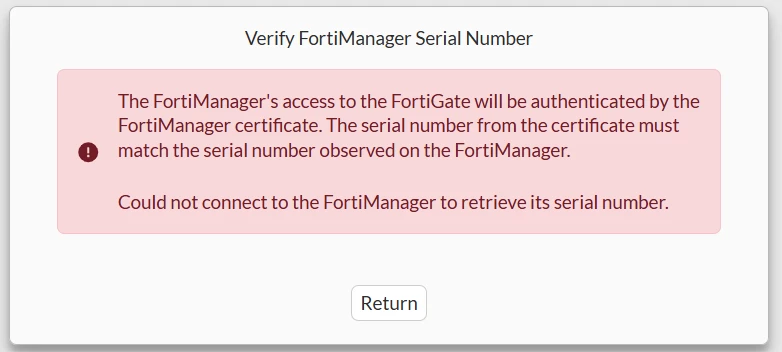
When trying to set a FortiManager in Central Management on a FortiGate-VM, the following error may be observed:


The FortiManager's access to the FortiGate will be authenticated by the FortiManager certificate. The serial number from the certificate must match the serial number observed on the FortiManager.  Could not connect to the FortiManager to retrieve its serial number


fmg-serial.png


This is likely due to a change introduced in FortiManager 7.4.7, which restricts the registration of FortiGate VM. 


See Adding VM devices to FortiManager - FortiManager 7.4.7 release notes for instructions on how to resolve this.

1 reply

New Member
June 15, 2026

On Fortimanager:

FMG-VM64-cfcb0e68 # 2026-06-14 18:20:30 proxy_session.c,__session_frontend_accept_core,859: 192.168.0.30:16632 -> 192.168.0.10:541.
2026-06-14 18:20:30 __use_cert,763: start idx = 0
2026-06-14 18:20:30 use certificate issuer  = /C=US/ST=California/L=Sunnyvale/O=Fortinet/OU=Certificate Authority/CN=support/emailAddress=support@fortinet.com
2026-06-14 18:20:30                 subject = /C=US/ST=California/L=Sunnyvale/O=Fortinet/OU=FortiManager/CN=FMG-VMTM26006853/emailAddress=support@fortinet.com
2026-06-14 18:20:30 proxy_session.c,__proxy_session_cleanup, 124:cnt=0, session=0x557fa7f0da8c.
2026-06-14 18:20:30 __info_callback,1147, pid=30201: role=svr,state=0, TLSv1.3 before SSL initialization
2026-06-14 18:20:30 Got client SNI information : sni=(null)
2026-06-14 18:20:30 __info_callback,1147, pid=30201: role=svr,state=22, TLSv1.3 SSLv3/TLS read client hello
2026-06-14 18:20:30 __info_callback,1147, pid=30201: role=svr,state=24, TLSv1.3 SSLv3/TLS write server hello
2026-06-14 18:20:30 __info_callback,1147, pid=30201: role=svr,state=39, TLSv1.3 SSLv3/TLS write change cipher spec
2026-06-14 18:20:30 __info_callback,1147, pid=30201: role=svr,state=50, TLSv1.3 TLSv1.3 early data
2026-06-14 18:20:30 Got client SNI information : sni=(null)
2026-06-14 18:20:30 __info_callback,1147, pid=30201: role=svr,state=22, TLSv1.3 SSLv3/TLS read client hello
2026-06-14 18:20:30 __info_callback,1147, pid=30201: role=svr,state=24, TLSv1.3 SSLv3/TLS write server hello
2026-06-14 18:20:30 __info_callback,1147, pid=30201: role=svr,state=41, TLSv1.3 TLSv1.3 write encrypted extensions
2026-06-14 18:20:30       CA to broadcast: /C=US/ST=California/L=Sunnyvale/O=Fortinet/OU=Certificate Authority/CN=fortinet-subca2003
2026-06-14 18:20:30       CA to broadcast: /C=US/ST=California/L=Sunnyvale/O=Fortinet/OU=Certificate Authority/CN=support/emailAddress=support@fortinet.com
2026-06-14 18:20:30       CA to broadcast: /C=US/ST=California/L=Sunnyvale/O=Fortinet/OU=Certificate Authority/CN=fortinet-ca2/emailAddress=support@fortinet.com
2026-06-14 18:20:30       CA to broadcast: /C=US/ST=California/L=Sunnyvale/O=Fortinet/OU=Certificate Authority/CN=fortinet-subca2001/emailAddress=support@fortinet.com
2026-06-14 18:20:30 Svr broadcast 4 CA subject names to peer
2026-06-14 18:20:30 __info_callback,1147, pid=30201: role=svr,state=28, TLSv1.3 SSLv3/TLS write certificate request
2026-06-14 18:20:30 The CA of No.1 local cert:
  /C=US/ST=California/L=Sunnyvale/O=Fortinet/OU=Certificate Authority/CN=support/emailAddress=support@fortinet.com
2026-06-14 18:20:30   Remote CA: /C=US/ST=California/L=Sunnyvale/O=Fortinet/OU=Certificate Authority/CN=fortinet-ca2/emailAddress=support@fortinet.com
2026-06-14 18:20:30 The CA of No.2 local cert:
  /C=US/ST=California/L=Sunnyvale/O=Fortinet/OU=Certificate Authority/CN=fortinet-subca2001/emailAddress=support@fortinet.com
2026-06-14 18:20:30   Remote CA: /C=US/ST=California/L=Sunnyvale/O=Fortinet/OU=Certificate Authority/CN=fortinet-ca2/emailAddress=support@fortinet.com
2026-06-14 18:20:30     They share the same root CA, but with different immediate CAs
2026-06-14 18:20:30 Find cert idx=1, peer_ca = 1
2026-06-14 18:20:30 __use_cert,763: start idx = 1
2026-06-14 18:20:30 use certificate issuer  = /C=US/ST=California/L=Sunnyvale/O=Fortinet/OU=Certificate Authority/CN=fortinet-subca2001/emailAddress=support@fortinet.com
2026-06-14 18:20:30                 subject = /C=US/ST=California/L=Sunnyvale/O=Fortinet/OU=FortiManager/CN=FMG-VMTM26006853/emailAddress=support@fortinet.com
2026-06-14 18:20:30 Use cert idx=1 by peer_ca = 1
2026-06-14 18:20:30 __info_callback,1147, pid=30201: role=svr,state=25, TLSv1.3 SSLv3/TLS write certificate
2026-06-14 18:20:30 __info_callback,1147, pid=30201: role=svr,state=44, TLSv1.3 TLSv1.3 write server certificate verify
2026-06-14 18:20:30 __info_callback,1147, pid=30201: role=svr,state=40, TLSv1.3 SSLv3/TLS write finished
2026-06-14 18:20:30 __info_callback,1147, pid=30201: role=svr,state=50, TLSv1.3 TLSv1.3 early data
2026-06-14 18:20:30 TLSv1.3 write fatal alert: unknown
2026-06-14 18:20:30 fw_proto_ssl.c,1180: TLSv1.3 error
2026-06-14 18:20:30 fw_proto_ssl.c,__get_error,1760, err=167772359, error:0A0000C7:SSL routines::peer did not return a certificate.
2026-06-14 18:20:30 fw_proto_ssl.c,__get_error,1774, ret=-4, error=1, errno=5,Input/output error.
2026-06-14 18:20:30 proxy_session.c,__negotiate,235: frontend accept error.
2026-06-14 18:20:30 proxy_session.c,__proxy_session_cleanup, 124:cnt=0, session=0x557fa7eeaf1c.
2026-06-14 18:20:37 Chkperm Response [gui flatui_proxy:13718:1]:
2026-06-14 18:20:37 { "id": 1, "result": [{ "status": { "code": 0, "message": "OK"}, "url": "start\/probe\/session"}], "session": 6444}

2026-06-14 18:20:37 Request:
2026-06-14 18:20:37 { "chkperm result": [{ "status": { "code": 0, "message": "OK"}, "url": "start\/probe\/session"}], "client": "gui flatui_proxy:13718", "id": 1, "method": "exec", "params": [{ "data": { "detect_only": 1, "force_probe": 0, "ip": "192.168.0.30", "passwd": "******", "usr": "admin"}, "target start": 4, "url": "start\/probe\/session"}], "root": "fgfm", "session": 6444}

2026-06-14 18:20:37 FGFMs: 2026-06-14 18:20:37 Entering __probe_device_core 1355.
2026-06-14 18:20:37 FGFMs: 2026-06-14 18:20:37 __probe_device_core 1367: user=admin, passwd=******, force_probe=0, detect_only=1.
2026-06-14 18:20:37 FGFMs(probing...): 2026-06-14 18:20:37 Create session 0x557fa7ee46ec.
2026-06-14 18:20:37 proxy_session.c,__session_backend_accept,932: incomoing to .
2026-06-14 18:20:37 proxy_session.c,__proxy_session_cleanup, 124:cnt=0, session=0x557fa7eeaf1c.
2026-06-14 18:20:37 FGFMs(probing...): 2026-06-14 18:20:37 Connect to 192.168.0.30.
2026-06-14 18:20:37 __on_backend_accept,384:
2026-06-14 18:20:37 addr:{0.0.0.0:0->2026-06-14 18:20:37 192.168.0.30:541},2026-06-14 18:20:37 }2026-06-14 18:20:37 
2026-06-14 18:20:37 proxy_session.c,__on_backend_accept,390: 0.0.0.0:0 -> 192.168.0.30:541.
2026-06-14 18:20:37 proxy_session.c,__backend_ssl_negotiate_enter,416: 192.168.0.10:22390 -> 192.168.0.30:541.
2026-06-14 18:20:37 __use_cert,763: start idx = 0
2026-06-14 18:20:37 use certificate issuer  = /C=US/ST=California/L=Sunnyvale/O=Fortinet/OU=Certificate Authority/CN=support/emailAddress=support@fortinet.com
2026-06-14 18:20:37                 subject = /C=US/ST=California/L=Sunnyvale/O=Fortinet/OU=FortiManager/CN=FMG-VMTM26006853/emailAddress=support@fortinet.com
2026-06-14 18:20:37 __info_callback,1147, pid=30200: role=svr,state=0, TLSv1.3 before SSL initialization
2026-06-14 18:20:37 Got client SNI information : sni=(null)
2026-06-14 18:20:37 __info_callback,1147, pid=30200: role=svr,state=22, TLSv1.3 SSLv3/TLS read client hello
2026-06-14 18:20:37 __info_callback,1147, pid=30200: role=svr,state=24, TLSv1.3 SSLv3/TLS write server hello
2026-06-14 18:20:37 __info_callback,1147, pid=30200: role=svr,state=39, TLSv1.3 SSLv3/TLS write change cipher spec
2026-06-14 18:20:37 __info_callback,1147, pid=30200: role=svr,state=50, TLSv1.3 TLSv1.3 early data
2026-06-14 18:20:37 Got client SNI information : sni=(null)
2026-06-14 18:20:37 __info_callback,1147, pid=30200: role=svr,state=22, TLSv1.3 SSLv3/TLS read client hello
2026-06-14 18:20:37 __info_callback,1147, pid=30200: role=svr,state=24, TLSv1.3 SSLv3/TLS write server hello
2026-06-14 18:20:37 __info_callback,1147, pid=30200: role=svr,state=41, TLSv1.3 TLSv1.3 write encrypted extensions
2026-06-14 18:20:37       CA to broadcast: /C=US/ST=California/L=Sunnyvale/O=Fortinet/OU=Certificate Authority/CN=fortinet-subca2003
2026-06-14 18:20:37       CA to broadcast: /C=US/ST=California/L=Sunnyvale/O=Fortinet/OU=Certificate Authority/CN=support/emailAddress=support@fortinet.com
2026-06-14 18:20:37       CA to broadcast: /C=US/ST=California/L=Sunnyvale/O=Fortinet/OU=Certificate Authority/CN=fortinet-ca2/emailAddress=support@fortinet.com
2026-06-14 18:20:37       CA to broadcast: /C=US/ST=California/L=Sunnyvale/O=Fortinet/OU=Certificate Authority/CN=fortinet-subca2001/emailAddress=support@fortinet.com
2026-06-14 18:20:37 Svr broadcast 4 CA subject names to peer
2026-06-14 18:20:37 __info_callback,1147, pid=30200: role=svr,state=28, TLSv1.3 SSLv3/TLS write certificate request
2026-06-14 18:20:37 The CA of No.1 local cert:
  /C=US/ST=California/L=Sunnyvale/O=Fortinet/OU=Certificate Authority/CN=support/emailAddress=support@fortinet.com
2026-06-14 18:20:37   Remote CA: /C=US/ST=California/L=Sunnyvale/O=Fortinet/OU=Certificate Authority/CN=fortinet-ca2/emailAddress=support@fortinet.com
2026-06-14 18:20:37 The CA of No.2 local cert:
  /C=US/ST=California/L=Sunnyvale/O=Fortinet/OU=Certificate Authority/CN=fortinet-subca2001/emailAddress=support@fortinet.com
2026-06-14 18:20:37   Remote CA: /C=US/ST=California/L=Sunnyvale/O=Fortinet/OU=Certificate Authority/CN=fortinet-ca2/emailAddress=support@fortinet.com
2026-06-14 18:20:37     They share the same root CA, but with different immediate CAs
2026-06-14 18:20:37 Find cert idx=1, peer_ca = 1
2026-06-14 18:20:37 __use_cert,763: start idx = 1
2026-06-14 18:20:37 use certificate issuer  = /C=US/ST=California/L=Sunnyvale/O=Fortinet/OU=Certificate Authority/CN=fortinet-subca2001/emailAddress=support@fortinet.com
2026-06-14 18:20:37                 subject = /C=US/ST=California/L=Sunnyvale/O=Fortinet/OU=FortiManager/CN=FMG-VMTM26006853/emailAddress=support@fortinet.com
2026-06-14 18:20:37 Use cert idx=1 by peer_ca = 1
2026-06-14 18:20:37 __info_callback,1147, pid=30200: role=svr,state=25, TLSv1.3 SSLv3/TLS write certificate


On Fortigate: 


2026-06-14 18:20:29 FGFMs: SSL Alert read: fatal unknown
2026-06-14 18:20:30 FGFMs: Cleanup session 0x5594f8389200, 192.168.0.10.
2026-06-14 18:20:30 FGFMs: Destroy session 0x5594f8389200, 192.168.0.10.
2026-06-14 18:20:36 FGFMs: Incoming 192.168.0.10 local 192.168.0.30.
2026-06-14 18:20:36 FGFMs: Create session 0x5594f8389200.
2026-06-14 18:20:36 FGFMs: checking existing sessions...
2026-06-14 18:20:36 FGFMs: Load Cipher [DES:!3DES:!ECDH:!DHE:!AES:!CAMELLIA:!SEED:!RC4:!PSK:!IDEA:!ARIA:@STRENGTH:@SECLEVEL=0]
2026-06-14 18:20:36 FGFMs: Load TLS 1.3 Cipher [TLS_AES_256_GCM_SHA384:TLS_CHACHA20_POLY1305_SHA256:TLS_AES_128_GCM_SHA256]
2026-06-14 18:20:36 FGFMs: before SSL initialization
2026-06-14 18:20:36 FGFMs:       CA to broadcast: subject fortinet-ca2, issuer fortinet-ca2
2026-06-14 18:20:36 FGFMs: Broadcast 1 CA subject names to FMG
2026-06-14 18:20:36 FGFMs: SSLv3/TLS write client hello
2026-06-14 18:20:36 FGFMs: SSLv3/TLS read server hello
2026-06-14 18:20:36 FGFMs: SSLv3/TLS write change cipher spec
2026-06-14 18:20:36 FGFMs: SSLv3/TLS write client hello
2026-06-14 18:20:36 FGFMs: SSLv3/TLS read server hello
2026-06-14 18:20:36 FGFMs: TLSv1.3 read encrypted extensions
2026-06-14 18:20:36 FGFMs: SSLv3/TLS read server certificate request
2026-06-14 18:20:36 FGFMs: Verified CA certificate 2: (subject: fortinet-ca2, issuer: fortinet-ca2)
2026-06-14 18:20:36 FGFMs: Verified CA certificate 1: (subject: fortinet-subca2001, issuer: fortinet-ca2)
2026-06-14 18:20:36 FGFMs: Verified peer certificate 0: (subject: FMG-VMTM26006853, issuer: fortinet-subca2001)
2026-06-14 18:20:36 FGFMs: The peer certificate FMG-VMTM26006853 is unknown!
2026-06-14 18:20:36 FGFMs: SSLv3/TLS read server certificate
2026-06-14 18:20:36 FGFMs: TLSv1.3 read server certificate verify
2026-06-14 18:20:36 FGFMs: SSLv3/TLS read finished
2026-06-14 18:20:36 FGFMs: SSLv3/TLS write client certificate
2026-06-14 18:20:36 FGFMs: SSLv3/TLS write finished
2026-06-14 18:20:36 FGFMs: SSL negotiation finished successfully
2026-06-14 18:20:36 FGFMs: client:send
get auth
fg_ip=192.168.0.30
mgmtip=192.168.0.30
mgmtport=443


2026-06-14 18:20:36 FGFMs: SSL Alert read: fatal unknown
2026-06-14 18:20:37 FGFMs: Cleanup session 0x5594f8389200, 192.168.0.10.
2026-06-14 18:20:37 FGFMs: Destroy session 0x5594f8389200, 192.168.0.10.
2026-06-14 18:20:45 FGFMs: Create session 0x5594f8389200.
2026-06-14 18:20:45 FGFMs: setting session 0x5594f8389200 exclusive=0
2026-06-14 18:20:45 FGFMs: Connect to 192.168.0.10:541, local 192.168.0.30:16634.
2026-06-14 18:20:45 FGFMs: Load Cipher [DES:!3DES:!ECDH:!DHE:!AES:!CAMELLIA:!SEED:!RC4:!PSK:!IDEA:!ARIA:@STRENGTH:@SECLEVEL=0]
2026-06-14 18:20:45 FGFMs: Load TLS 1.3 Cipher [TLS_AES_256_GCM_SHA384:TLS_CHACHA20_POLY1305_SHA256:TLS_AES_128_GCM_SHA256]
2026-06-14 18:20:45 FGFMs: Set self_initiated = 1
2026-06-14 18:20:45 FGFMs: before SSL initialization
2026-06-14 18:20:45 FGFMs:       CA to broadcast: subject fortinet-ca2, issuer fortinet-ca2
2026-06-14 18:20:45 FGFMs: Broadcast 1 CA subject names to FMG
2026-06-14 18:20:45 FGFMs: SSLv3/TLS write client hello
2026-06-14 18:20:45 FGFMs: SSLv3/TLS read server hello
2026-06-14 18:20:45 FGFMs: SSLv3/TLS write change cipher spec
2026-06-14 18:20:45 FGFMs: SSLv3/TLS write client hello
2026-06-14 18:20:46 FGFMs: SSLv3/TLS write client hello
2026-06-14 18:20:46 FGFMs: SSLv3/TLS read server hello
2026-06-14 18:20:46 FGFMs: TLSv1.3 read encrypted extensions
2026-06-14 18:20:46 FGFMs: SSLv3/TLS read server certificate request
2026-06-14 18:20:46 FGFMs: Verified CA certificate 2: (subject: fortinet-ca2, issuer: fortinet-ca2)
2026-06-14 18:20:46 FGFMs: Verified CA certificate 1: (subject: fortinet-subca2001, issuer: fortinet-ca2)
2026-06-14 18:20:46 FGFMs: Verified peer certificate 0: (subject: FMG-VMTM26006853, issuer: fortinet-subca2001)
2026-06-14 18:20:46 FGFMs: SSLv3/TLS read server certificate
2026-06-14 18:20:46 FGFMs: TLSv1.3 read server certificate verify
2026-06-14 18:20:46 FGFMs: SSLv3/TLS read finished
2026-06-14 18:20:46 FGFMs: SSLv3/TLS write client certificate
2026-06-14 18:20:46 FGFMs: SSLv3/TLS write finished
2026-06-14 18:20:46 FGFMs: SSL negotiation finished successfully
2026-06-14 18:20:46 FGFMs: client:send
get auth
serialno=FGVMEVIY4IPWHN15
mgmtid=00000000-0000-0000-0000-000000000000
platform=FortiGate-VM64
fos_ver=800
minor=0
patch=0
build=167
branch=167
maxvdom=2
fg_ip=192.168.0.30
hostname=FGVMEVIY4IPWHN15
harddisk=no
biover=04000002
mgmt_mode=normal
enc_flags=0
mgmtip=192.168.0.30
mgmtport=443


2026-06-14 18:20:46 FGFMs: SSL Alert read: fatal unknown
2026-06-14 18:20:46 FGFMs: Cleanup session 0x5594f8389200, 192.168.0.10.
2026-06-14 18:20:46 FGFMs: Destroy session 0x5594f8389200, 192.168.0.10.
2026-06-14 18:21:01 FGFMs: Create session 0x5594f8389200.
2026-06-14 18:21:01 FGFMs: setting session 0x5594f8389200 exclusive=0
2026-06-14 18:21:01 FGFMs: Connect to 192.168.0.10:541, local 192.168.0.30:16636.
2026-06-14 18:21:01 FGFMs: Load Cipher [DES:!3DES:!ECDH:!DHE:!AES:!CAMELLIA:!SEED:!RC4:!PSK:!IDEA:!ARIA:@STRENGTH:@SECLEVEL=0]
2026-06-14 18:21:01 FGFMs: Load TLS 1.3 Cipher [TLS_AES_256_GCM_SHA384:TLS_CHACHA20_POLY1305_SHA256:TLS_AES_128_GCM_SHA256]
2026-06-14 18:21:01 FGFMs: Set self_initiated = 1
2026-06-14 18:21:01 FGFMs: before SSL initialization
2026-06-14 18:21:01 FGFMs:       CA to broadcast: subject fortinet-ca2, issuer fortinet-ca2
2026-06-14 18:21:01 FGFMs: Broadcast 1 CA subject names to FMG
2026-06-14 18:21:01 FGFMs: SSLv3/TLS write client hello
2026-06-14 18:21:01 FGFMs: SSLv3/TLS read server hello
2026-06-14 18:21:01 FGFMs: SSLv3/TLS write change cipher spec
2026-06-14 18:21:01 FGFMs: SSLv3/TLS write client hello
2026-06-14 18:21:01 FGFMs: SSLv3/TLS read server hello
2026-06-14 18:21:01 FGFMs: TLSv1.3 read encrypted extensions
2026-06-14 18:21:01 FGFMs: SSLv3/TLS read server certificate request
2026-06-14 18:21:01 FGFMs: Verified CA certificate 2: (subject: fortinet-ca2, issuer: fortinet-ca2)
2026-06-14 18:21:01 FGFMs: Verified CA certificate 1: (subject: fortinet-subca2001, issuer: fortinet-ca2)
2026-06-14 18:21:01 FGFMs: Verified peer certificate 0: (subject: FMG-VMTM26006853, issuer: fortinet-subca2001)
2026-06-14 18:21:01 FGFMs: SSLv3/TLS read server certificate
2026-06-14 18:21:01 FGFMs: TLSv1.3 read server certificate verify
2026-06-14 18:21:01 FGFMs: SSLv3/TLS read finished
2026-06-14 18:21:01 FGFMs: SSLv3/TLS write client certificate
2026-06-14 18:21:01 FGFMs: SSLv3/TLS write finished
2026-06-14 18:21:01 FGFMs: SSL negotiation finished successfully
2026-06-14 18:21:01 FGFMs: client:send
get auth
serialno=FGVMEVIY4IPWHN15
mgmtid=00000000-0000-0000-0000-000000000000
platform=FortiGate-VM64
fos_ver=800
minor=0
patch=0
build=167
branch=167
maxvdom=2
fg_ip=192.168.0.30
hostname=FGVMEVIY4IPWHN15
harddisk=no
biover=04000002
mgmt_mode=normal
enc_flags=0
mgmtip=192.168.0.30
mgmtport=443


2026-06-14 18:21:01 FGFMs: SSL Alert read: fatal unknown
2026-06-14 18:21:02 FGFMs: Cleanup session 0x5594f8389200, 192.168.0.10.
2026-06-14 18:21:02 FGFMs: Destroy session 0x5594f8389200, 192.168.0.10.
2026-06-14 18:21:17 FGFMs: Create session 0x5594f8389200.
2026-06-14 18:21:17 FGFMs: setting session 0x5594f8389200 exclusive=0
2026-06-14 18:21:17 FGFMs: Connect to 192.168.0.10:541, local 192.168.0.30:16638.
2026-06-14 18:21:17 FGFMs: Load Cipher [DES:!3DES:!ECDH:!DHE:!AES:!CAMELLIA:!SEED:!RC4:!PSK:!IDEA:!ARIA:@STRENGTH:@SECLEVEL=0]
2026-06-14 18:21:17 FGFMs: Load TLS 1.3 Cipher [TLS_AES_256_GCM_SHA384:TLS_CHACHA20_POLY1305_SHA256:TLS_AES_128_GCM_SHA256]
2026-06-14 18:21:17 FGFMs: Set self_initiated = 1
2026-06-14 18:21:17 FGFMs: before SSL initialization
2026-06-14 18:21:17 FGFMs:       CA to broadcast: subject fortinet-ca2, issuer fortinet-ca2
2026-06-14 18:21:17 FGFMs: Broadcast 1 CA subject names to FMG
2026-06-14 18:21:17 FGFMs: SSLv3/TLS write client hello
2026-06-14 18:21:17 FGFMs: SSLv3/TLS read server hello
2026-06-14 18:21:17 FGFMs: SSLv3/TLS write change cipher spec
2026-06-14 18:21:17 FGFMs: SSLv3/TLS write client hello
2026-06-14 18:21:17 FGFMs: SSLv3/TLS read server hello
2026-06-14 18:21:17 FGFMs: TLSv1.3 read encrypted extensions
2026-06-14 18:21:17 FGFMs: SSLv3/TLS read server certificate request
2026-06-14 18:21:17 FGFMs: Verified CA certificate 2: (subject: fortinet-ca2, issuer: fortinet-ca2)
2026-06-14 18:21:17 FGFMs: Verified CA certificate 1: (subject: fortinet-subca2001, issuer: fortinet-ca2)
2026-06-14 18:21:17 FGFMs: Verified peer certificate 0: (subject: FMG-VMTM26006853, issuer: fortinet-subca2001)
2026-06-14 18:21:17 FGFMs: SSLv3/TLS read server certificate
2026-06-14 18:21:17 FGFMs: TLSv1.3 read server certificate verify
2026-06-14 18:21:17 FGFMs: SSLv3/TLS read finished
2026-06-14 18:21:17 FGFMs: SSLv3/TLS write client certificate
2026-06-14 18:21:17 FGFMs: SSLv3/TLS write finished
2026-06-14 18:21:17 FGFMs: SSL negotiation finished successfully
2026-06-14 18:21:17 FGFMs: client:send
get auth
serialno=FGVMEVIY4IPWHN15
mgmtid=00000000-0000-0000-0000-000000000000
platform=FortiGate-VM64
fos_ver=800
minor=0
patch=0
build=167
branch=167
maxvdom=2
fg_ip=192.168.0.30
hostname=FGVMEVIY4IPWHN15
harddisk=no
biover=04000002
mgmt_mode=normal
enc_flags=0
mgmtip=192.168.0.30
mgmtport=443


2026-06-14 18:21:17 FGFMs: SSL Alert read: fatal unknown
2026-06-14 18:21:18 FGFMs: Cleanup session 0x5594f8389200, 192.168.0.10.
2026-06-14 18:21:18 FGFMs: Destroy session 0x5594f8389200, 192.168.0.10.
2026-06-14 18:21:33 FGFMs: Create session 0x5594f8389200.
2026-06-14 18:21:33 FGFMs: setting session 0x5594f8389200 exclusive=0
2026-06-14 18:21:33 FGFMs: Connect to 192.168.0.10:541, local 192.168.0.30:16644.
2026-06-14 18:21:33 FGFMs: Load Cipher [DES:!3DES:!ECDH:!DHE:!AES:!CAMELLIA:!SEED:!RC4:!PSK:!IDEA:!ARIA:@STRENGTH:@SECLEVEL=0]
2026-06-14 18:21:33 FGFMs: Load TLS 1.3 Cipher [TLS_AES_256_GCM_SHA384:TLS_CHACHA20_POLY1305_SHA256:TLS_AES_128_GCM_SHA256]
2026-06-14 18:21:33 FGFMs: Set self_initiated = 1
2026-06-14 18:21:33 FGFMs: before SSL initialization
2026-06-14 18:21:33 FGFMs:       CA to broadcast: subject fortinet-ca2, issuer fortinet-ca2
2026-06-14 18:21:33 FGFMs: Broadcast 1 CA subject names to FMG
2026-06-14 18:21:33 FGFMs: SSLv3/TLS write client hello
2026-06-14 18:21:34 FGFMs: SSLv3/TLS write client hello
2026-06-14 18:21:34 FGFMs: SSLv3/TLS read server hello
2026-06-14 18:21:34 FGFMs: SSLv3/TLS write change cipher spec
2026-06-14 18:21:34 FGFMs: SSLv3/TLS write client hello
2026-06-14 18:21:34 FGFMs: SSLv3/TLS read server hello
2026-06-14 18:21:34 FGFMs: TLSv1.3 read encrypted extensions
2026-06-14 18:21:34 FGFMs: SSLv3/TLS read server certificate request
2026-06-14 18:21:34 FGFMs: Verified CA certificate 2: (subject: fortinet-ca2, issuer: fortinet-ca2)
2026-06-14 18:21:34 FGFMs: Verified CA certificate 1: (subject: fortinet-subca2001, issuer: fortinet-ca2)
2026-06-14 18:21:34 FGFMs: Verified peer certificate 0: (subject: FMG-VMTM26006853, issuer: fortinet-subca2001)
2026-06-14 18:21:34 FGFMs: SSLv3/TLS read server certificate
2026-06-14 18:21:34 FGFMs: TLSv1.3 read server certificate verify
2026-06-14 18:21:34 FGFMs: SSLv3/TLS read finished
2026-06-14 18:21:34 FGFMs: SSLv3/TLS write client certificate
2026-06-14 18:21:34 FGFMs: SSLv3/TLS write finished
2026-06-14 18:21:34 FGFMs: SSL negotiation finished successfully
2026-06-14 18:21:34 FGFMs: client:send
get auth
serialno=FGVMEVIY4IPWHN15
mgmtid=00000000-0000-0000-0000-000000000000
platform=FortiGate-VM64
fos_ver=800
minor=0
patch=0
build=167
branch=167
maxvdom=2
fg_ip=192.168.0.30
hostname=FGVMEVIY4IPWHN15
harddisk=no
biover=04000002
mgmt_mode=normal
enc_flags=0
mgmtip=192.168.0.30
mgmtport=443


2026-06-14 18:21:34 FGFMs: SSL Alert read: fatal unknown
2026-06-14 18:21:35 FGFMs: Cleanup session 0x5594f8389200, 192.168.0.10.
2026-06-14 18:21:35 FGFMs: Destroy session 0x5594f8389200, 192.168.0.10.
2026-06-14 18:21:50 FGFMs: Create session 0x5594f8389200.
2026-06-14 18:21:50 FGFMs: setting session 0x5594f8389200 exclusive=0
2026-06-14 18:21:50 FGFMs: Connect to 192.168.0.10:541, local 192.168.0.30:16646.
2026-06-14 18:21:50 FGFMs: Load Cipher [DES:!3DES:!ECDH:!DHE:!AES:!CAMELLIA:!SEED:!RC4:!PSK:!IDEA:!ARIA:@STRENGTH:@SECLEVEL=0]
2026-06-14 18:21:50 FGFMs: Load TLS 1.3 Cipher [TLS_AES_256_GCM_SHA384:TLS_CHACHA20_POLY1305_SHA256:TLS_AES_128_GCM_SHA256]
2026-06-14 18:21:50 FGFMs: Set self_initiated = 1
2026-06-14 18:21:50 FGFMs: before SSL initialization
2026-06-14 18:21:50 FGFMs:       CA to broadcast: subject fortinet-ca2, issuer fortinet-ca2
2026-06-14 18:21:50 FGFMs: Broadcast 1 CA subject names to FMG
2026-06-14 18:21:50 FGFMs: SSLv3/TLS write client hello
2026-06-14 18:21:50 FGFMs: SSLv3/TLS read server hello
2026-06-14 18:21:50 FGFMs: SSLv3/TLS write change cipher spec
2026-06-14 18:21:50 FGFMs: SSLv3/TLS write client hello
2026-06-14 18:21:50 FGFMs: SSLv3/TLS read server hello
2026-06-14 18:21:50 FGFMs: TLSv1.3 read encrypted extensions
2026-06-14 18:21:50 FGFMs: SSLv3/TLS read server certificate request
2026-06-14 18:21:50 FGFMs: Verified CA certificate 2: (subject: fortinet-ca2, issuer: fortinet-ca2)
2026-06-14 18:21:50 FGFMs: Verified CA certificate 1: (subject: fortinet-subca2001, issuer: fortinet-ca2)
2026-06-14 18:21:50 FGFMs: Verified peer certificate 0: (subject: FMG-VMTM26006853, issuer: fortinet-subca2001)
2026-06-14 18:21:50 FGFMs: SSLv3/TLS read server certificate
2026-06-14 18:21:50 FGFMs: TLSv1.3 read server certificate verify
2026-06-14 18:21:50 FGFMs: SSLv3/TLS read finished
2026-06-14 18:21:50 FGFMs: SSLv3/TLS write client certificate
2026-06-14 18:21:50 FGFMs: SSLv3/TLS write finished
2026-06-14 18:21:50 FGFMs: SSL negotiation finished successfully
2026-06-14 18:21:50 FGFMs: client:send
get auth
serialno=FGVMEVIY4IPWHN15
mgmtid=00000000-0000-0000-0000-000000000000
platform=FortiGate-VM64
fos_ver=800
minor=0
patch=0
build=167
branch=167
maxvdom=2
fg_ip=192.168.0.30
hostname=FGVMEVIY4IPWHN15
harddisk=no
biover=04000002
mgmt_mode=normal
enc_flags=0
mgmtip=192.168.0.30
mgmtport=443


2026-06-14 18:21:50 FGFMs: SSL Alert read: fatal unknown
2026-06-14 18:21:51 FGFMs: Cleanup session 0x5594f8389200, 192.168.0.10.
2026-06-14 18:21:51 FGFMs: Destroy session 0x5594f8389200, 192.168.0.10.
2026-06-14 18:22:06 FGFMs: Create session 0x5594f8389200.
2026-06-14 18:22:06 FGFMs: setting session 0x5594f8389200 exclusive=0
2026-06-14 18:22:06 FGFMs: Connect to 192.168.0.10:541, local 192.168.0.30:16648.
2026-06-14 18:22:06 FGFMs: Load Cipher [DES:!3DES:!ECDH:!DHE:!AES:!CAMELLIA:!SEED:!RC4:!PSK:!IDEA:!ARIA:@STRENGTH:@SECLEVEL=0]
2026-06-14 18:22:06 FGFMs: Load TLS 1.3 Cipher [TLS_AES_256_GCM_SHA384:TLS_CHACHA20_POLY1305_SHA256:TLS_AES_128_GCM_SHA256]
2026-06-14 18:22:06 FGFMs: Set self_initiated = 1
2026-06-14 18:22:06 FGFMs: before SSL initialization
2026-06-14 18:22:06 FGFMs:       CA to broadcast: subject fortinet-ca2, issuer fortinet-ca2
2026-06-14 18:22:06 FGFMs: Broadcast 1 CA subject names to FMG
2026-06-14 18:22:06 FGFMs: SSLv3/TLS write client hello
2026-06-14 18:22:06 FGFMs: SSLv3/TLS read server hello
2026-06-14 18:22:06 FGFMs: SSLv3/TLS write change cipher spec
2026-06-14 18:22:06 FGFMs: SSLv3/TLS write client hello
2026-06-14 18:22:07 FGFMs: SSLv3/TLS write client hello
2026-06-14 18:22:07 FGFMs: SSLv3/TLS read server hello
2026-06-14 18:22:07 FGFMs: TLSv1.3 read encrypted extensions
2026-06-14 18:22:07 FGFMs: SSLv3/TLS read server certificate request
2026-06-14 18:22:07 FGFMs: Verified CA certificate 2: (subject: fortinet-ca2, issuer: fortinet-ca2)
2026-06-14 18:22:07 FGFMs: Verified CA certificate 1: (subject: fortinet-subca2001, issuer: fortinet-ca2)
2026-06-14 18:22:07 FGFMs: Verified peer certificate 0: (subject: FMG-VMTM26006853, issuer: fortinet-subca2001)
2026-06-14 18:22:07 FGFMs: SSLv3/TLS read server certificate
2026-06-14 18:22:07 FGFMs: TLSv1.3 read server certificate verify
2026-06-14 18:22:07 FGFMs: SSLv3/TLS read finished
2026-06-14 18:22:07 FGFMs: SSLv3/TLS write client certificate
2026-06-14 18:22:07 FGFMs: SSLv3/TLS write finished
2026-06-14 18:22:07 FGFMs: SSL negotiation finished successfully
2026-06-14 18:22:07 FGFMs: client:send
get auth
serialno=FGVMEVIY4IPWHN15
mgmtid=00000000-0000-0000-0000-000000000000
platform=FortiGate-VM64
fos_ver=800
minor=0
patch=0
build=167
branch=167
maxvdom=2
fg_ip=192.168.0.30
hostname=FGVMEVIY4IPWHN15
harddisk=no
biover=04000002
mgmt_mode=normal
enc_flags=0
mgmtip=192.168.0.30
mgmtport=443

Thought Leadership. Security Summit. Thursday, November 12th, PGA National Resort, Palm Beach Gardens, FL.
Thought Leadership. Security Summit. Thursday, October 8th. Disney's Grand Californian Hotel & SPA, Anaheim, CA.
Security Operations Summit: Modernize SecOps. Operate AI-Native.AMER: November 4 | 9:00 AM PST. India and SAARC: November 5 | 10:00 AM IST. EMEA: November 5 | 10:30 AM CET. APAC: November 5 | 11:00 AM SGT