
sjoshi
Staff
Staff
August 19, 2025

Troubleshooting Tip: RADIUS Configuration Purged When Pushing Policy Package to FortiGate Devices via FortiManager

Description


This article describes an issue where RADIUS configurations on newly added FortiGate devices are removed after pushing a policy package from FortiManager.


Scope


FortiGate, FortiManager.


Solution


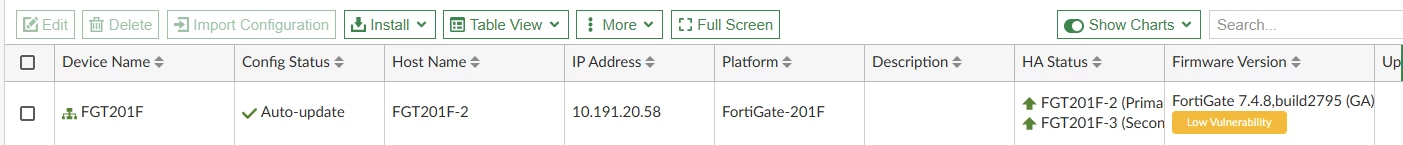
FortiGate is added in FortiManager, andthe  connection status is up:
 

1.PNG


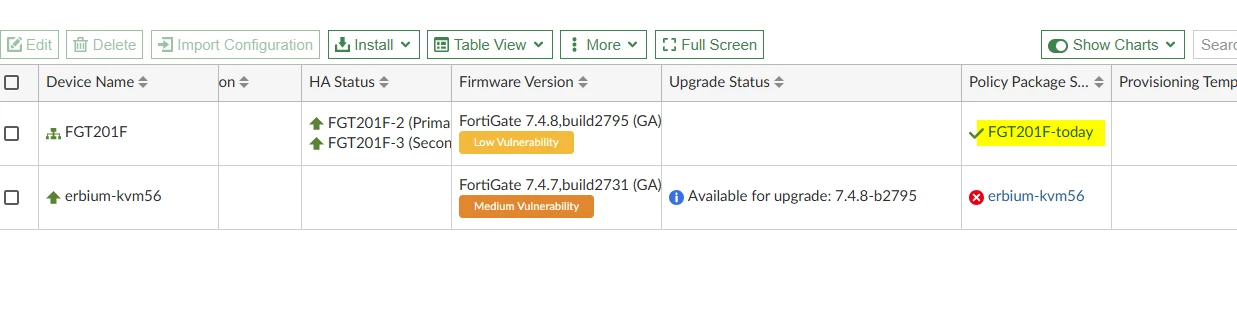
Policy package assigned to the device:
 

1.PNG


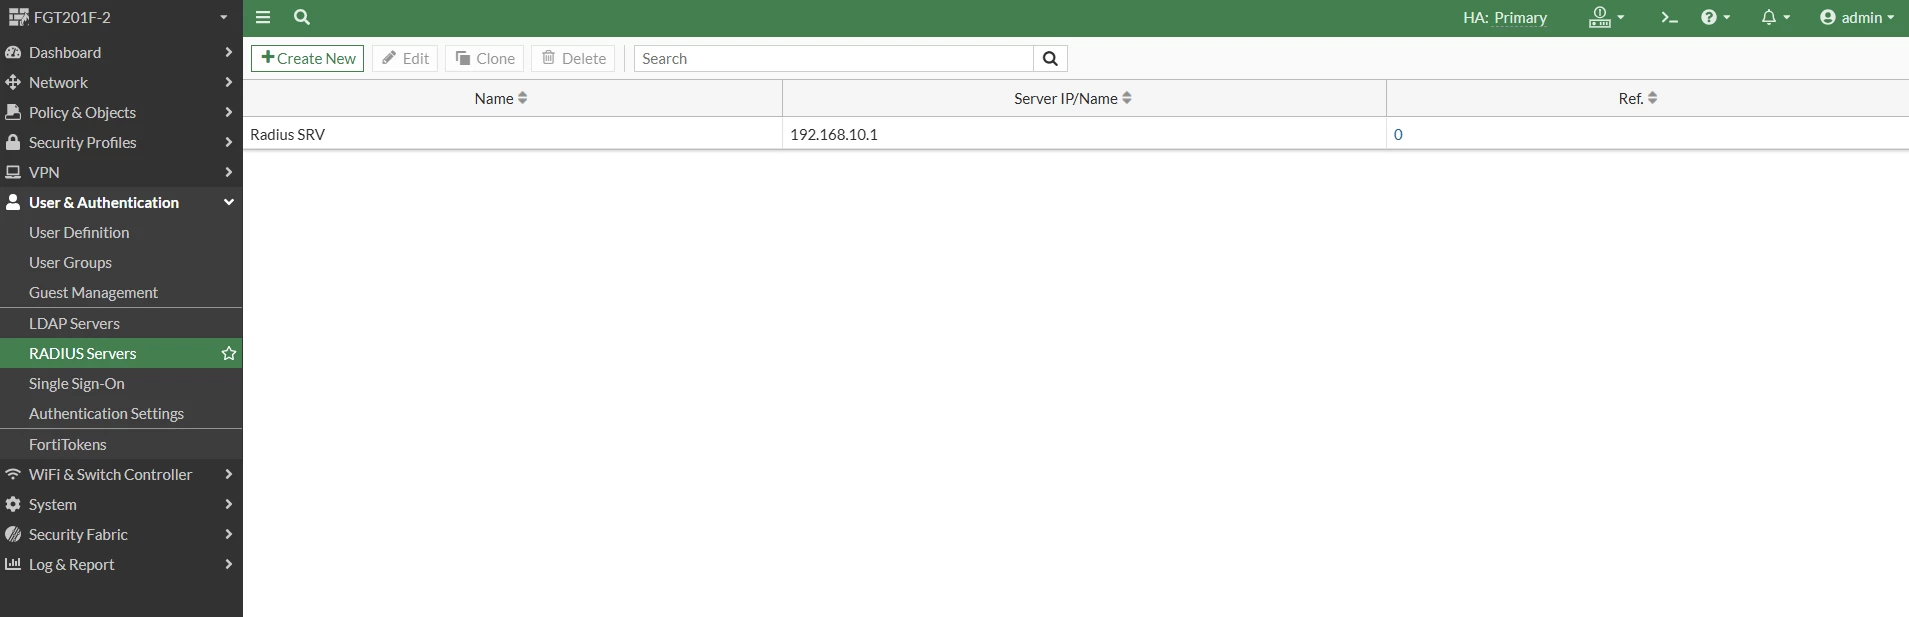
Radius Config present on the FortiGate before policy package push:
 

1.PNG


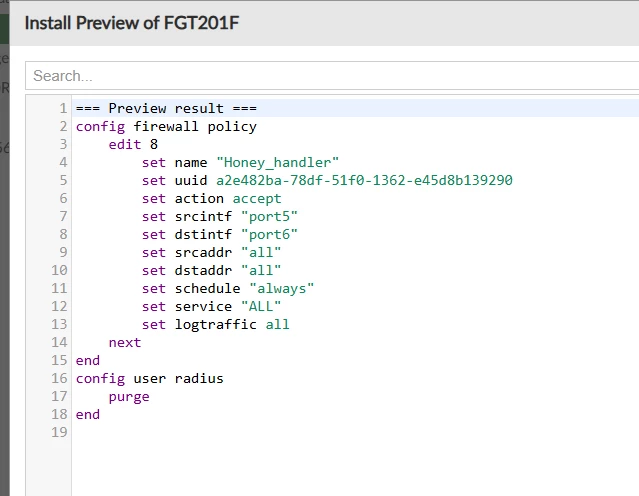
The policy package is pushed by creating a new policy, and the installation preview logs clearly show that the RADIUS server configuration is being purged:
 

1.PNG


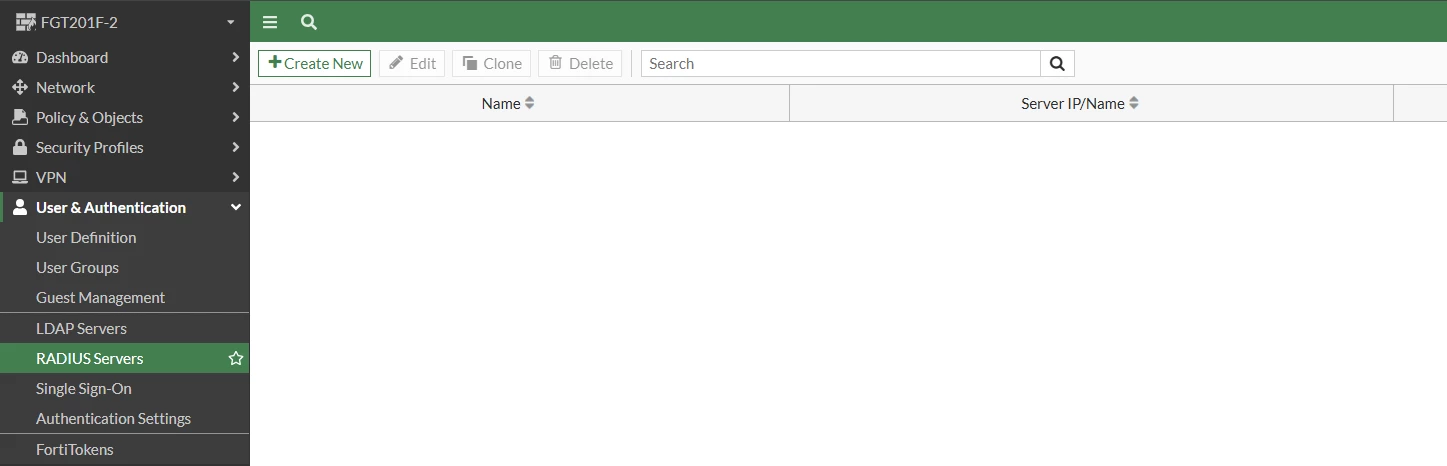
On the FortiGate, the RADIUS configuration is no longer visible as it has already been removed.
 

1.PNG


FortiManager purges the RADIUS server configuration because it is not referenced in any firewall policy. During a policy package installation, FortiManager is expected to remove radius configurations that have zero references.


The recommended approach is to create the RADIUS server configuration directly in FortiManager, include it in the relevant policy package, and then use the Install Wizard to deploy the package to the FortiGate.
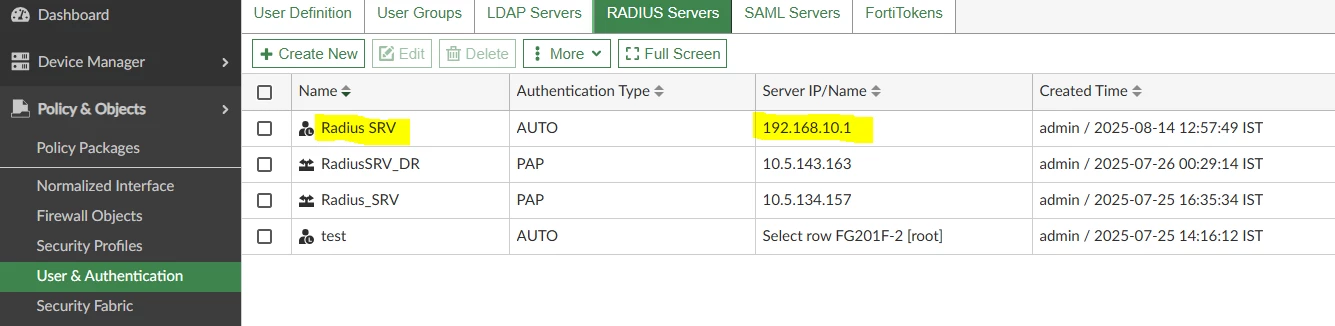
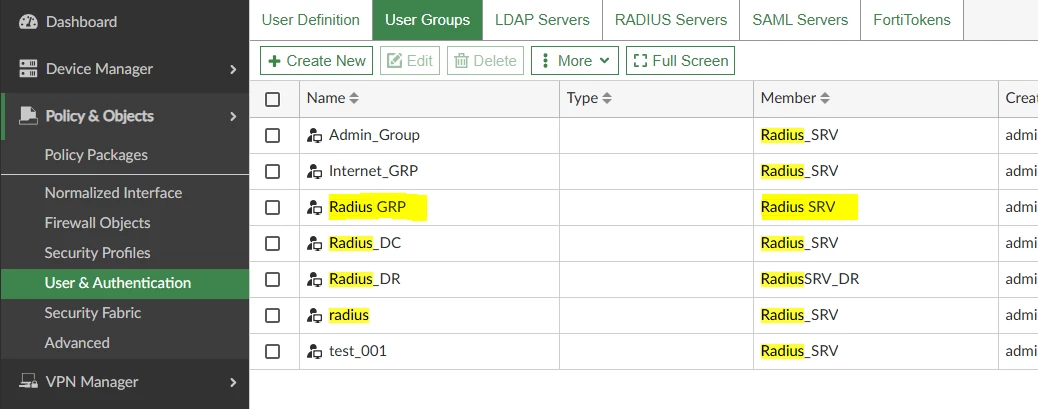
 

1.PNG


1.PNG


When the policy package is pushed, FortiManager installs the RADIUS configuration, and this time the configuration is not purged.
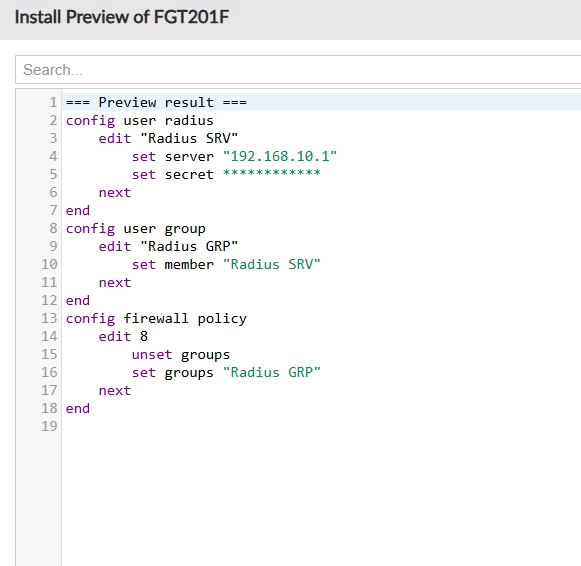
 

1.PNG


After the policy package is installed, the RADIUS configuration is present on the FortiGate.
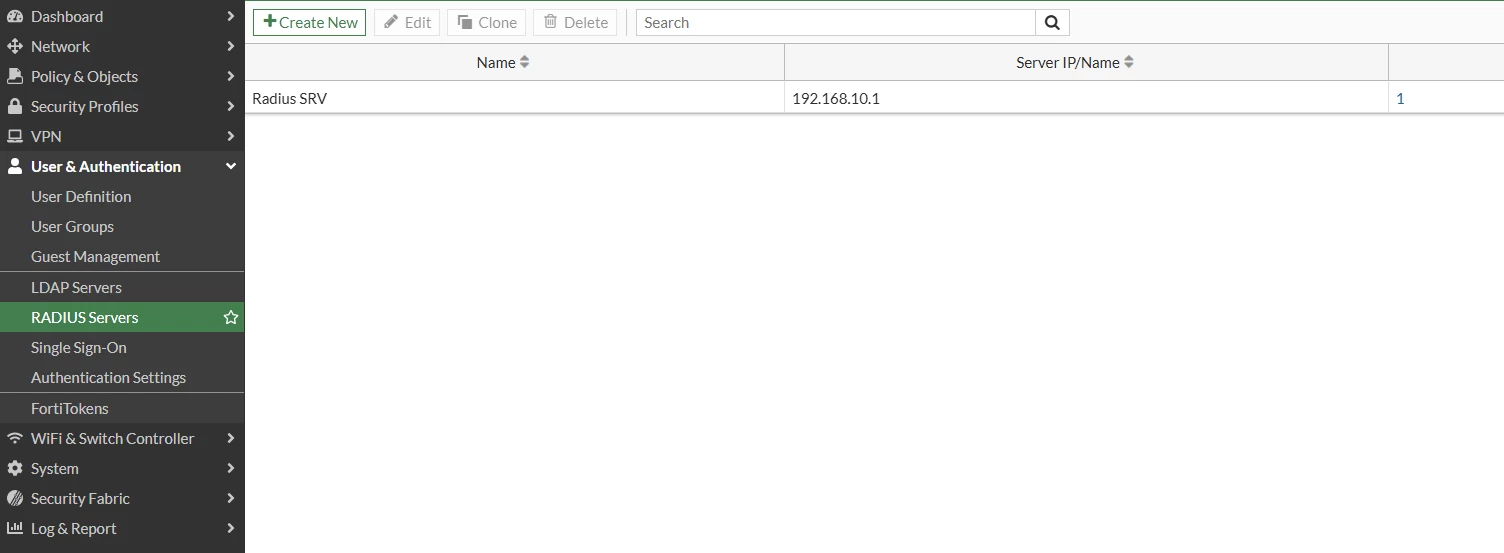
 

1.PNG

    2 replies

    FranFisc1
    Visitor III
    September 29, 2026

    We have a RADIUS Server defined in FMG.
    It is required by the the FGT integrated switch controller
    to do RADIUS based NAC/802.1X with FortiSwitches in a MultiVendor environment.

    When defining advanced settings like CoA on the Gate, the Config DB is auto.upated correctly on the FMG.
    On the next install:
    Not the RADIUS server itself, but its advanced settings like accounting servers, CoA enabled etc. are purged
    The server is referenced as member of  firewall group in Switch Controller Port policies.


    Here is the log from an install
    Starting log (Run on device)


    Start installing
    XXX-Y-01(Primary)  config user radius
    XXX-Y-01(Primary) (radius)  edit "ISE01_wired_dotX"
    XXX-Y-01(Primary) (ISE01_wired_dotX)  config accounting-server
    XXX-Y-01(Primary) (accounting-server)  purge
    XXX-Y-01(Primary) (accounting-server)  end
    XXX-Y-01(Primary) (ISE01_wired_dotX)  unset acct-interim-interval
    XXX-Y-01(Primary) (ISE01_wired_dotX)  unset radius-coa
    XXX-Y-01(Primary) (ISE01_wired_dotX)  unset radius-port
    XXX-Y-01(Primary) (ISE01_wired_dotX)  unset auth-type
    XXX-Y-01(Primary) (ISE01_wired_dotX)  next
    XXX-Y-01(Primary) (radius)  end


    ---> generating verification report
    <--- done generating verification report


    install finished

    FranFisc1
    Visitor III
    September 29, 2026

    Found the root cause:
    When creating the RADIUS Server, FMG creates a “per device mapping” for each managed firewall.
    Looks like the Per-Device-mapped settings i.e. “radius-coa” “auth-type” etc. are not inherited initially from the RADIUS Server definition.

    Thought Leadership. Security Summit. Thursday, November 12th, PGA National Resort, Palm Beach Gardens, FL.
    Thought Leadership. Security Summit. Thursday, October 8th. Disney's Grand Californian Hotel & SPA, Anaheim, CA.
    Security Operations Summit: Modernize SecOps. Operate AI-Native.AMER: November 4 | 9:00 AM PST. India and SAARC: November 5 | 10:00 AM IST. EMEA: November 5 | 10:30 AM CET. APAC: November 5 | 11:00 AM SGT


