


Troubleshooting Tip: RADIUS authentication issue with Cisco ISE via IPSec/IKEv2 tunnel
| Description | This article describes a RADIUS Authentication issue with Cisco ISE via IPSec/IKEv2 tunnel. The issue occurs when the user is unable to connect to the VPN using IKEv2, and the Cisco ISE returns an Access-Reject message to FortiGate.
Network topology: Firewall ===VPN/IKEv2=== CiscoISE(Radius server)
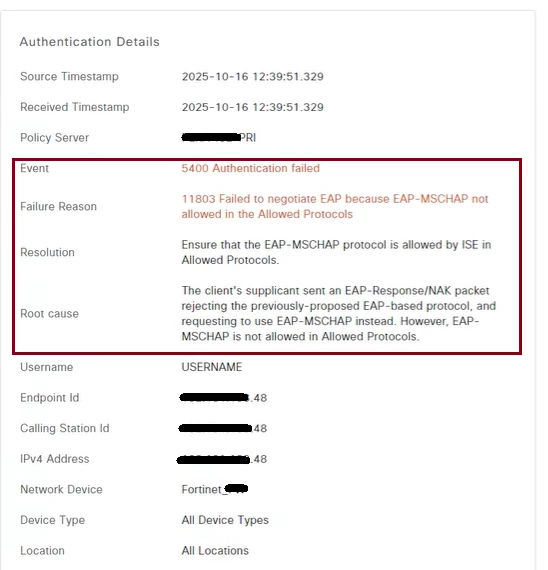
This is the log from Cisco ISE:
 |
| Scope | FortiGate, RADIUS. |
| Solution |
SSH1:
diagnose sniffer packet any "host [radius_IP] and port (1812 or 1813)" 6 0 l
SSH2:
diagnose debug reset diagnose debug console timestamp enable diagnose debug application ike -1 diagnose debug application fnbamd -1 diagnose debug application eap_proxy -1 diagnose vpn ike log filter rem-addr4 [wan_IP_of_client] diagnose debug enable
"...
2025-10-16 12:03:15 [595] __create_access_request-Created RADIUS Access-Request. Len: 255.
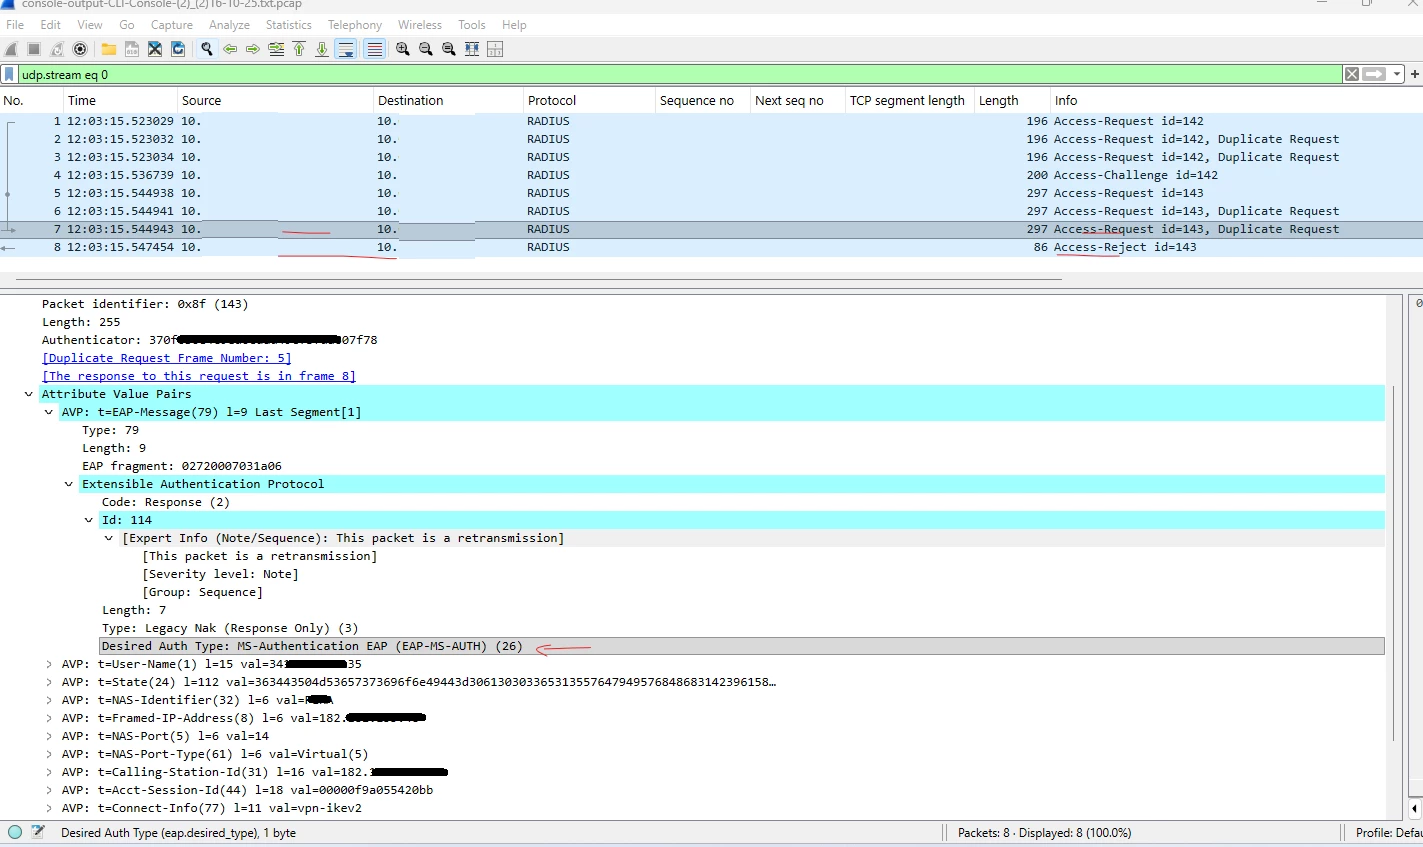
The packet sniffer output showed that FortiGate is suggesting using EAP-MSCHAPv2 (type 26), which is not supported by Cisco ISE - this is why Cisco sent the Access-Reject message:
 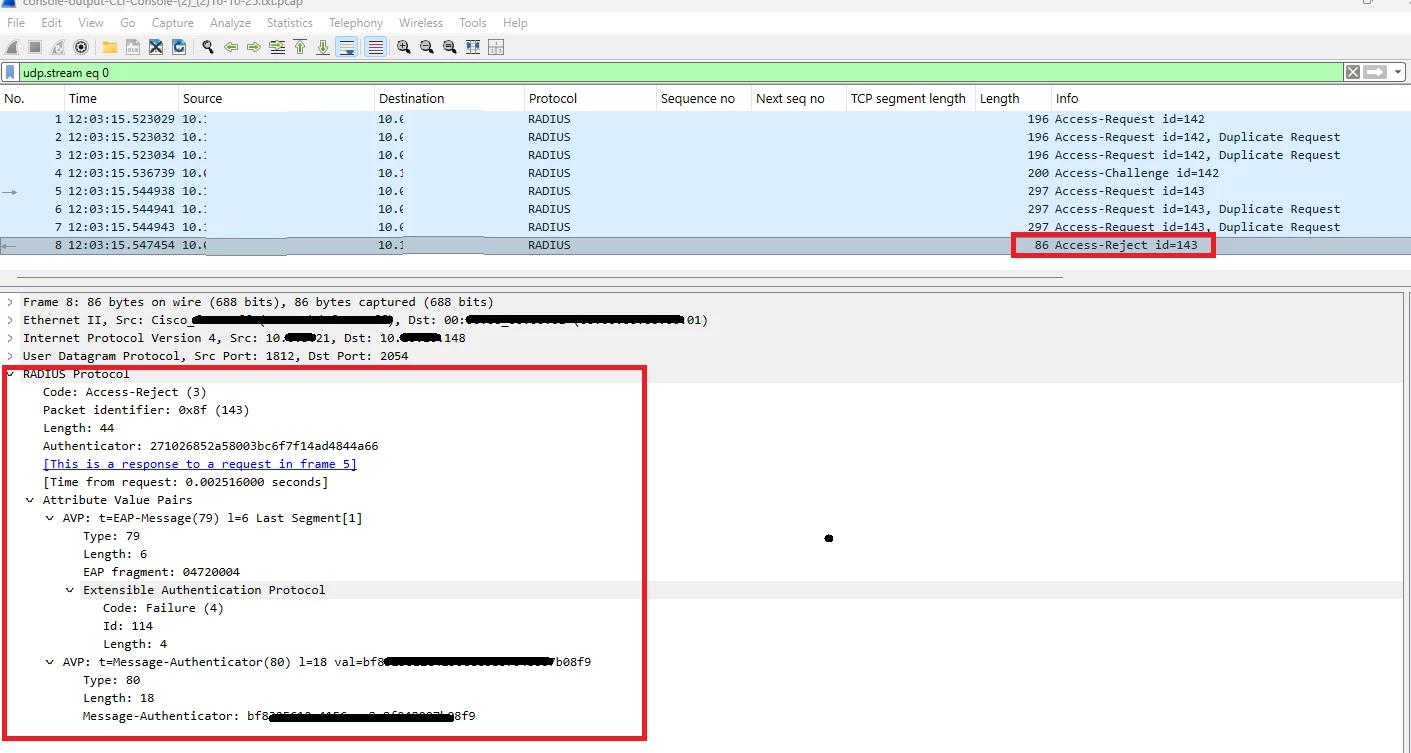
The solution is to use IKE version 1 in VPN settings.
Related article: |


