
Troubleshooting Tip: 'No DN is Found' error during LDAP authentication failure for usernames with domain names in FortiGate
| Description | This article describes the steps to resolve issues related to LDAP authentication failure when using usernames with domain names 'username@domain.local'. |
| Scope | FortiOS, FortiGate, LDAP. |
| Solution | Navigate to the LDAP settings via FortiGate CLI to understand the current configuration by using commands:
config user ldap show
Run the following debug commands to check for the error 'No DN is Found'.
diagnose debug enable diagnose debug enable
To stop the debug, run the following commands:
diagnose debug disable diagnose debug reset
If debug logs show 'No DN is found', this output will appear:
[1100] fnbamd_ldap_recv-Response length: 16, server: 192.168.1.11
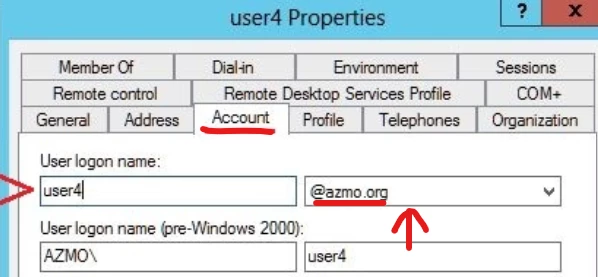
Set the CNID attribute to 'UserPrincipalName' to allow successful authentication using usernames with domain names. Here are the commands to run on the CLI:
config user ldap edit <LDAP Server Name> end
Note:
Related articles: Troubleshooting Tip: FortiGate LDAP troubleshooting and debug logs created by fnbamd Technical Tip: Using logon name for the LDAP authentication |