
Troubleshooting Tip : Network instability when enabling MCLAG access links due to manually created ICL
| Description | This article describes the symptoms and possible solutions of a Multi‑Chassis Link Aggregation Group (MCLAG) deployment using FortiSwitch devices. Connecting access switches to both distribution switches may cause a network-wide reset or extended convergence time if the Inter-Chassis Link (ICL) was manually created instead of automatically generated. |
| Scope | FortiGate, FortiSwitch. |
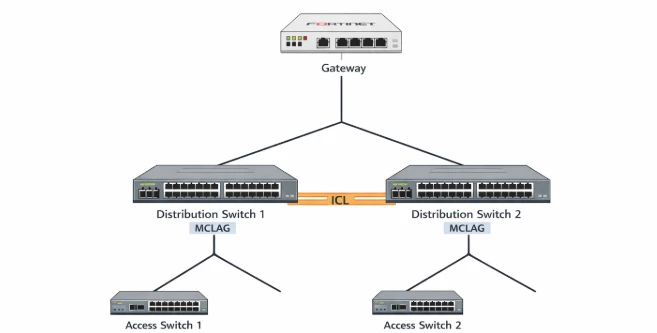
| Solution | An example topology is shared below:
In this environment, when a second uplink from an access switch is connected to the second distribution switch, the following can occur that entire Layer-2 network resets, switches temporarily lose connectivity, network convergence may take longer than expected, or performance instabilities. diagnose switch mclag peer-consistency-check
Running diagnostic, it may take sometime... ** Comparing "switch.global.mclag-split-brain-detect" config ....OK mclag-trunk-name peer-config lacp-state stp-state local-ports remote-ports
The MISMATCH state indicates configuration inconsistency between MCLAG peers. The issue occurs because the MCLAG Inter-Chassis Link (ICL) trunk was manually created. Although the initial configuration generated an automatic MCLAG ICL trunk, it was later deleted and recreated manually. This resulted in an ICL that did not match the expected internal MCLAG configuration, even though it appeared correct in the configuration. To resolve the issue, allow the switches to automatically create the MCLAG ICL trunk instead of manually configuring it.
This allows the switches to correctly identify the link as an MCLAG ICL trunk rather than a standard LAG trunk or a simple ICL trunk, where one link may remain blocked to prevent loops.
diagnose switch-controller switch-info mclag peer-consistency-check Related article: |