


Troubleshooting Tip: Managed FortiSwitch coming online on wrong FortiGate
Description
This article describes an issue where FortiSwitch shows as online on the wrong FortiGate.
.
Scope
FortiGate, FortiSwitch.
Solution
Setup:
In some deployments, it is necessary to manage FortiSwitch on the respective firewalls with an inter-switch link.
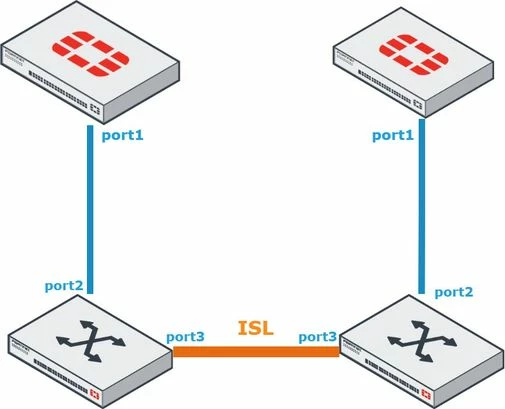
For example, refer to the diagram below, where the requirement is that 'FSW1' has to be be managed by 'FGT1' and 'FSW2' has to be managed by 'FGT2'.
In these situations, issues may appear where both FortiSwitches show up on both FortiGates and connection fluctuates.
Solution:
By default, all FortiSwitch ports are mapped with 'default-auto-isl' LLDP profile.
That is the reason why when 2 managed FortiSwitches are connected with inter switch link (ISL), both FortiSwitches will automatically form a FortiLink trunk and will try to come online on FortiGate.
For example:
FSW# show switch physical-port port1 <----- 'LLDP' profile is set to 'default-auto-isl'.
config switch physical-port
edit "port1"
set lldp-profile "default-auto-isl"
set speed auto
next
end
config switch physical-port
edit "port1"
set lldp-profile "default-auto-isl"
set speed auto
next
end
FSW # show switch lldp profile default-auto-isl <----- 'default-auto-isl' 'LLDP' profile has 'auto-isl enable'.
config switch lldp profile
edit "default-auto-isl"
set auto-isl enable
next
end
While deploying these setups, follow these steps:
- First bring up 'FSW1' on 'FGT1' and 'FSW2' on 'FGT2'. Do not connect a link between both FortiSwitches (Port3).
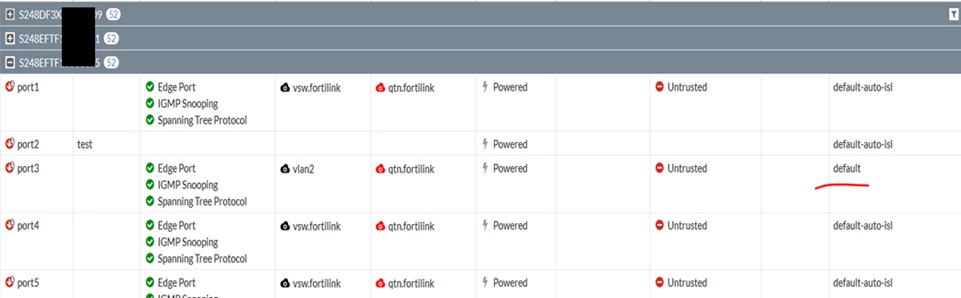
- Map the 'default' 'LLDP' profile on port3 of both FortiSwitches.
The 'default' LLD profile has auto-isl disabled, so FortiSwitches will not form ISL FortiLink trunk and will not come online on other FortiGates.
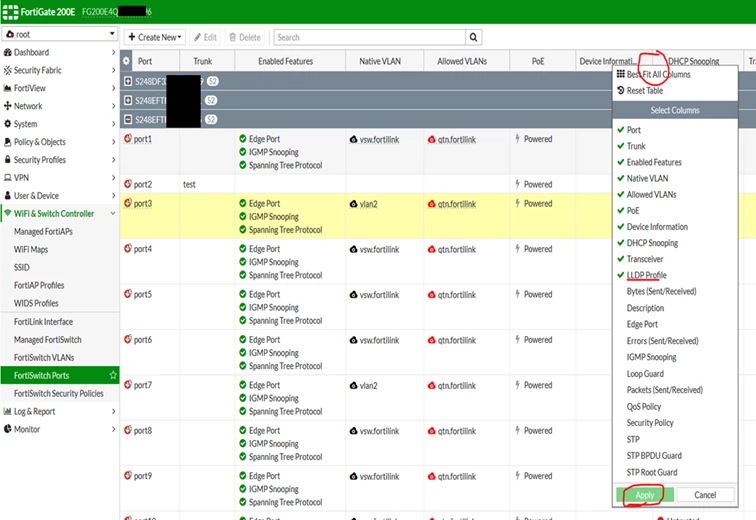
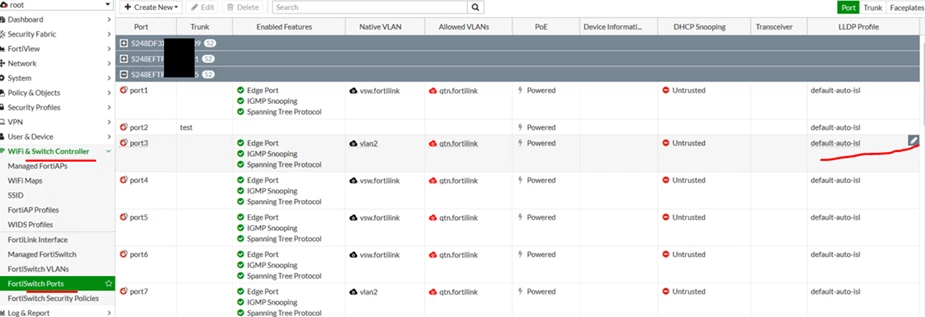
Map the profile from FortiGate GUI where possible. Go to WiFi & Switch Controller -> FortiSwitch Ports, select the Port number, select the 'LLDP' profile column, then edit and map the 'default' 'LLDP' profile.
If the LLDP profile column is not visible, add the column by right-clicking and then adding the column:
- On 'FGT1', disable discovery for the 'FSW2' serial number, and on 'FGT2', disable discovery for the 'FSW1' serial. For example:
FortiGate # config switch-controller global
FortiGate (global) set disable-discovery <switch serial#>
end
FortiGate (global) set disable-discovery <switch serial#>
end
Related document:
Managed FortiSwitch guide - Fortinet documentation
If an inter-switch link (ISL) was already connected and FortiSwitches show up on the wrong FortiGate, follow these steps:
- Connect ISL Port3 on both FortiSwitches. The FortiSwitches will not come online on other FortiGates.
If an inter-switch link (ISL) was already connected and FortiSwitches show up on the wrong FortiGate, follow these steps:
- Disconnect the ISL between the FortiSwitches.
- Delete the switch entry from the wrong FortiGate. Go to Managed FortiSwitch and select the FortiSwitch and select 'Delete'.
- Gain CLI access to both FortiSwitches and delete the FortiLink ISL trunk.
For example, if FortiSwitch S248EFTF1-----75 Port23 is connected to FortiSwitch S248EFTF18-----1 Port23, both FortiSwitches will have an ISL FortiLink trunk which gets automatically formed.
Delete the trunk.
On FortiSwitch S248EFTF1-----75:
On FortiSwitch S248EFTF1-----75:
# sh switch trunk
edit "8EFTF18-----1-0"
set mode lacp-active
set auto-isl 1
set auto-isl 1
set members "port23"
config switch trunk
delete "8EFTF18-----1-0"
end
config switch trunk
delete "8EFTF18-----1-0"
end
On FortiSwitch S248EFTF18-----1.
sh switch trunk
edit "8EFTF18000075-0"
set mode lacp-active
set auto-isl 1
set members "port23"
config switch trunk
delete "8EFTF1-----75-0"
end
edit "8EFTF18000075-0"
set mode lacp-active
set auto-isl 1
set members "port23"
config switch trunk
delete "8EFTF1-----75-0"
end
Once the trunks are deleted, follow steps 1-4.
Related documentation:
FortiSwitch 6.4 documentation
LLDP profile, page 117 - Fortinet documentation


