This article is recommended reading, as it explains details about link monitors: Technical Tip: Link monitor.
Setup:
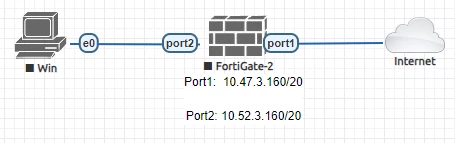 For testing purposes, assume that the FortiGate's port1 IP address 10.47.3.160/20 is a Public IP address.
Configure the link-monitor setup as below:
config system link-monitor
    edit "1"
        set srcintf "port1"
        set server "1.1.1.1"
    next
end
diagnose sys link-monitor status

Link Monitor: 1, Status: alive, Server num(1), cfg_version=0 HA state: local(alive), shared(alive)
Flags=0x1 init, Create time: Wed Sep 18 16:26:44 2024
Source interface: port1 (3)
VRF: 0
Interval: 500 ms
Service-detect: disable
Diffservcode: 000000
Class-ID: 0
Transport-Group: 0
Class-ID: 0
  Peer: 1.1.1.1(1.1.1.1)
        Source IP(10.47.3.160)
        Route: 10.47.3.160->1.1.1.1/32, gwy(10.47.15.254)
        protocol: ping, state: alive
                Latency(Min/Max/Avg): 2.112/9.297/3.764 ms
                Jitter(Min/Max/Avg): 0.022/7.098/1.242 ms
                Packet lost: 0.000%
                MOS: 4.401
                Number of out-of-sequence packets: 0
                Fail Times(0/5)
                Packet sent: 234, received: 234, Sequence(sent/rcvd/exp): 235/235/236
Once the Internal LAN IP is use as the source-ip in link-monitor, the Status will fail (dead).
config system link-monitor
    edit "1"
        set srcintf "port1"
        set server "1.1.1.1"
        set source-ip 10.52.3.160
    next
end
diagnose sys link-monitor status

Link Monitor: 1, Status: dead, Server num(1), cfg_version=0 HA state: local(dead), shared(dead)
Flags=0x9 init log_downgateway, Create time: Wed Sep 18 16:30:19 2024
Source interface: port1 (3)
VRF: 0
Source IP: 10.52.3.160
Interval: 500 ms
Service-detect: disable
Diffservcode: 000000
Class-ID: 0
Transport-Group: 0
Class-ID: 0
  Peer: 1.1.1.1(1.1.1.1)
        Source IP(10.52.3.160)
        Route: 10.52.3.160->1.1.1.1/32, gwy(10.47.15.254)
        protocol: ping, state: dead
                Packet lost: 100.000%
                MOS: 4.350
                Number of out-of-sequence packets: 0
                Recovery times(0/5) Fail Times(4/5)
                Packet sent: 105, received: 0, Sequence(sent/rcvd/exp): 106/0/0
This is expected behavior because the source of the probes are local traffic generated by the FortiGate. Local traffic will not hit a Firewall Policy so the source IP (which is the Internal LAN IP) will not be Translated (NAT) into a Public IP address of port1.
The same behavior is encountered if the Internal LAN IP or Loopback interface is used as a source-ip in a ping operation, as shown in the following articles:
| 




