

ibituya
Staff
Staff
January 23, 2025

Troubleshooting Tip: LDAP user not synchronizing to FortiToken Cloud

  • January 23, 2025
  • 0 replies
  • 913 views

Description

This article describes a possible case of why an LDAP user is not synchronizing to FortiToken Cloud.

Scope

FortiGate, FortiToken Cloud.

Solution

The two-factor-filter option in the LDAP setting is the filter string that controls which Active Directory users will be synchronized to FortiToken Cloud for two-factor authentication.

Example Filters:


Example 1: All users from a specific group:


set two-factor-filter "(&(objectCategory=Person)(sAMAccountName=*)(memberOf=cn=FTC Users,ou=FortiGate,dc=winserver,dc=lab))"


Example 2: All users with matching email address:


set two-factor-filter "(&(SAMAccountName=*)(mail=*fortinet*))"


In the given scenario, the LDAP server is configured to have a filter for the Active Directory group 'FTC Users' to be synchronized to FortiToken Cloud for two-factor authentication:


config user ldap
    edit "WINSERVER-AD"
        set server "10.10.10.10"
        set cnid "sAMAccountName"
        set dn "ou=FortiGate,dc=winserver,dc=lab"
        set type regular
        set two-factor fortitoken-cloud
        set two-factor-filter "(&(objectCategory=Person)(sAMAccountName=*)(memberOf=cn=FTC Users,ou=FortiGate,dc=winserver,dc=lab))"
        set username "WINSERVER\\fgt.svc"
        set password [masked]
    next
end


Users are automatically synchronized to the FortiToken Cloud portal, however, the synchronization process can be manually triggered by running the below command on the FortiGate:


execute fortitoken-cloud sync


To verify the list of users that are synchronized to FortiToken Cloud, run the given command:


diagnose fortitoken-cloud show users


If the expected users are not added to FortiToken Cloud, run the following commands to check the FortiGate connectivity to the FortiToken Cloud server:


diagnose fortitoken-cloud server
diagnose fortitoken-cloud show service


If the FortiToken Cloud service status is verified connected and ready, run the below debug and trigger a manual sync:


diagnose fortitoken-cloud debug enable
diagnose debug enable
execute fortitoken-cloud sync


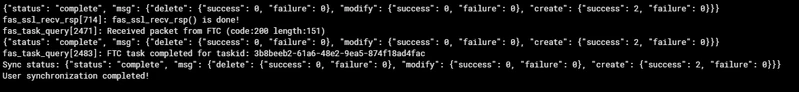
The debug output will show the sync status and the number of users that are successfully synchronized or failed to synchronize.
 

2.PNG


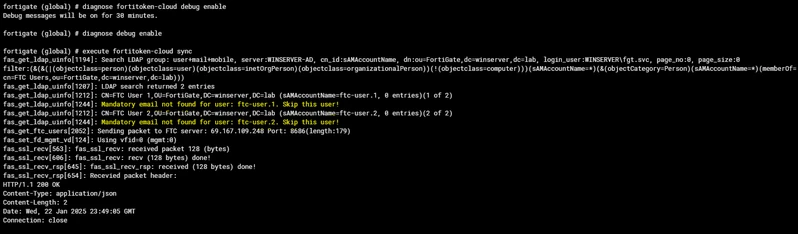
If there are LDAP users that are not getting synchronized, the 'fortitoken-cloud debug' will also show if the user was skipped during synchronization. From the given output below, the LDAP users were skipped due to missing or not valid email assignments.
 

1.PNG


Ensure that the user has a proper email address assigned on the AD server as this is where the FortiToken Cloud activation email will be sent.

    Thought Leadership Security Summit. Outpace New Threats with AI - enhanced defense. Tuesday, Septmeber 15, 8:30 AM - 2:30 PM PT. The Golf Club at Newcastle, WA.
    Virtual event | September 2026. SASE summit. The age of autonomous trust. Register here!

