To configure the ZTNA access to the LDAP server from FortiAuthenticator, refer to this document: Accessing an AD server with a zero trust tunnel on FortiAuthenticator.
The following errors are observed on FortiAuthenticator when trying to query for group information.
Sample error 1:
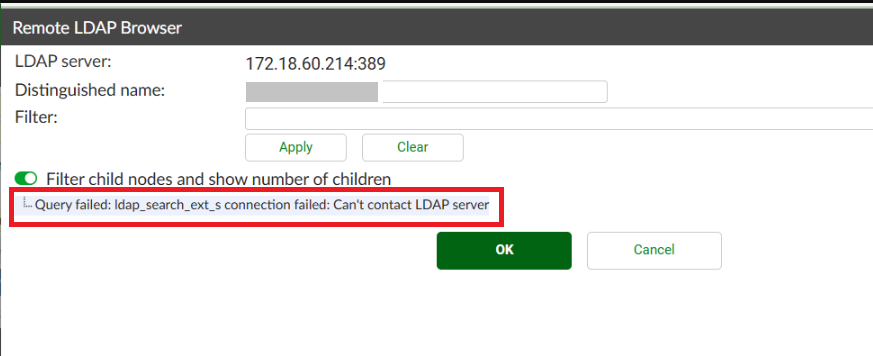
Sample error 2:
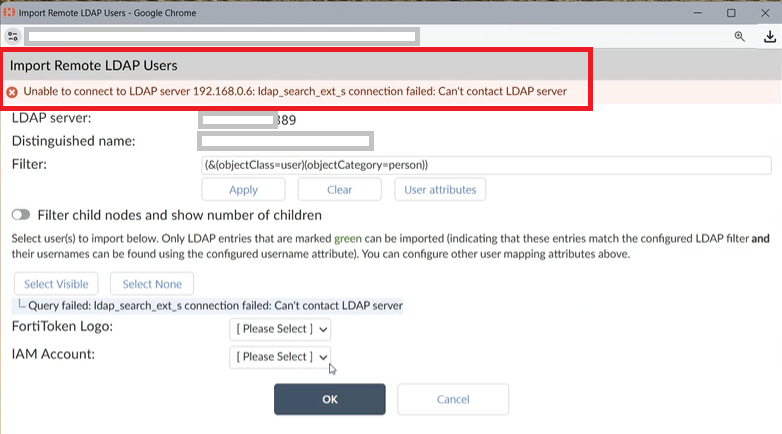
On FortiGate ZTNA logs, traffic is arriving but not getting forwarded to the LDAP server.
date=2025-08-30 time=09:50:56 eventtime=1756504255838368856 tz="+1200" logid="0005000024" type="traffic" subtype="ztna" level="notice" vd="vdom1" srcip=1.1.1.1 srcport=49312 srcintf="port2" srcintfrole="undefined" dstcountry="Reserved" srccountry="Reserved" dstip=2.2.2.2 dstport=4443 dstintf="vdom1" dstintfrole="undefined" sessionid=178 service="tcp/4443" proxyapptype="ztna-proxy" proto=6 action="accept" policyid=1 policytype="proxy-policy" poluuid="29c3b1ae-3a63-51f0-d83f-ada730937f07" policyname="zt" appcat="unscanned" duration=0 vip="ztna4" vipincomingip=10.1.100.4 accessproxy="ztna4" clientdevicemanageable="manageable" clientcert="yes" wanin=0 rcvdbyte=0 wanout=0 lanin=3279 sentbyte=3279 lanout=6724
The WAD debugs output would show successful certificate authentication but connection closes. The below WAD debug commands use firewall policy 27 as a filter to reduce WAD output. For other available WAD filters, refer to Technical Tip: Using the 'diagnose wad debug' command to troubleshoot Explicit Web Proxy related issues
diagnose debug reset
diagnose debug disable
diagnose debug console timestamp  enable
diagnose wad filter firewall-policy 27
diagnose wad debug enable category all
diagnose wad debug enable level verbose
diagnose wad debug display pid enable
diagnose debug enable
To stop the debug:
diagnose wad debug clear
diagnose wad filter clear
diagnose debug disable
diagnose debug reset
WAD output snippet:
[I]2026-08-27 14:51:39.789213 wad_vs_ssl_port_caps_c2p_on_server_hello:12165 wsp 0x7ff3e456e820 handshake sent ServerHello 3.3
[I]2026-08-27 14:51:39.789222 wad_vs_ssl_port_caps_cert_req :13601 1461:FAC: requested certs from client. ca_store is empty.
[I]2026-08-27 14:51:39.789225 wad_vs_ssl_c2p_cert_req_add_trust_issuers:13556 1461:FAC: cas->x509 is (nil) or ca list is empty.
..........
[I]2026-08-27 14:51:39.851117 wad_vs_ssl_access_proxy_on_clt_certs:13022 1461:FAC: received certs from the client.
[I]2026-08-27 14:51:39.851123 wad_ssl_cert_auth_find :177 Found auth_info (stable)
[I]2026-08-27 14:51:39.851125 wad_vs_ssl_access_proxy_on_clt_certs:13026 1461:FAC: cert cache cert(0x7ff3e262d798) authi(0x7ff3e4de39e0)
[V]2026-08-27 14:51:39.851128 wad_vs_ssl_access_proxy_on_clt_certs:13031 1461:FAC: vs, Found the cert, and issued by:cert-auth-case
[V]2026-08-27 14:51:39.851130 wad_vs_ssl_access_proxy_on_clt_certs:13036 1461:FAC: hit the cached auth_result(7)
[I]2026-08-27 14:51:39.851133 wad_vs_ssl_access_proxy_on_clt_certs:13072 1461:FAC: Cert auth success. issued_by: cert-auth-case
[V]2026-08-27 14:51:39.854056 wad_vs_ssl_port_caps_on_dh_secret :12360 wsp 0x7ff3e456e820 DH secret generation status 0: succeeded
..........
[I]2026-08-27 14:51:39.908797 wad_dump_http_request :2911 hreq=0x7ff3e15ce048 Received request from client: 1.1.1.1:39786
GET /tcp?address=192.168.0.6&port=389&tls=1 HTTP/1.1
Host: 38.122.185.163
Upgrade: websocket
Connection: upgrade
User-Agent: FortiJumper (1.0)

[V]2026-08-27 14:51:39.908802 wad_http_marker_uri :1270 path=/tcp len=4
[V]2026-08-27 14:51:39.908807 wad_http_parse_host :1649 host_len=14
[I]2026-08-27 14:51:39.908810 wad_http_parse_host :1681 host=[14]2.2.2.2
[I]2026-08-27 14:51:39.908814 wad_http_str_canonicalize :2196 enc=0 path=/tcp len=4 changes=0
[I]2026-08-27 14:51:39.908817 wad_http_str_canonicalize :2198 end=4 path=address=192.168.0.6&port=389&tls=1 len=34 changes=0
[V]2026-08-27 14:51:39.908820 wad_http_normalize_uri :2570 host_len=14 path_len=4 query_len=34
[I]2026-08-27 14:51:39.908823 wad_http_req_detect_special :16175 captive_portal detected: false, preflight=(null)
[I]2026-08-27 14:51:39.908828 wad_vs_proxy_match_gwy :4313 1461:FAC: matching gwy with vhost(_def_virtual_host_)
[V]2026-08-27 14:51:39.908831 wad_vs_proxy_match_vhost :4394 1461:FAC: matching vhost by: 2.2.2.2
[V]2026-08-27 14:51:39.908833 wad_vs_matcher_map_find :740 Empty matcher!
[V]2026-08-27 14:51:39.908836 wad_vs_proxy_match_vhost :4397 1461:FAC: no host matched.
[I]2026-08-27 14:51:39.908838 wad_vs_proxy_match_gwy :4332 1461:FAC: matching gwy by (/tcp) with vhost(_def_virtual_host_).
[V]2026-08-27 14:51:39.908843 wad_pattern_matcher_search :1221 pattern-match succ:/tcp
[I]2026-08-27 14:51:39.908846 wad_vs_proxy_match_gwy :4370 1461:FAC: Matched gwy(2) type(tcp-fwd).
[I]2026-08-27 14:51:39.908849 wad_http_srv_selector_static_make :1712 make static server selector.
[I]2026-08-27 14:51:39.908853 wad_vs_gwy_tcp_dst_ovrd :3277 1461:FAC:2: req(0x7ff3e15ce048) query(address=192.168.0.6&port=389&tls=1)
[I]2026-08-27 14:51:39.908857 wad_vs_gwy_tcp_get_parameters :3047 1461:FAC:2: got the addr=192.168.0.6.
[I]2026-08-27 14:51:39.908861 wad_vs_gwy_tcp_dst_ovrd :3316 1461:FAC:2: req(0x7ff3e15ce048) found the server by matching ip(192.168.0.6).
[V]2026-08-27 14:51:39.908865 wad_http_req_exec_act :14651 dst_addr_type=3 wc_nontp=0 sec_web=1 web_cache=0 req_bypass=0
[V]2026-08-27 14:51:39.908870 wad_get_dst_intf_idx2 :174 Matched route cache.local=0, oif=34
[V]2026-08-27 14:51:39.908901 wad_route_query_pol_rt :149 NO matched policy route.
[V]2026-08-27 14:51:39.908905 wad_http_req_get_dst_intf :13275 vd=0 dst=192.168.0.6 ifidx=34
[I]2026-08-27 14:51:39.908910 wad_session_update_tcp_window_options:940 app http set window-type auto-tuning
[I]2026-08-27 14:51:39.908914 wad_http_req_proc_policy :10899 ses_ctx:ct|P|M|H|C|A1|O conn_srv=0 fwd_srv=<nil>
[V]2026-08-27 14:51:39.908919 __wad_hauth_user_node_hold :2375 wad_user_node_stats_hold (574): holding node 0x7ff3e4df3680
[V]2026-08-27 14:51:39.908922 __wad_hauth_user_node_hold :2375 wad_http_session_upd_user_node (7852): holding node 0x7ff3e4df3680
[I]2026-08-27 14:51:39.908925 wad_http_req_proc_policy :11017 policy result:vf_id=0:0 sec_profile=0x7ff3e34c68c8 set_cookie=0
[V]2026-08-27 14:51:39.908929 wad_http_build_tcp_fwd_200_resp :557 Authentication is done.
[I]2026-08-27 14:51:39.908935 wad_session_update_tcp_window_options:940 app http set window-type auto-tuning
[I]2026-08-27 14:51:39.908938 wad_http_req_proc_policy :10899 ses_ctx:ct|P|M|H|C|A1|O conn_srv=0 fwd_srv=<nil>
[I]2026-08-27 14:51:39.908940 wad_http_req_proc_policy :11017 policy result:vf_id=0:0 sec_profile=0x7ff3e34c68c8 set_cookie=0
[V]2026-08-27 14:51:39.908942 wad_http_msg_start_setup_proc :2251 msg(0x7ff3e15ce048) proc-setup started from: req_resp_ready.
[V]2026-08-27 14:51:39.908945 wad_http_def_proc_msg_plan :2213 msg(0x7ff3e15ce048) setting up processor(req_resp_ready)
[V]2026-08-27 14:51:39.908948 wad_http_msg_start_setup_proc :2251 msg(0x7ff3e6195b20) proc-setup started from: resp_forward.
[V]2026-08-27 14:51:39.908950 wad_http_def_proc_msg_plan :2213 msg(0x7ff3e6195b20) setting up processor(resp_forward)
[I]2026-08-27 14:51:39.908952 wad_dump_fwd_http_resp :2932 hreq=0x7ff3e15ce048 Forward response from Internal:

HTTP/1.1 200 OK
Connection: close
Content-Length: 0

[V]2026-08-27 14:51:39.908957 wad_ssl_app_port_out_ops_read :19880 sp=0x7ff3e456e820/10 plain down stream len=17 closed=0
[V]2026-08-27 14:51:39.908960 wad_ssl_app_port_out_ops_read :19880 sp=0x7ff3e456e820/10 plain down stream len=19 closed=0
[V]2026-08-27 14:51:39.908962 wad_ssl_app_port_out_ops_read :19880 sp=0x7ff3e456e820/10 plain down stream len=19 closed=0
[V]2026-08-27 14:51:39.908965 wad_ssl_app_port_out_ops_read :19880 sp=0x7ff3e456e820/10 plain down stream len=2 closed=0
[V]2026-08-27 14:51:39.908967 wad_ssl_app_port_out_ops_sync :19950 sp=0x7ff3e456e820/10 plain down stream state=3
[I]2026-08-27 14:51:39.908970 wad_ssl_app_port_txn_write :19836 wsp=0x7ff3e456e820/10 sync plain down stream len=57
[I]2026-08-27 14:51:39.908975 wad_ssl_app_port_txn_write :19849 wsp=0x7ff3e456e820/10 total fwded len=57, status 0
[I]2026-08-27 14:51:39.908979 wad_http_req_resp_fwd_done :5156 req(0x7ff3e15ce048) resp(0x7ff3e6195b20/(nil)) resp-fwd done!
The issue is caused by the user-agent checking when using the FortiJumper (v1.0) User-Agent from FortiAuthenticator Cloud. The fix allows connecting to the server regardless of user-agent values for ZTNA tcp-fwd traffic.
Resolution.
The behavior is addressed in FortiOS v7.6.7 and FortiOS v8.0.0. Release notes. Resolved Issues 7.6.7. Release notes. Resolved Issues 8.0.0. | 




