Scenario: FortiGate is deployed in Azure with a private IP address. NAT performed upstream using an Azure public IP address. IPsec VPN configured between FortiGate and Palo Alto firewall.
It can be noticed that Phase 1 and Phase 2 show UP on FortiGate, and the same can be verified using the below CLI commands and VPN event logs.
diagnose vpn tunnel list name <phase1-name>
diagnose vpn ike gateway list name <phase1-name>
However, Phase 1 is not established on the Palo Alto firewall. Palo Alto logs display the error message:
'received id_r <FortiGate Private IP> type ipaddr does not match peers id'.
In addition to Palo Alto logs, FortiGate IKE debug commands can be run to determine the root cause on the FortiGate end.
diagnose vpn ike log-filter dst-addr4 x.x.x.x <---- To filter using remote-gateway address.
diagnose vpn ike log filter rem-addr4 x.x.x.x <---- Command to filter using remote-gateway address. (v7.4.1 and above).
diagnose debug app ike -1 <----- To do the VPN debug.
diagnose debug console timestamp enable <----- To cross-check with VPN events.
diagnose debug enable <------ To display the debug output.
diagnose debug disable <----- To stop the debug output.
Leave the Local ID field blank on the FortiGate, and the remote end only needs to make the changes.
config vpn ipsec phase1-interfac
    edit <phase1-name>
        set localid ''
    next
end
From the GUI:
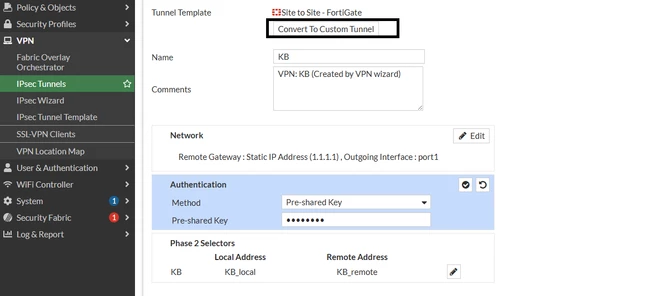
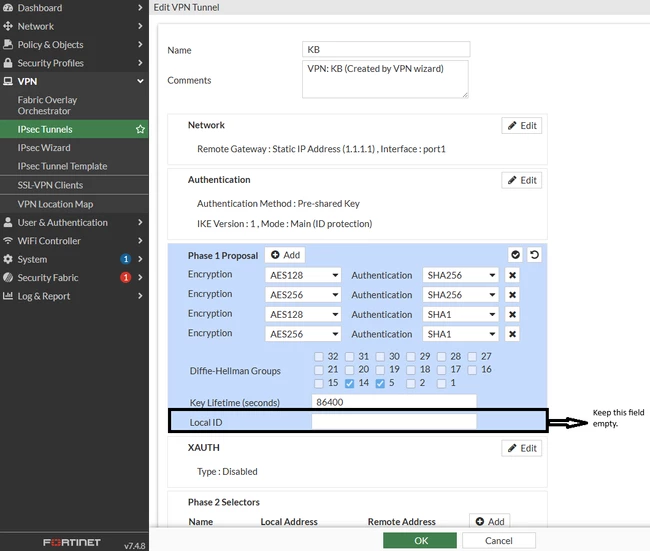 The Local ID option in the GUI cannot be seen when the Tunnel is created from the Wizard. In such cases, use the 'Convert to Custom Tunnel' option.
After configuring the FortiGate private IP address as Peer Identification on the Palo Alto firewall, the IPsec tunnel establishes successfully.
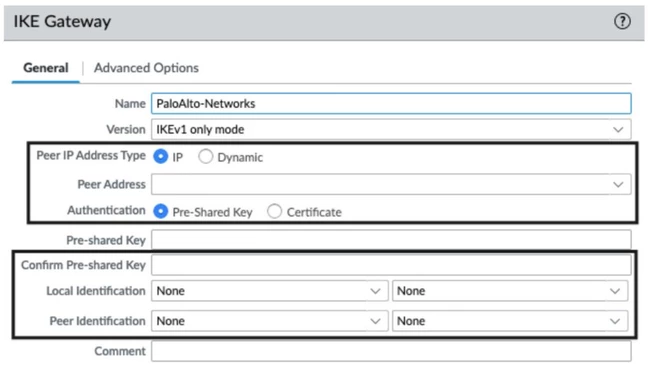
A private IP address refers to the IP address assigned to the underlying interface on which the tunnel is built on the FortiGate firewall. For example, if the tunnel is configured on interface port1 of the firewall, then the IP address of port1 can be used as the peer identification on the remote firewall (Palo Alto Firewall).
Related article: Technical Tip: Configuring IPSec tunnel between FortiGate and Palo Alto | 




