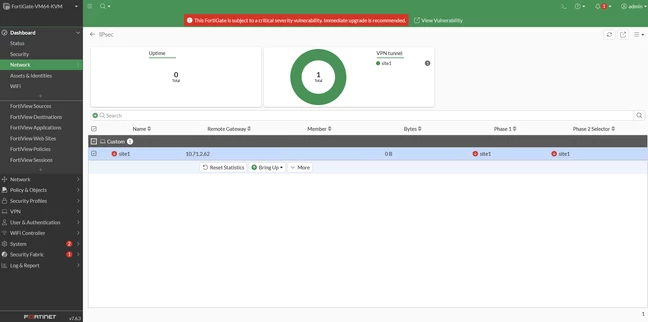
 The following errors are seen on the IKE debug. 2026-01-20 05:45:00.856557 ike V=root:0:site1:934: generate DH public value request pending
2026-01-20 05:45:00.923568 ike V=root:0:site1:934: compute DH shared secret request pending
Change the IPsec VPN tunnel PSK secret to have at least 14 characters to fix the IPsec VPN tunnels that are down.
Starting on FortiOS v7.6.1 with FIPS enabled, the IPsec VPN PSK secret needs to be at least 14 characters. This also affects dialup IPsec tunnel.
How to change the PSK secret on an IPsec VPN tunnel via the CLI:
config vpn ipsec phase1-interface
	edit "VPN tunnel name"
		set psksecret ****
	next
end
Starting from FortiOS v8.0.0, a PSK secret length less than 14 will not be accepted.
Lab-FGT (dialup) # set psksecret 123456
Minimum psksecret length in FIPS-CC is 14.
node_check_object fail! for psksecret 123456
value parse error before '123456'
Command fail. Return code -651
| 




